
Three llama.cpp advisories deserve attention from teams that import model-related files: CVE-2026-126974, CVE-2026-126975 and CVE-2026-126976. Their Zero Day Initiative advisories were publicly released November 13, 2026; their appearance in a November 18 advisory feed is not a new disclosure date. The operational task is to establish which parser fixes exist in the binary that loads your files, including optional multimodal and control-vector paths.
A GGUF label does not identify one loader
ZDI-26-975 describes integer overflow in GGUF parsing, while ZDI-26-976 describes inadequate length validation before a heap-buffer copy. Both link upstream pull request 31336. ZDI-26-954, for CVE-2026-126976, describes integer overflow when parsing audio multimodal projector GGUF data and points to a separate commit.
The advisories describe file-opening or related user interaction requirements and execution in the affected process’s context. They do not establish that every Internet-facing inference request can trigger every parser. Map how model artifacts actually enter your deployment: operator-selected files, an import service, a downloaded projector or another supported workflow. Treat a server-side automated import as its own exposure question.
Read the patches as separate evidence
| Upstream reference | Changes visible in the source | What to verify downstream |
|---|---|---|
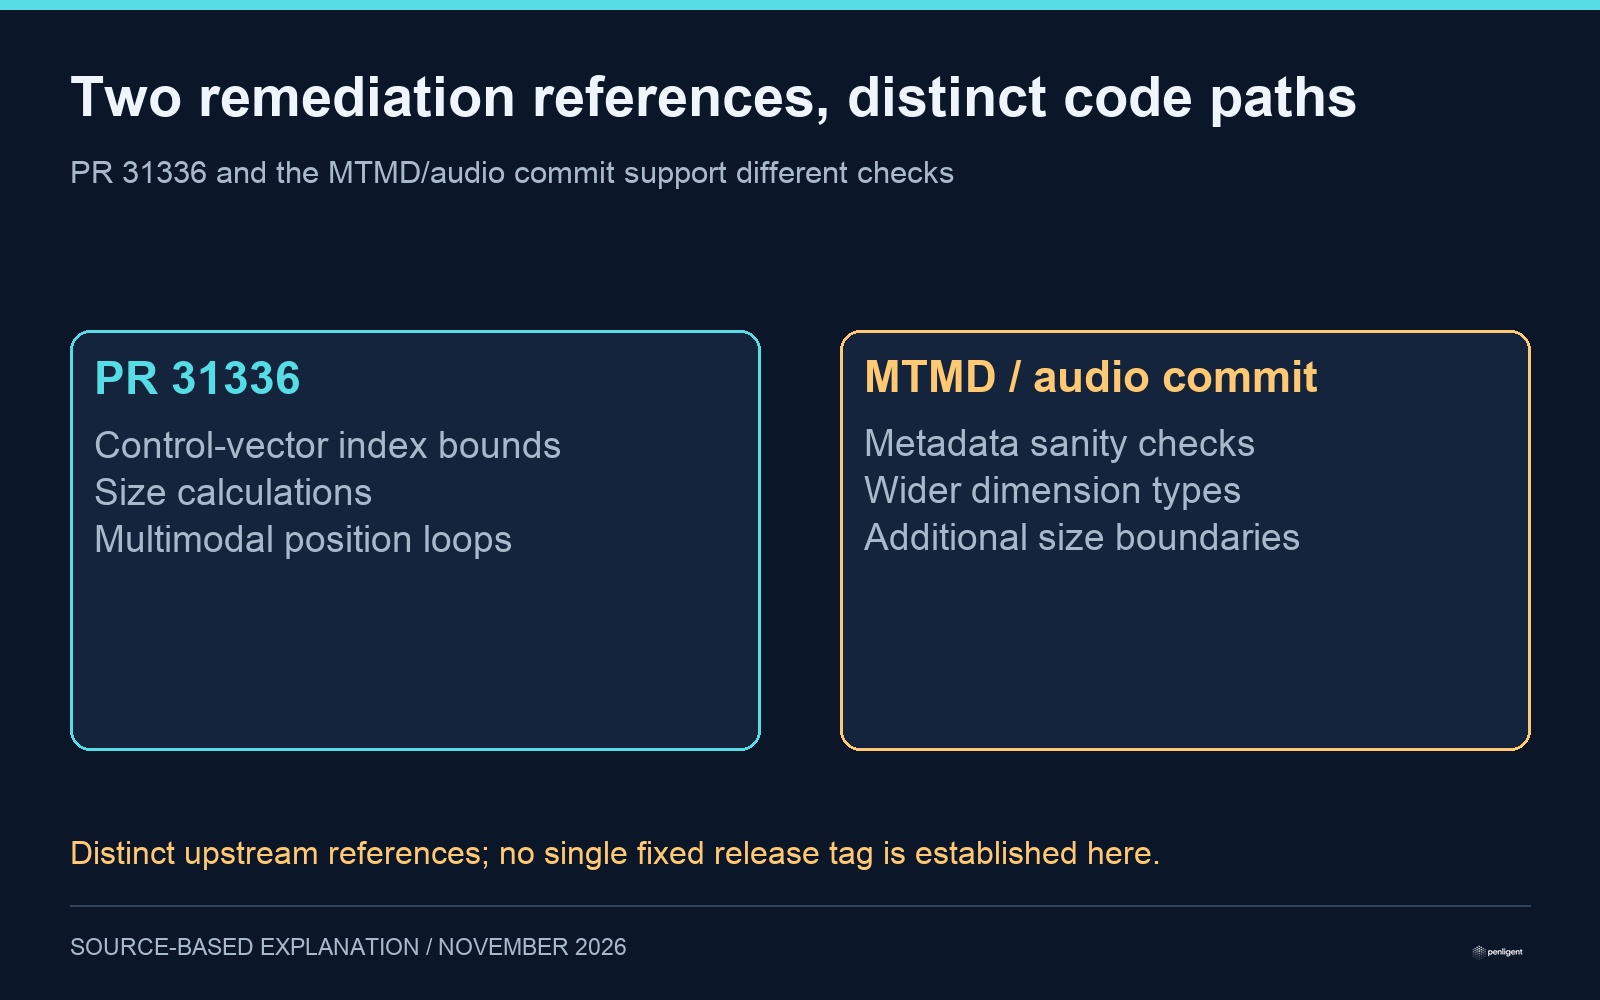
| PR 31336 | Control-vector layer index bounds, size calculations and multimodal position-loop bounds | The shipped build includes the linked merge or equivalent backport for the used paths |
| Audio and MTMD commit | Metadata sanity checks, wider dimension types and additional size boundaries in multimodal processing | The projector-loading build contains these distinct changes |
This comparison is deliberately narrower than a claim that one bounds check fixes all GGUF parsing. The first pull request’s title and body describe control-vector and M-RoPE work; the audio commit changes different code. An advisory link identifies a remediation reference, but does not justify assigning every changed line to a specific CVE without further maintainer evidence.
We did not establish a first fixed release tag for all three issues from the reviewed references. For a packaged application, obtain the supplier’s build or backport evidence. For a source build, record the exact revision and whether both relevant change sets are included. A recent-looking application version or a successful model load is insufficient evidence.
Keep a model-admission record that includes the parser
Use an admission record for each approved artifact class. The following fields are a proposed defensive method, not a report of a Penligent lab run.
| Artifact class | Admission evidence | Parser evidence |
|---|---|---|
| Base model | Approved origin, exact artifact digest and owner | Actual loader binary and build revision |
| Control vector | Separate approval and digest; relation to the intended model | Control-vector loading path and relevant bounds changes |
| Multimodal projector | Separate projector provenance and model compatibility | MTMD/audio parsing changes included in the running build |
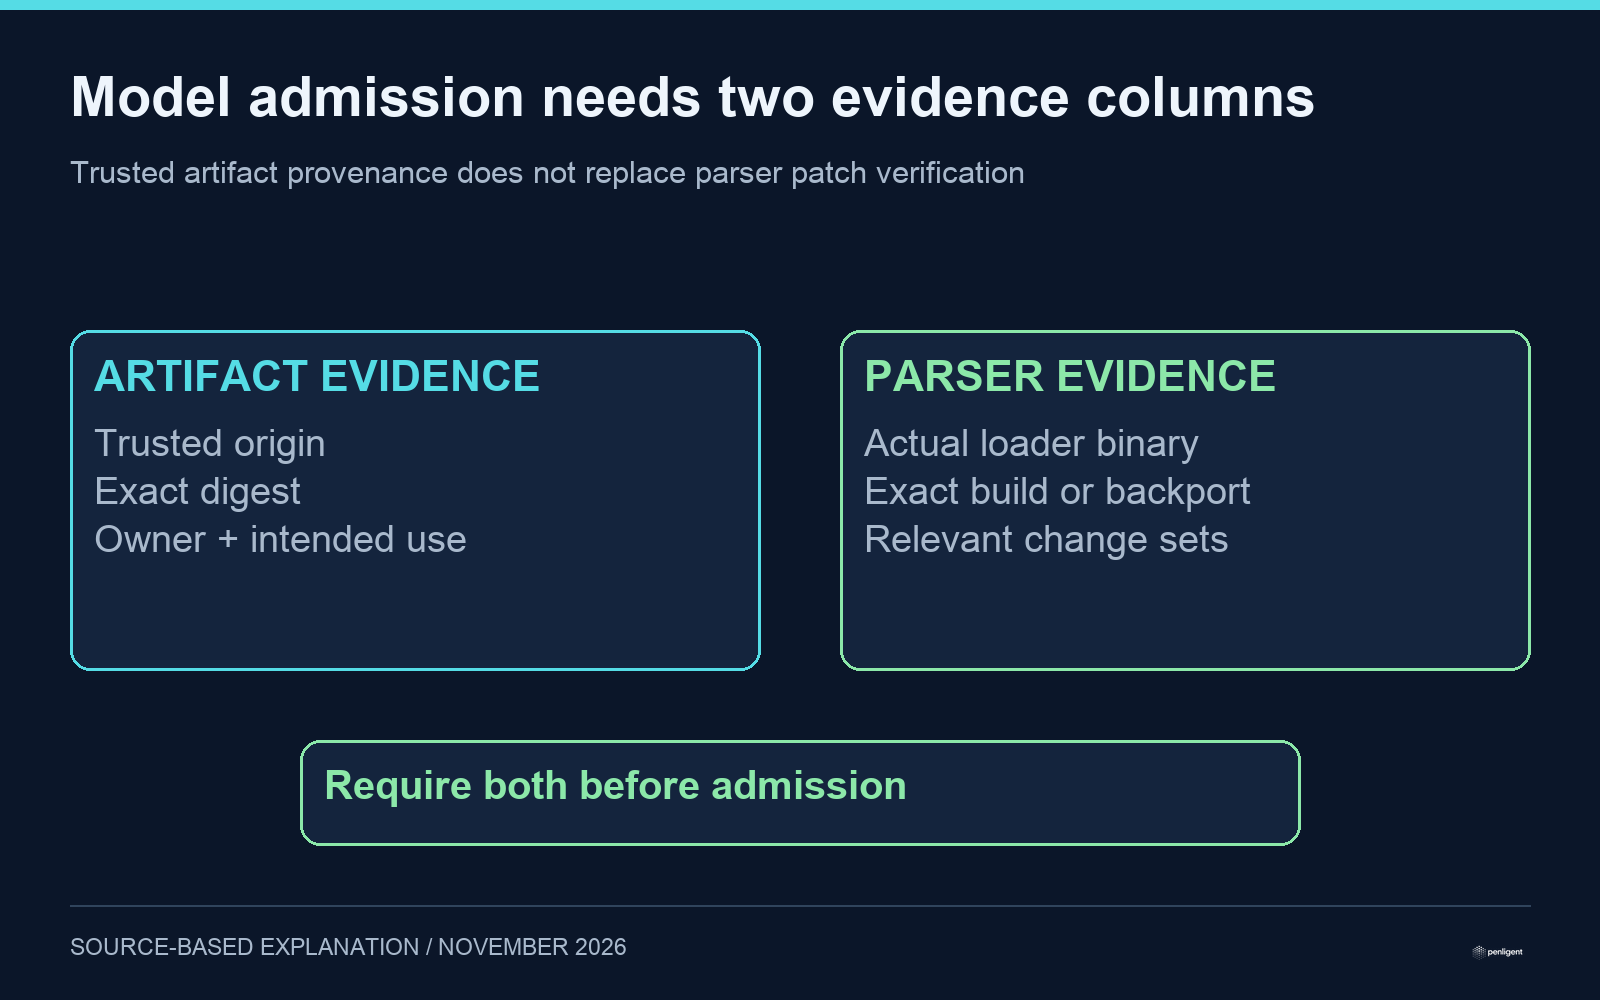
Provenance and parser safety answer different questions. A checksum proves you have the expected bytes only when the reference itself is trusted. It does not prove that a parser can safely handle those bytes. Conversely, a patched parser does not establish that an arbitrary model has an approved origin or acceptable behavior.
In a controlled environment, validate normal approved model and projector loading after the update. Keep artifact parsing in an appropriately restricted process and review which credentials, mounts and network routes that process can access. These are containment recommendations derived from the reported process-context impact, not claims that sandboxing is a vendor-certified workaround.
Retest the deployed distribution
Applications that embed llama.cpp may carry their own snapshot or modify the loader. Review the supplier’s remediation rather than assuming that updating a separate system copy changes the application. Retain the binary digest or supplier build evidence with the approved artifact list, and revisit the record when either the model path or the runtime changes.
Method: ZDI advisories and upstream source changes reviewed November 18, 2026. AI-assisted drafting received agent claim validation. Patch comparison and the admission record are our analysis; no malicious GGUF file was generated or executed. The following Penligent 3.0 video demonstrates a general product workflow.
 Arabic
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Turkish
 Hebrew