
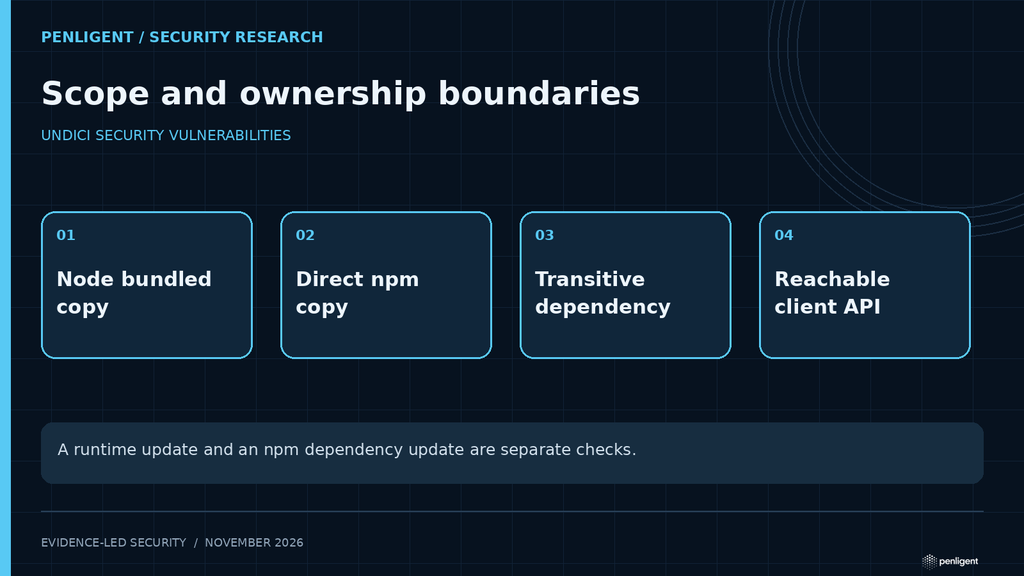
Undici published a concentrated set of security advisories in October 2026 affecting HTTP fetch, EventSource, WebSocket, TLS configuration, caching, Subresource Integrity and decompression. The first operational question is which Undici copy an application actually uses. Node.js includes a bundled implementation for its global fetch(), while many projects also install undici directly or receive it transitively.
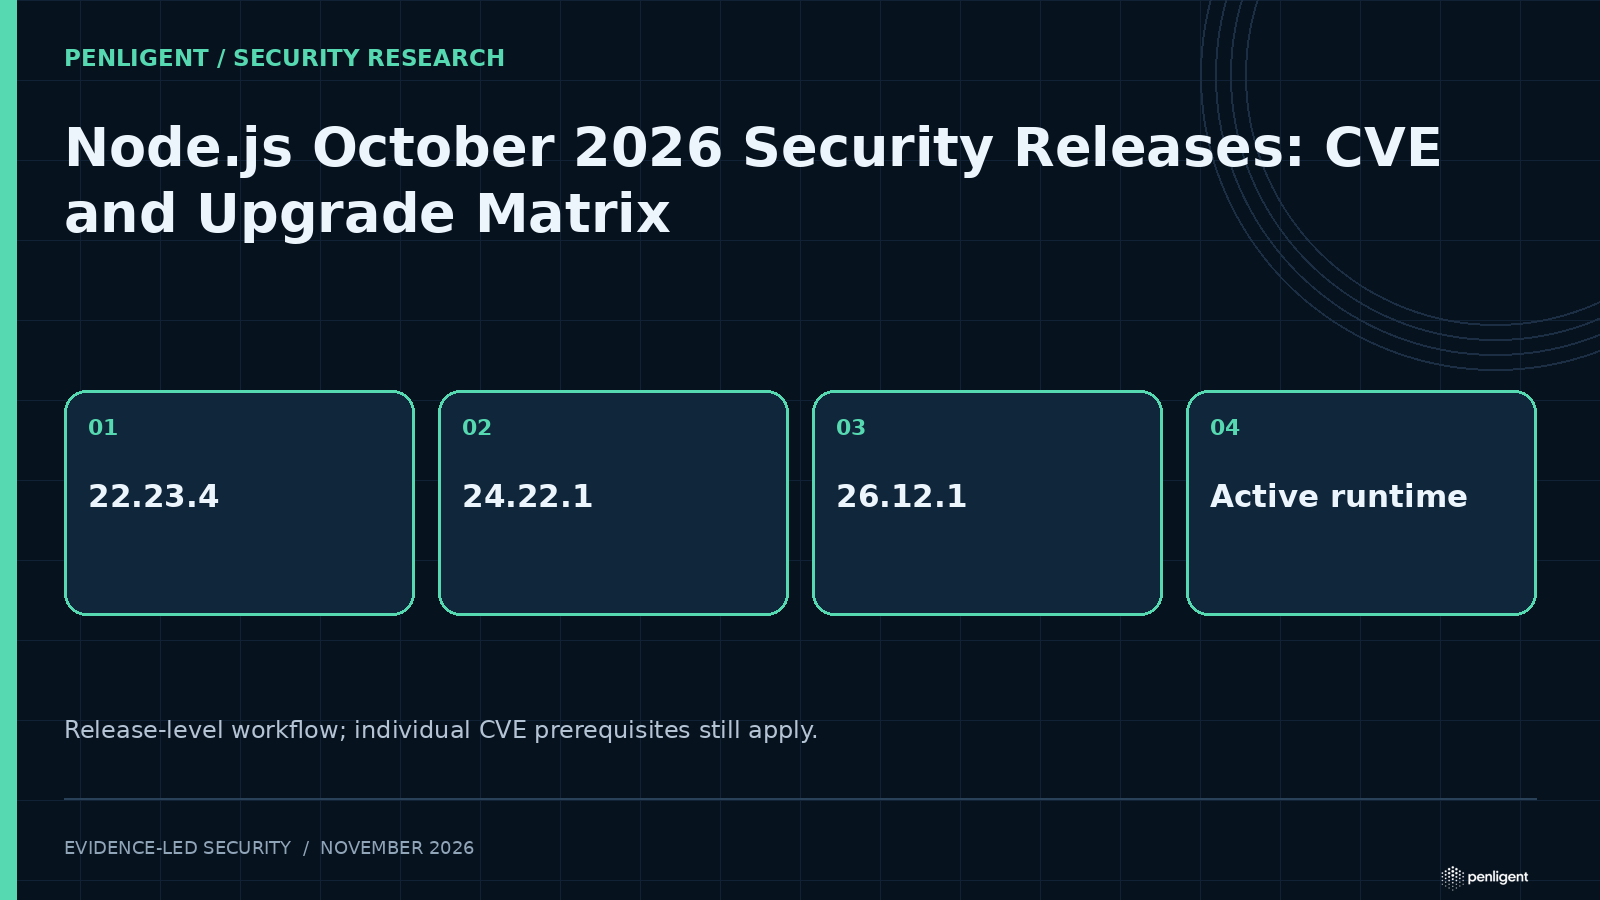
The maintained 6.x, 7.x and 8.x branches converge on fixed releases 6.29.1, 7.30.1 و 8.12.2 for the October 15 advisory set where those branches are affected. The HTTP/2 WebSocket handshake regression in 8.11.0 and 8.11.1 was first corrected in 8.11.2 and is also superseded by 8.12.2. Always check the individual Undici advisories for the exact affected range.
Group the vulnerabilities by reachable feature
| الميزة | Security outcome | Exposure condition |
|---|---|---|
fetch() decompression | Process termination from unhandled errors | An untrusted server controls malformed or excessive content encodings |
EventSource | Unbounded retained parser state and memory exhaustion | The application maintains an SSE connection to a malicious or compromised peer |
| WebSocket over HTTP/2 | Unhandled stream error and process termination | A malicious server fails the handshake and destroys the connection |
| Redirect-aware caching | Cache poisoning or cross-user disclosure | Shared cache keys and cross-origin redirects interact unsafely |
| TLS Agent options | Certificate-validation policy bypass | Security-relevant TLS options are not carried into the active connection |
| TLS 1.2 renegotiation | Availability loss | A server changes certificates during allowed renegotiation |
| Subresource Integrity | Integrity-policy bypass | Non-lowercase algorithm tokens are handled inconsistently |
Find the active implementation
node --version
node -p "process.versions.undici || 'bundled version not exposed'"
npm ls undici --all
npm explain undici

# Alternative package managers
pnpm why undici
yarn why undici
A clean npm ls does not prove that global fetch() is unaffected, because the runtime-bundled copy is not necessarily a package in the application tree. Conversely, upgrading Node.js does not update a directly declared dependency. Record both sources and the code paths that use them.
Choose the remediation path
- For direct dependencies, upgrade to the newest compatible fixed release in the supported branch, update the lockfile through the normal review process, and rebuild the deployment artifact.
- For transitive dependencies, upgrade the owning package or use a reviewed resolution only when the ecosystem supports it safely.
- For global
fetch(), deploy the Node.js security release containing the corrected bundled Undici. - For WebSocket clients that cannot upgrade immediately, the specific advisory allows disabling HTTP/2 with
allowH2: false; treat this as a temporary scoped workaround. - Do not rely on
try/catchalone for unhandled-stream vulnerabilities that terminate the process outside the caller’s expected rejection path.
Regression tests that match the risk
Use an isolated malicious test server controlled by the organization. Test that excessive Content-Encoding chains, early connection close, malformed WebSocket handshakes and bounded SSE streams are rejected without process termination or unbounded memory growth. For TLS policy, verify that the configured CA, hostname and verification options reach the actual connection. For shared caches, use two test identities and confirm redirected responses cannot cross the intended cache boundary.
Keep these tests defensive. They should validate rejection, resource bounds and policy propagation, not scan third-party services or attempt to extract another user’s data.
Prove the deployed version
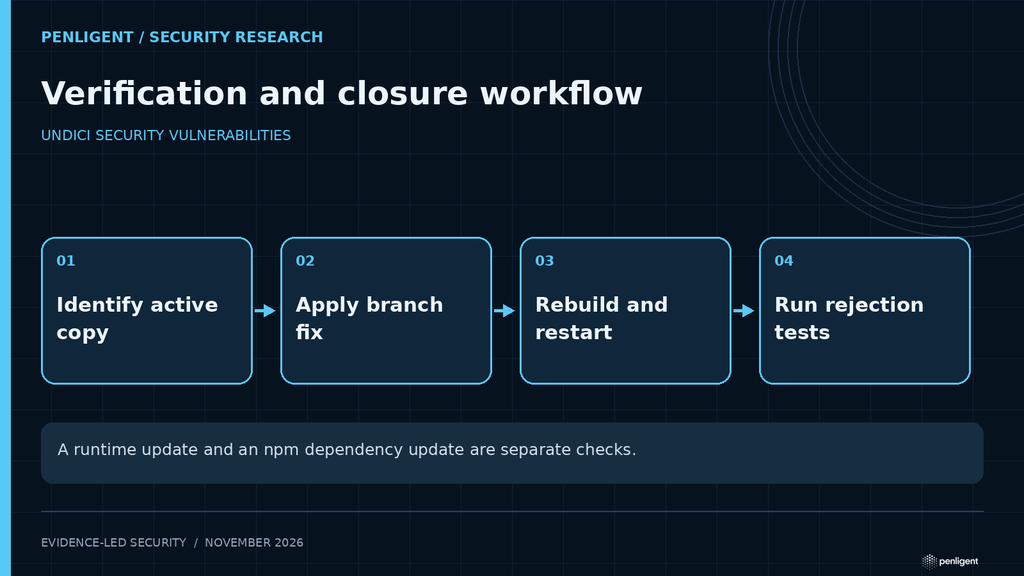
After the dependency or runtime change, rebuild containers, serverless bundles and packaged applications. Capture the image digest or artifact checksum, Node.js version, resolved Undici package version, deployment time and process restart. A fixed lockfile in source control is not evidence that production loaded it.
الخاتمة
Undici’s October 2026 security work spans several independent client features. Identify bundled and package copies separately, upgrade the applicable fixed branch, rebuild every deployment artifact, and run feature-specific rejection tests. Close the finding only when the active process and deployed dependency graph both reflect the corrected code.
 Arabic
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Turkish
 Hebrew