
Last updated: November 4, 2026.
API penetration testing services should be evaluated by the authorization and workflow decisions they can prove, not by endpoint count alone. A useful engagement tests how identities obtain tokens, which objects each identity can reach, how state changes across a transaction, and whether the final report gives developers enough evidence to reproduce and fix the issue.
Automated discovery is valuable for inventory, schema checks and repeatable baseline tests. It does not replace role-aware testing of object ownership, tenant boundaries, approval steps, pricing rules, rate controls or asynchronous workflows. Buyers should require both machine-assisted coverage and accountable review of the paths that matter to the business.
For the assessment framework, consult OWASP API-Sicherheit Top 10 and map the relevant guidance to the actual environment and authorized scope.
Define the API attack surface before testing
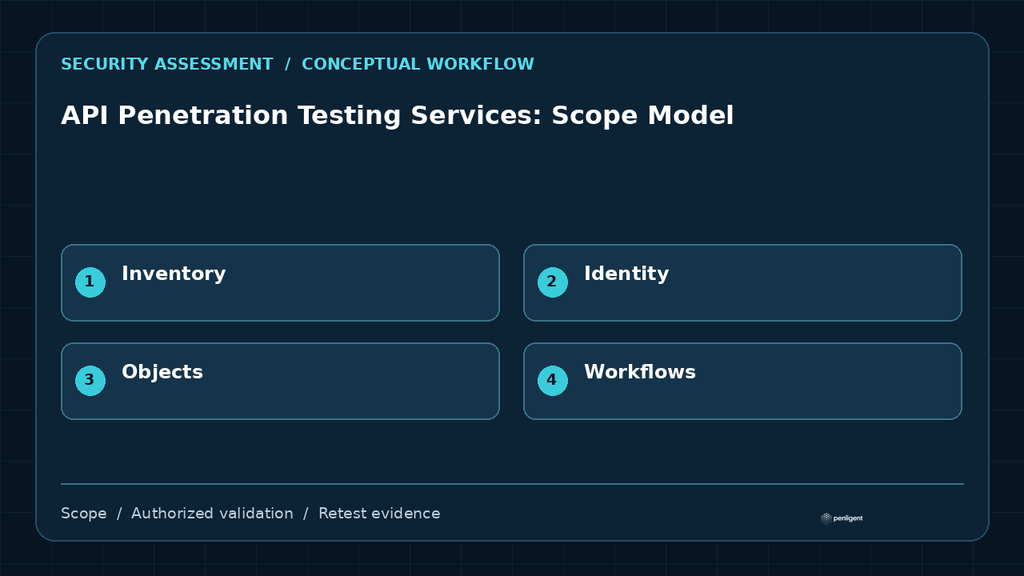
Start with the deployed interfaces, not only a source repository or one OpenAPI document. Include public and private REST or GraphQL endpoints, mobile backends, web application APIs, partner integrations, webhooks, upload and download services, administrative APIs and any version that still receives traffic.
| Scope layer | Evidence to provide | Testing decision |
|---|---|---|
| Inventory | Hosts, base paths, versions, schemas and gateways | Identify undocumented and legacy interfaces |
| Identity | User roles, service accounts, token types and test credentials | Build an authenticated role matrix |
| Objects | Tenant-owned records, identifiers and ownership rules | Test object- and property-level authorization |
| Workflows | Create, approve, refund, invite, export and delete paths | Test state transitions and business rules |
Validate the API paths scanners miss
Connect authenticated scope, tool output, manual investigation and retesting evidence in one authorized application-security workflow.
What a serious API test should cover
OWASP API Security guidance highlights recurring risks such as broken object-level authorization, broken authentication, unrestricted resource consumption, server-side request forgery and unsafe consumption of third-party APIs. The engagement should translate those categories into the customer’s actual objects, roles and integrations rather than treating the list as a generic checklist.
- Token issuance, refresh, revocation, audience and privilege transitions.
- Cross-user and cross-tenant access to objects, properties, exports and files.
- Mass assignment, hidden fields and administrative actions exposed through ordinary endpoints.
- Rate, quota and cost controls for resource-intensive or paid operations.
- Webhook authentication, replay handling and trust in third-party response data.
- Business sequences such as invitation, approval, refund, coupon, entitlement and account recovery.
Require evidence that developers can act on
A finding should name the tested identity, request sequence, affected object, expected control and observed result. Sensitive data should be minimized or sanitized, but the evidence must still show why the behavior is unauthorized and how to reproduce it in the approved environment.
| Deliverable | Minimum useful content |
|---|---|
| Scope record | Hosts, versions, roles, exclusions and test window |
| Finding evidence | Sanitized requests and responses, identity context and affected workflow |
| Impact analysis | Data, privilege, tenant or transaction consequence |
| Sanierung | Control objective and implementation guidance without assuming one framework |
| Retest | Original case, corrected result, regression checks and closure status |
How to compare API pentest providers
Ask how the provider handles authentication, test data, production safety and rate limits. A low endpoint price can become expensive when the quote excludes role setup, business-logic paths, evidence review or retesting. The most useful proposal states what will be tested, what will not be tested, who approves risky actions and what constitutes a completed retest.
Validate the API paths scanners miss
Connect authenticated scope, tool output, manual investigation and retesting evidence in one authorized application-security workflow.
Questions buyers should ask
- Will every material role and tenant boundary receive test credentials?
- How are GraphQL, webhooks, asynchronous jobs and third-party integrations handled?
- Does the report include reproducible request evidence and a role/object matrix?
- Is remediation retesting included, and what evidence is delivered after closure?
Schlussfolgerung
Choose API penetration testing services that can connect endpoints to identities, objects and business state. The engagement is complete when the organization can explain what was tested, reproduce each material finding, verify the remediation and retain evidence that the corrected control is active.
 German
 English
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew