
CVE-2026-116779 crosses a boundary between delivering a SIP message and invoking FreeSWITCH administrative APIs. The maintainer advisory lists FreeSWITCH 1.11.2 and earlier as affected and 1.11.3 and later as patched. It also reports exploitation in the wild. Administrators need to assess each active SIP profile, because a general statement that SIP authentication or an inbound ACL is enabled does not settle this path.
The advisory was published October 28, 2026. CISA's KEV catalog added the CVE on November 9. Those dates describe disclosure and prioritization, not a new November 16 vulnerability. A KEV entry is an exploitation signal; it does not establish compromise of a particular telephone system.
Identify the message-to-command boundary
The maintainer describes an inbound SIP MESSAGE handler that interprets part of the destination user as a registered chat-protocol selector. A registered API chat interface can then pass the selected operation into FreeSWITCH's API execution machinery. Message-delivery interfaces and command-execution interfaces were not adequately separated.
The consequence is command execution with the FreeSWITCH process's privileges, potentially including configuration disclosure and call control. Do not automatically describe this as root execution: the service identity and local permissions matter. Additional loaded modules can change what the API can do, but removing one dangerous API is not the same as closing the selector boundary.
The practical inventory unit is a SIP profile on a specific active server. Record its intended peers, accepted message types, authentication settings, chat settings, running build and configuration activation. A cluster-wide configuration repository is useful input, but it is not proof that every process loaded the same profile revision.
Assess profile exposure without conflating the controls
The advisory says inbound chat is enabled unless a profile sets enable-chat=false; stock internal and external profiles leave it enabled. It also explains that the inbound ACL does not cover MESSAGE. Tightening that ACL alone therefore does not establish that the vulnerable path is unreachable.
| Control or observation | What the maintainer says it changes | Remaining question |
|---|---|---|
| MESSAGE authentication | Requires an account where enforced | Can an ordinary account still reach the API selector? |
| Removal of empty-password accounts | Removes one route to authentication | Does the message-to-command path remain? |
enable-chat=false | Disables inbound MESSAGE chat on that profile | Can the service operate without that chat function? |
disable_system_api_commands=true | Removes the system API | Are other command-capable APIs still reachable? |
| Patched protocol gate, left disabled | Blocks inbound selection of the API chat protocol | Is the corrected build active on every serving profile? |
Use this table as a coverage comparison, not a recommendation to toggle production settings blindly. The profile owner must assess call and messaging dependencies and use the supported deployment procedure. A mitigation's business effect belongs in the change record alongside its security effect.
Treat authentication as a prerequisite, not the fix
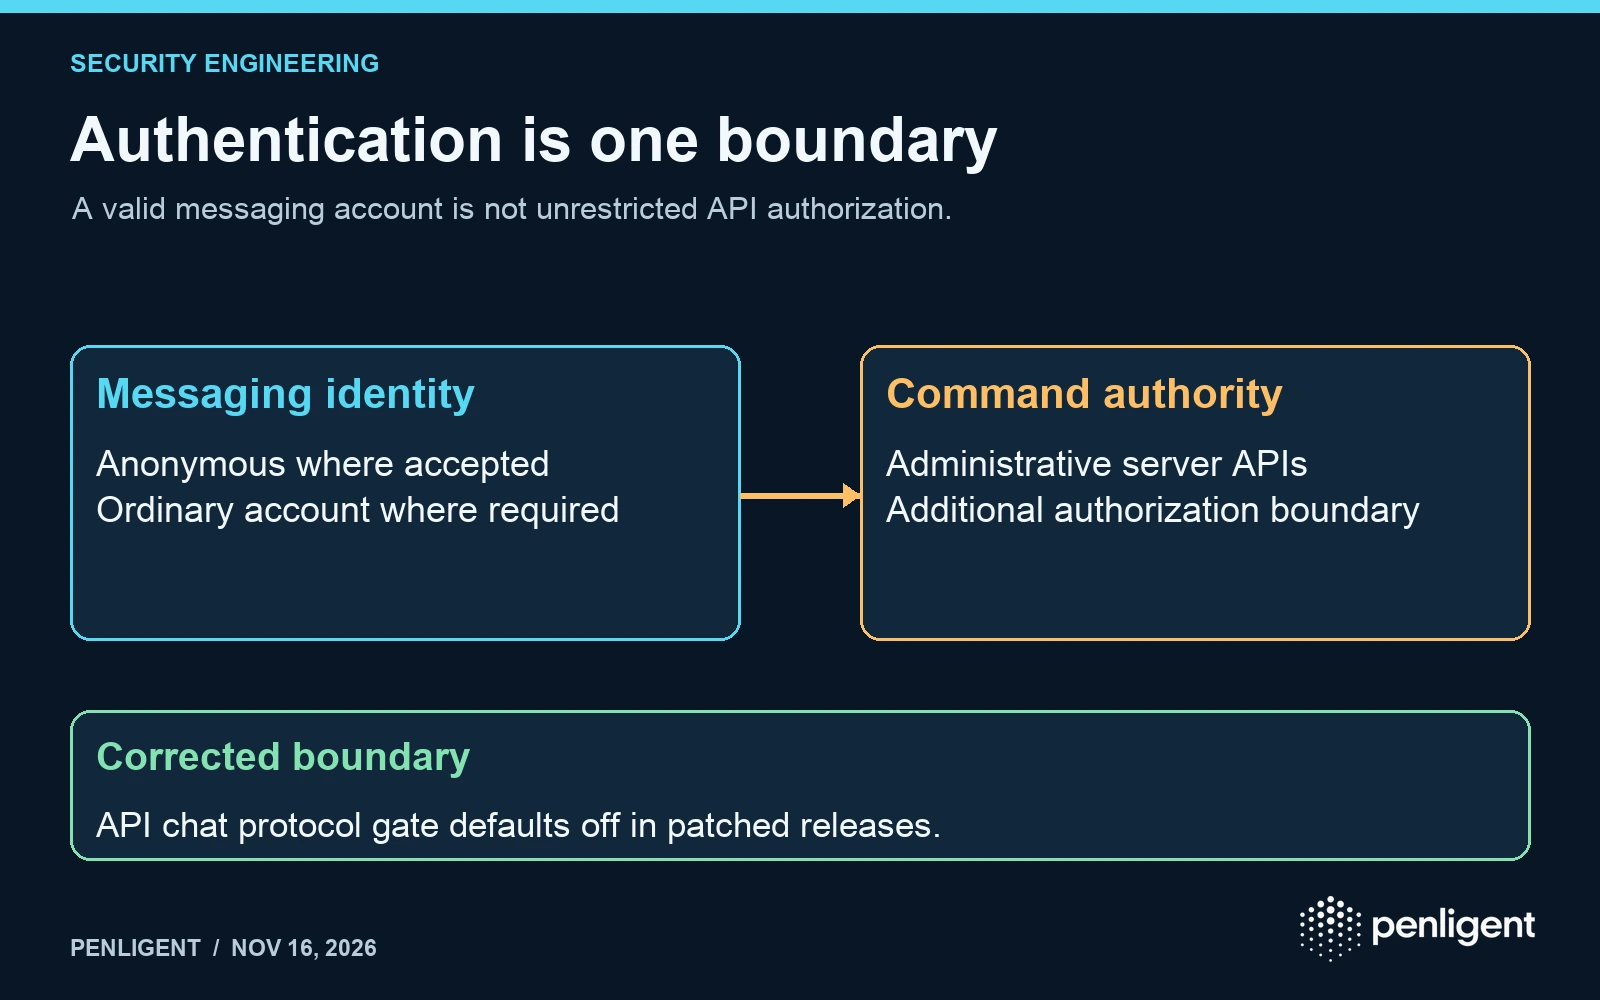
Where MESSAGE authentication is enforced, the maintainer says a normal registered account is sufficient to reach the vulnerable behavior. The issue is therefore not resolved by asserting that only authenticated extensions or trunks can send messages. Those identities normally have messaging or registration authority, not unrestricted server API authority.
The advisory also identifies stock directory examples without a password or password hash and explains the relevant empty-password behavior. Review the actual directory configuration with the service owner. Do not assume every production deployment retains those examples, and do not infer their absence from a single successful login test.
An exposure worksheet should distinguish anonymous network reachability, account authentication and command authorization. They answer different questions. Record unknown states explicitly, particularly when a hosted provider manages part of the SIP stack or profile configuration.
Verify the correction and its activation
FreeSWITCH 1.11.3 release notes list the new enable-chat-api-proto gate. The maintainer says it is off unless explicitly enabled and that a blocked selection receives a 403 response and a log entry identifying the source and requested command. These are documented expected behaviors, not results of a Penligent exploitation test.
Retain the supplying artifact, build identity and current release information. When a distributor backports the correction, use that distributor's package determination rather than rejecting the fix because its version string differs from upstream. The vendor's current supported update remains the maintenance target; a historical first-fixed version is a boundary reference.
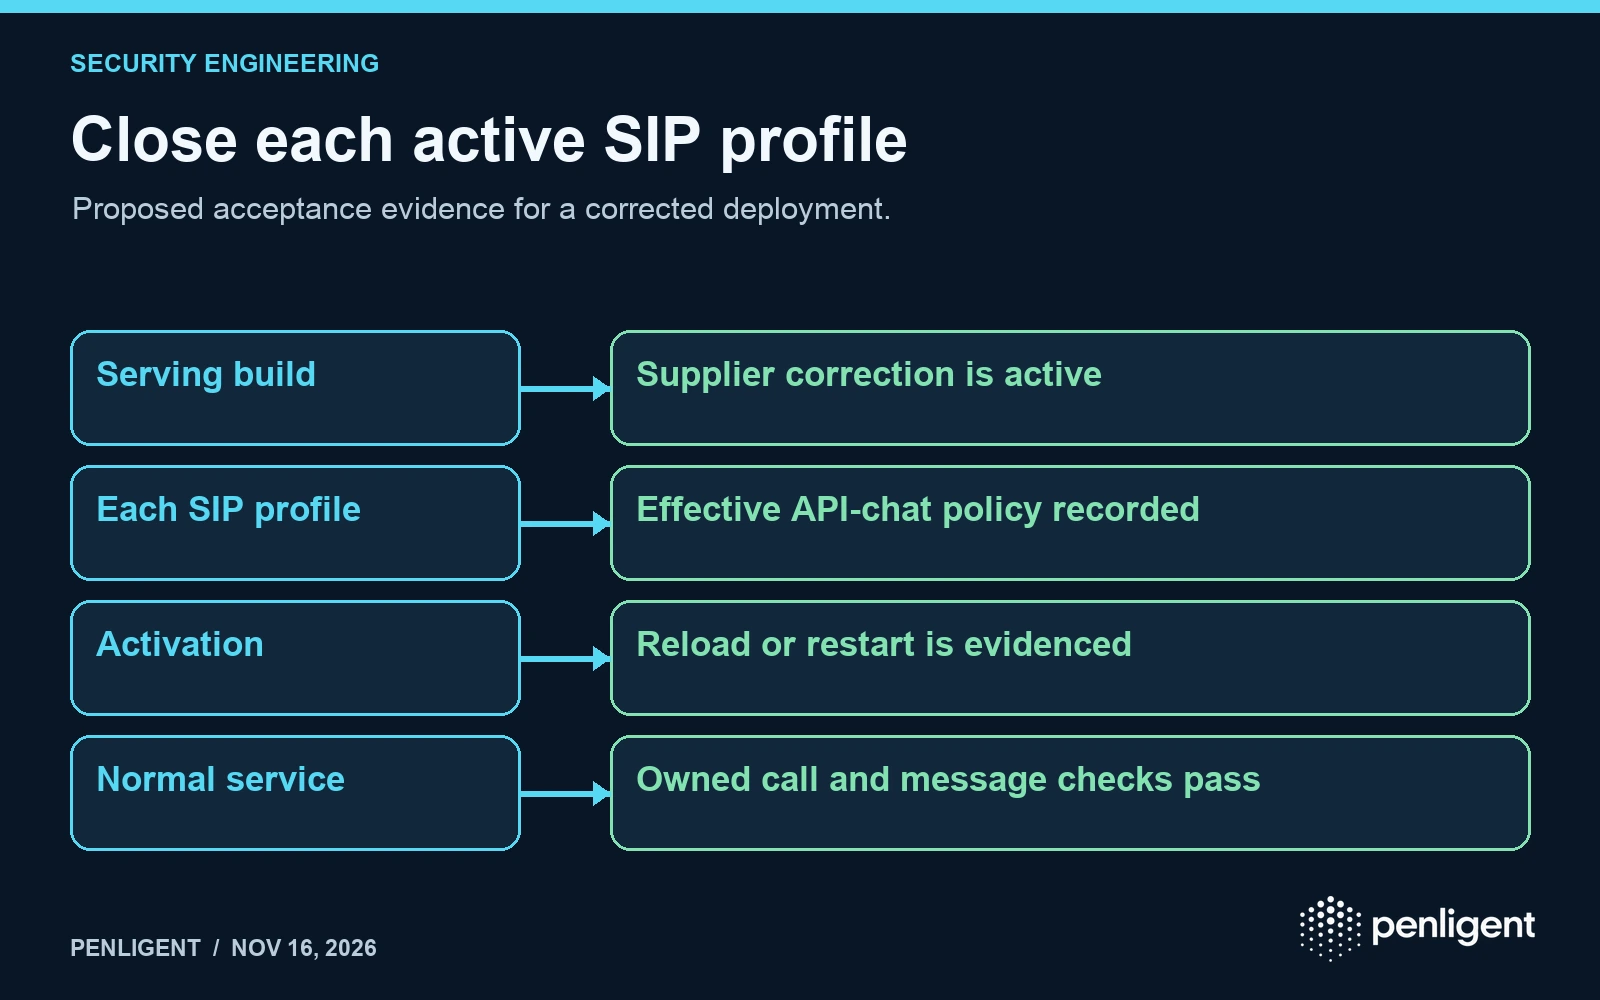
| Acceptance item | Evidence to retain | Keep unresolved when |
|---|---|---|
| Corrected software | Active build and supplier fix statement | Only an installation candidate is known |
| Intended protocol policy | Effective profile configuration | Another profile enables the API protocol unexpectedly |
| Configuration activation | Supported reload/restart and active profile evidence | Repository settings are the only observation |
| Rejection behavior | Approved nonproduction negative-control record | No agreed safe test was completed |
| Normal service | Authorized call and messaging checks | The mitigation breaks a required business function |
Do not replay an operating-system command or use a real subscriber's account to demonstrate the issue. A bounded staging validation can confirm that the corrected configuration refuses the prohibited protocol selection while preserving ordinary messages. Have the owner define the benign test and logging criteria using the current vendor documentation.
Investigate prior activity separately
Updating the process does not reconstruct historical SIP traffic or undo a previously executed command. Review available SIP, application, identity and host records over the plausible exposure interval. Correlate unexplained configuration, call-control, account or process changes with approved administrative activity.
Do not treat one error code as a historical compromise indicator. A corrected rejection log can show that a request was denied at that time. Missing entries can reflect retention or incomplete collection. Record the deployed logging coverage before interpreting an empty result.
If investigation shows unauthorized access to credentials or the host, involve incident-response owners and address the affected authority through its issuing system. Preserve evidence before cleanup where practical. Keep software patch closure and incident closure as separate decisions.
Close each active profile, not just the package ticket
A useful completion statement names the server, supplier build, active profiles, API-chat policy, activation record and normal-service result. It also states whether the historical review remains open. This makes the decision reusable when a standby, restored configuration or replacement node begins serving traffic.
Method: AI-assisted analysis prepared November 16, 2026 from the FreeSWITCH advisory, release notes and CISA catalog. The profile matrix is an original proposed validation method. No exploit message, production telephone system or customer host was tested.
Verwenden Sie die patch verification workflow to organize the handoff from an approved correction to its active process, expected behavior and coverage. Retain a separate acceptance record for each SIP profile.
General product workflow
The official Penligent 3.0 video illustrates general authorized testing. It does not demonstrate FreeSWITCH exploit coverage or certify a SIP deployment.
 German
 English
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew