
Last updated: November 4, 2026.
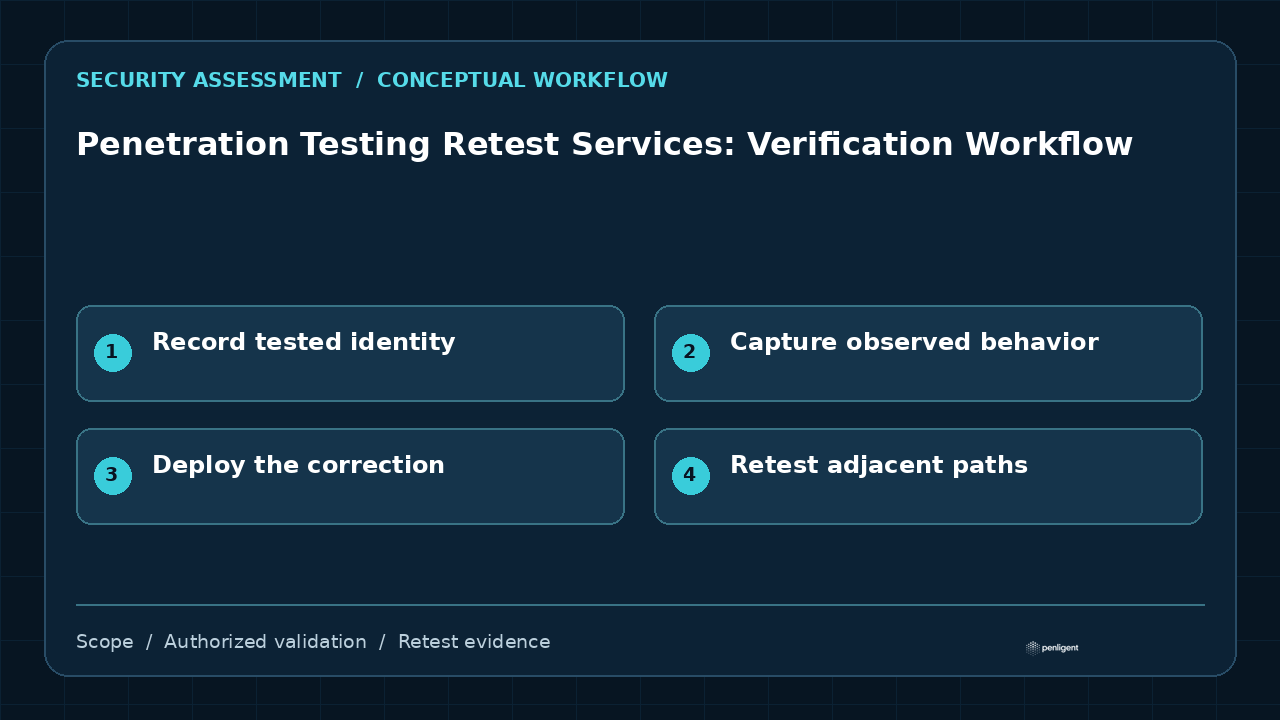
A penetration testing retest verifies that the deployed control changes the original security outcome. A pull request, ticket status or package update is not sufficient by itself. The corrected code must reach the tested environment, stale processes and images must be replaced, and the original request or attack path must no longer produce the finding.
Good retesting also checks the nearby paths most likely to preserve the weakness: another role, endpoint, tenant, protocol, cache, worker or legacy version. The goal is focused closure evidence, not an unbounded second engagement.
For the assessment framework, consult NIST SP 800-115 and map the relevant guidance to the actual environment and authorized scope.
Collect a retest-ready remediation package
Before scheduling, provide the original finding identifier, affected assets, deployed fix, environment, expected result and any changed endpoint or workflow. If the scope changed materially, decide whether the work is a retest or a new assessment.
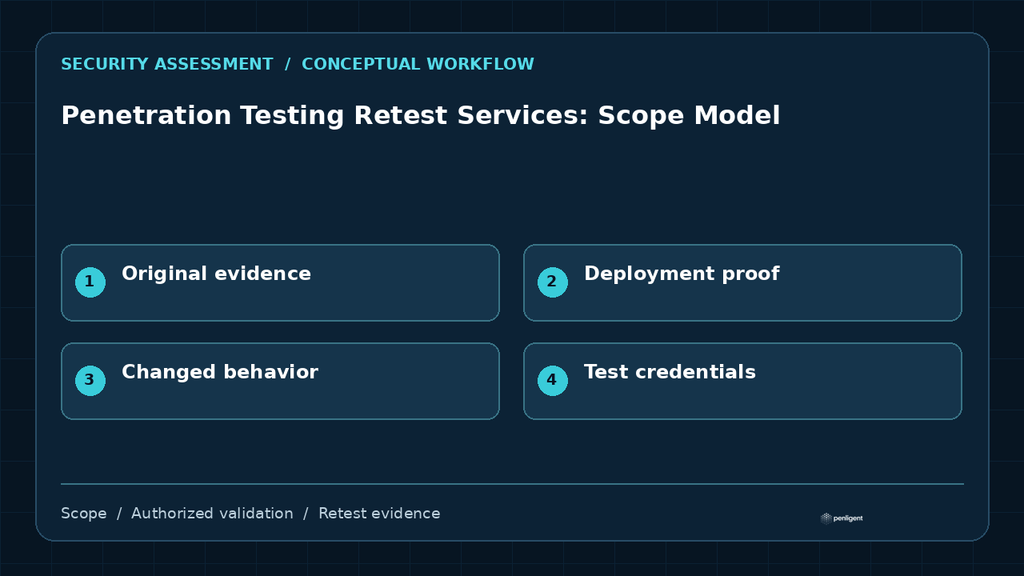
| Input | Warum das wichtig ist |
|---|---|
| Original evidence | Recreates the exact failed control |
| Deployment proof | Confirms code or configuration reached the target |
| Changed behavior | Defines the expected security result |
| Test credentials | Preserves the same role and tenant assumptions |
| Regression scope | Identifies adjacent cases worth checking |
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Verify runtime state before behavior
Confirm version, configuration, image digest, process start time or feature flag before repeating the exploit condition. This prevents false closure when the source is fixed but the tested instance still runs old code.
Use explicit closure states
A binary open/closed field hides uncertainty. Use statuses that communicate the evidence and remaining work.
| Status | Bedeutung |
|---|---|
| Fixed | Original and agreed regression cases no longer fail |
| Partially fixed | Impact reduced but a material path remains |
| Not fixed | Original behavior remains reproducible |
| Not retested | Required access, environment or evidence was unavailable |
| Risk accepted | Owner accepts the documented residual risk; this is not a technical fix |
Produce an auditable retest record
Record date, environment, tester, finding ID, deployment identity, exact cases, observed result and remaining limitations. Preserve enough sanitized evidence for developers, auditors and future regression testing.
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Questions buyers should ask
- Will the retest confirm the deployed runtime before testing behavior?
- Which adjacent roles, tenants, endpoints or versions are included?
- How are partial fixes and unavailable environments reported?
- Does the final report preserve both original and corrected evidence?
Schlussfolgerung
Retesting closes a finding only when the deployed system produces the corrected result. Require runtime proof, repeat the original case, check the agreed regression paths and use closure states that communicate uncertainty honestly.
 German
 English
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew