
CVE-2026-131857 describes a denial of service in Supergateway 4.2.0 through 4.2.2 when used in stdio-to-SSE mode. The CVE record says a crafted session identifier can reach a prototype-inherited value and cause an unhandled TypeError, terminating the gateway and attached MCP sessions. The immediate assessment is transport-specific: record the installed version, exposed listener and active output mode before assigning this finding to a deployment.
Session lookup needs an actual session object
En v4.2.2 source initializes the session collection as a plain object and looks up a request-supplied key. Its truthiness check does not by itself distinguish an owned session entry from an inherited JavaScript property. Code then expects a session transport. The source supports the lookup mismatch; the process-wide crash outcome is reported by the CVE record and original researcher.
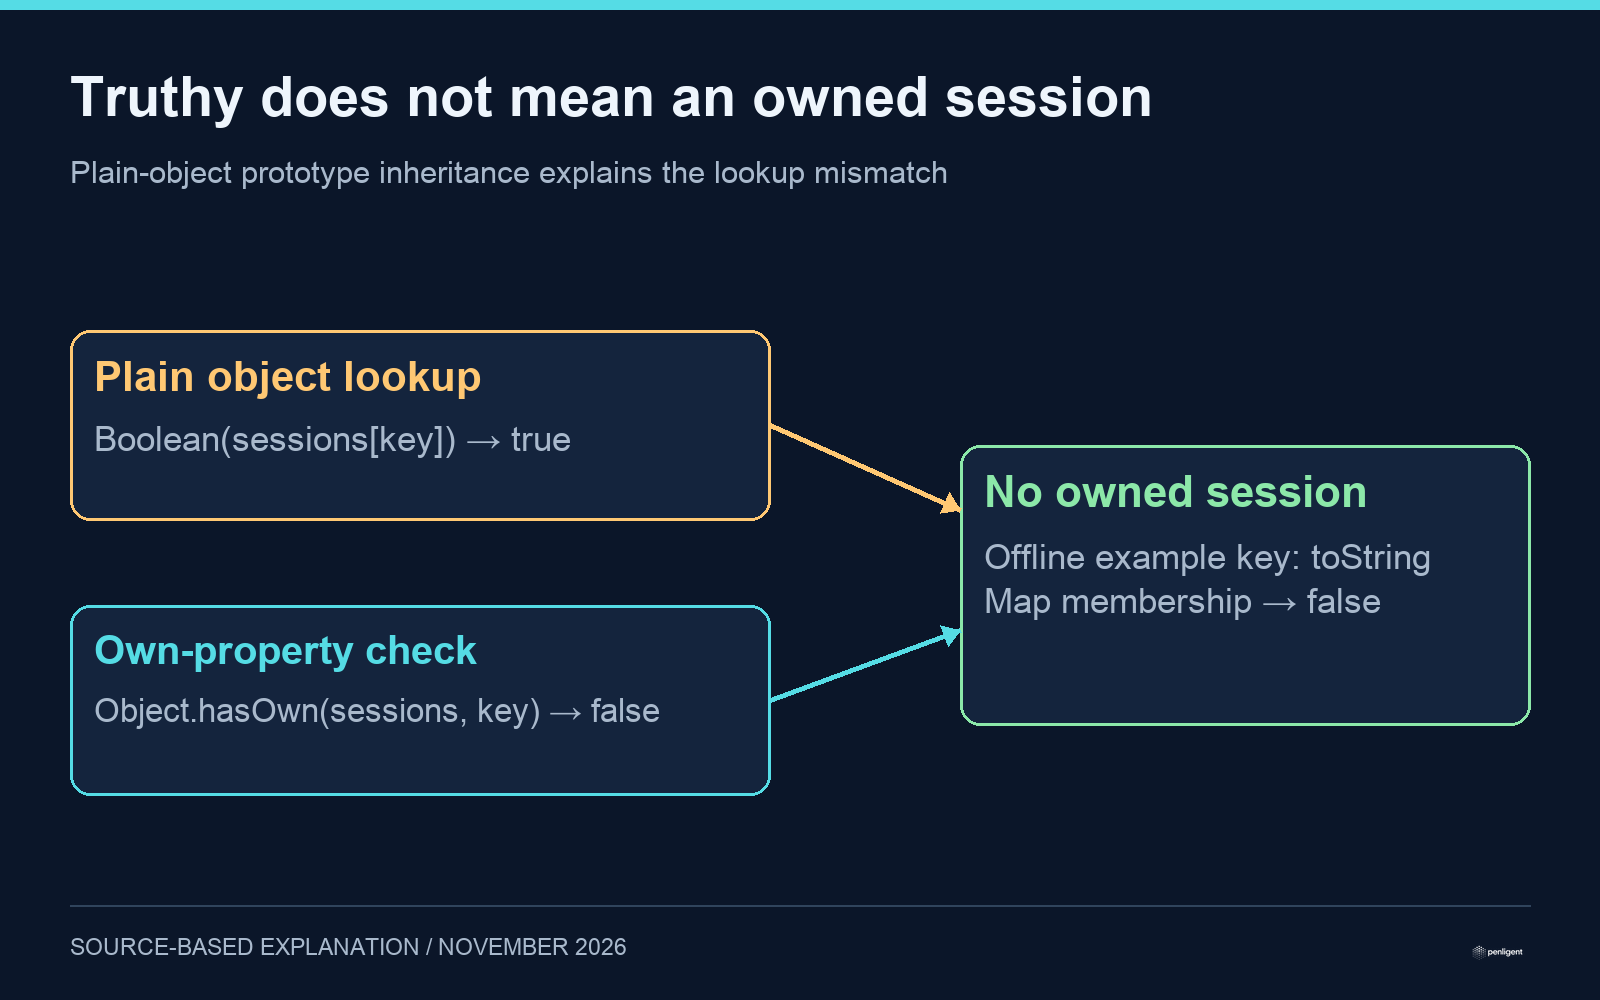
This offline JavaScript example illustrates that language property without a gateway, HTTP request or exploit. Run it only as a local language-behavior check:
const sessions = {};
const key = 'toString';
console.log(Boolean(sessions[key])); // true: inherited property
console.log(Object.hasOwn(sessions, key)); // false: no owned session
console.log(new Map().has(key)); // false: no map entry
The observed local output in our November 18 check was verdadero, falso, falso. This verifies object lookup behavior, not exploitation of Supergateway, a fixed gateway build or a network-access condition. A production fix also has to preserve transport lifecycle and error handling; replacing one expression in isolation is not a tested release.
A patch reference is a starting point, not acceptance evidence
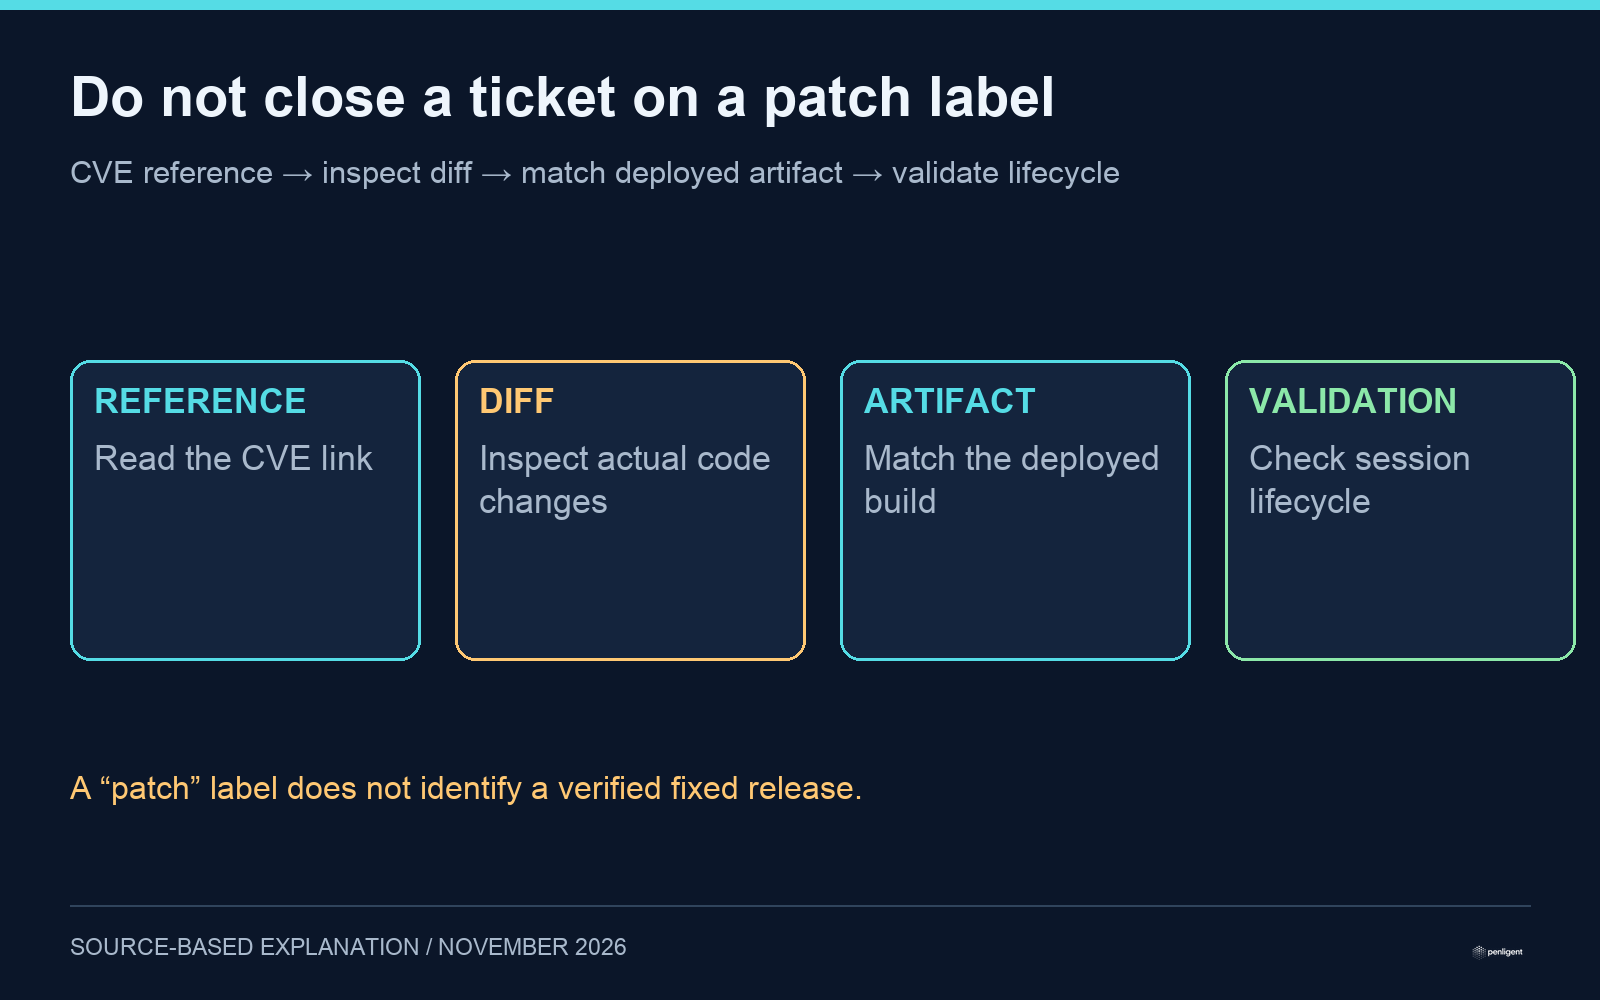
The CVE record labels commit e2254169 as a patch reference. At our review, that commit’s subject is “serve several config entries on one port,” and its change set is broader gateway configuration and mounting work. The reference alone does not establish the first fixed package version or prove that the vulnerable lookup has been removed from a deployed artifact.
The latest release listed by the upstream release API during our November 18 check was 4.2.2, which the CVE lists as affected. Its release notes describe a new warning for a network-reachable gateway without an API key and explicitly say clients are still served. A warning is observability, not an access-control change. We therefore do not name 4.2.2 as a fix or invent a later fixed tag.
Reduce exposure while keeping remediation unresolved
| Control or evidence | What it answers | What remains open |
|---|---|---|
| Listener restricted to the intended network boundary | Who can reach the gateway | The parser defect still exists in affected code |
| Supported API-key requirement and authorization review | Who can submit accepted requests through that path | Authentication is not proof of a code fix |
| Release or supplier evidence containing the actual session-handling correction | Whether the deployed artifact has the fix | Normal lifecycle and isolation still need an acceptance test |
| Monitoring restarts and session interruption | Whether service health changed | A restart alone does not attribute an event to this CVE |
In staging, test supported normal session creation, valid messages, expiration and rejected unknown identifiers using non-destructive inputs. Record gateway version, mode and expected rejection behavior. Keep a missing fixed-release confirmation visible in the remediation record instead of closing the issue on the strength of a commit label.
En researcher’s issue also describes a WebSocket concern. It has a different mode and impact. Do not treat that report as an additional capability of CVE-2026-131857 or imply that an SSE availability flaw automatically grants tool execution.
Method: CVE, tagged source, commit and release review checked November 18, 2026. Only the offline JavaScript property check was executed; no gateway was attacked. AI assisted drafting and agent validation. The Penligent 3.0 video below is a general workflow demonstration.
 Spanish
 English
 German
 French
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew