
Last updated: November 4, 2026.
PCI DSS penetration testing starts with an accurate cardholder data environment and the systems that can affect its security. A generic external scan does not answer whether internal paths, applications or segmentation controls allow access to in-scope assets.
PCI DSS requirements and reporting expectations depend on the organization’s environment and assessment method. Use the current PCI Security Standards Council documents and work with the responsible assessor. A penetration test report can support an assessment, but it does not itself certify compliance.
For the assessment framework, consult PCI Security Standards Council Document Library and map the relevant guidance to the actual environment and authorized scope.
Define the CDE and connected systems
Document where cardholder data is stored, processed or transmitted, plus systems connected to or capable of affecting that environment. Include identity, management, logging, software delivery, cloud services and third parties when they can change the CDE security posture.
| Asset class | Scope question | Pruebas |
|---|---|---|
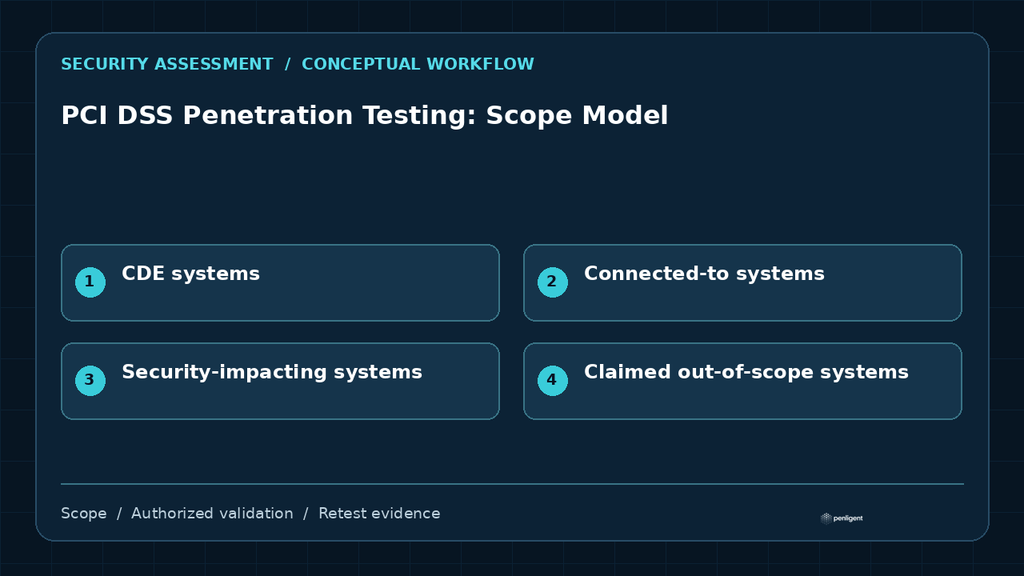
| CDE systems | Does the system store, process or transmit cardholder data? | Data flow and asset inventory |
| Connected-to systems | Can it communicate with or administer the CDE? | Network and identity paths |
| Security-impacting systems | Can it change code, policy, logging or access? | Administrative and delivery relationships |
| Claimed out-of-scope systems | What verified control prevents CDE access? | Segmentation design and test results |
Build evidence your remediation team can reuse
Keep scope, findings, reproduction details and retest results connected in an authorized assessment workflow. Compliance acceptance remains the assessor’s decision.
Cover external, internal and application paths
The test plan should state which external and internal attack paths are included and how custom or bespoke applications are assessed. The exact requirement mapping must follow the current PCI DSS version and assessor interpretation, but the technical work should still show how an attacker could move from an approved starting point toward cardholder data or security-impacting functions.
Treat segmentation as a testable security claim
Segmentation reduces scope only when the control actually prevents out-of-scope systems from reaching the CDE. Validate relevant network, identity, management and application paths. Record both permitted and blocked results and identify the configuration or enforcement point responsible for each outcome.
Plan remediation retesting and report handoff
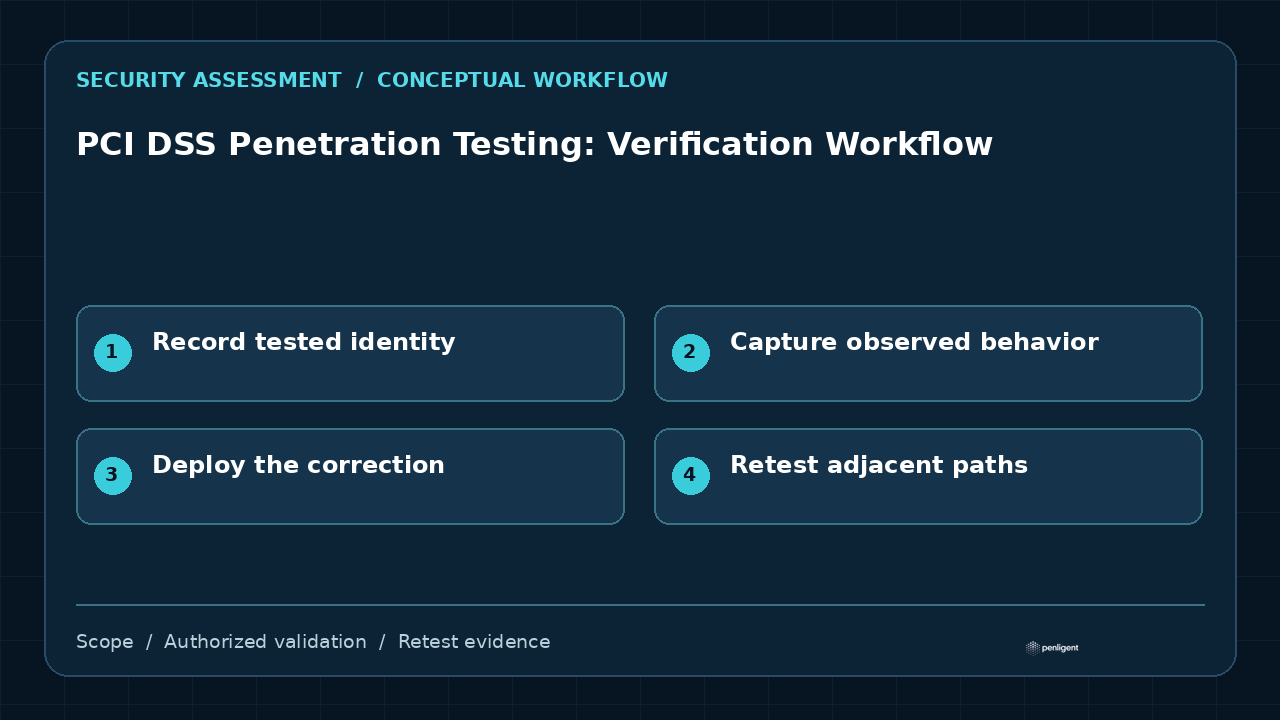
The report should identify scope, methodology, dates, assumptions, exclusions, findings, evidence and remediation status. Retest every material finding after correction and preserve closure evidence. If the environment changes materially, confirm whether the original scope and segmentation conclusions remain valid.
Build evidence your remediation team can reuse
Keep scope, findings, reproduction details and retest results connected in an authorized assessment workflow. Compliance acceptance remains the assessor’s decision.
Questions buyers should ask
- Who owns the authoritative CDE and data-flow inventory?
- Which connected and security-impacting systems are included?
- How will segmentation be tested across network, identity and management paths?
- Does the deliverable support the responsible assessor without claiming automatic compliance?
Conclusión
PCI DSS penetration testing is useful when scope, attack paths and segmentation claims are explicit. The organization should be able to show what was tested, how access was prevented or obtained, how findings were fixed and why the current environment still supports the scope decision.
Sources and standards
- PCI Security Standards Council Document Library
- PCI SSC Penetration Testing Guidance
- NIST SP 800-115
 Spanish
 English
 German
 French
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew