
CVE-2026-68903 affects LLMKube through 0.8.28 and is fixed in 0.9.0. Les maintainer advisory describes unsafe local model-source handling that can expose files through the controller or node filesystem. The relevant attacker authority is the ability to write the namespaced Model and InferenceService resources used by the workflow. Namespace-scoped API permission does not by itself bound the filesystem authority of the controller that acts on those objects.
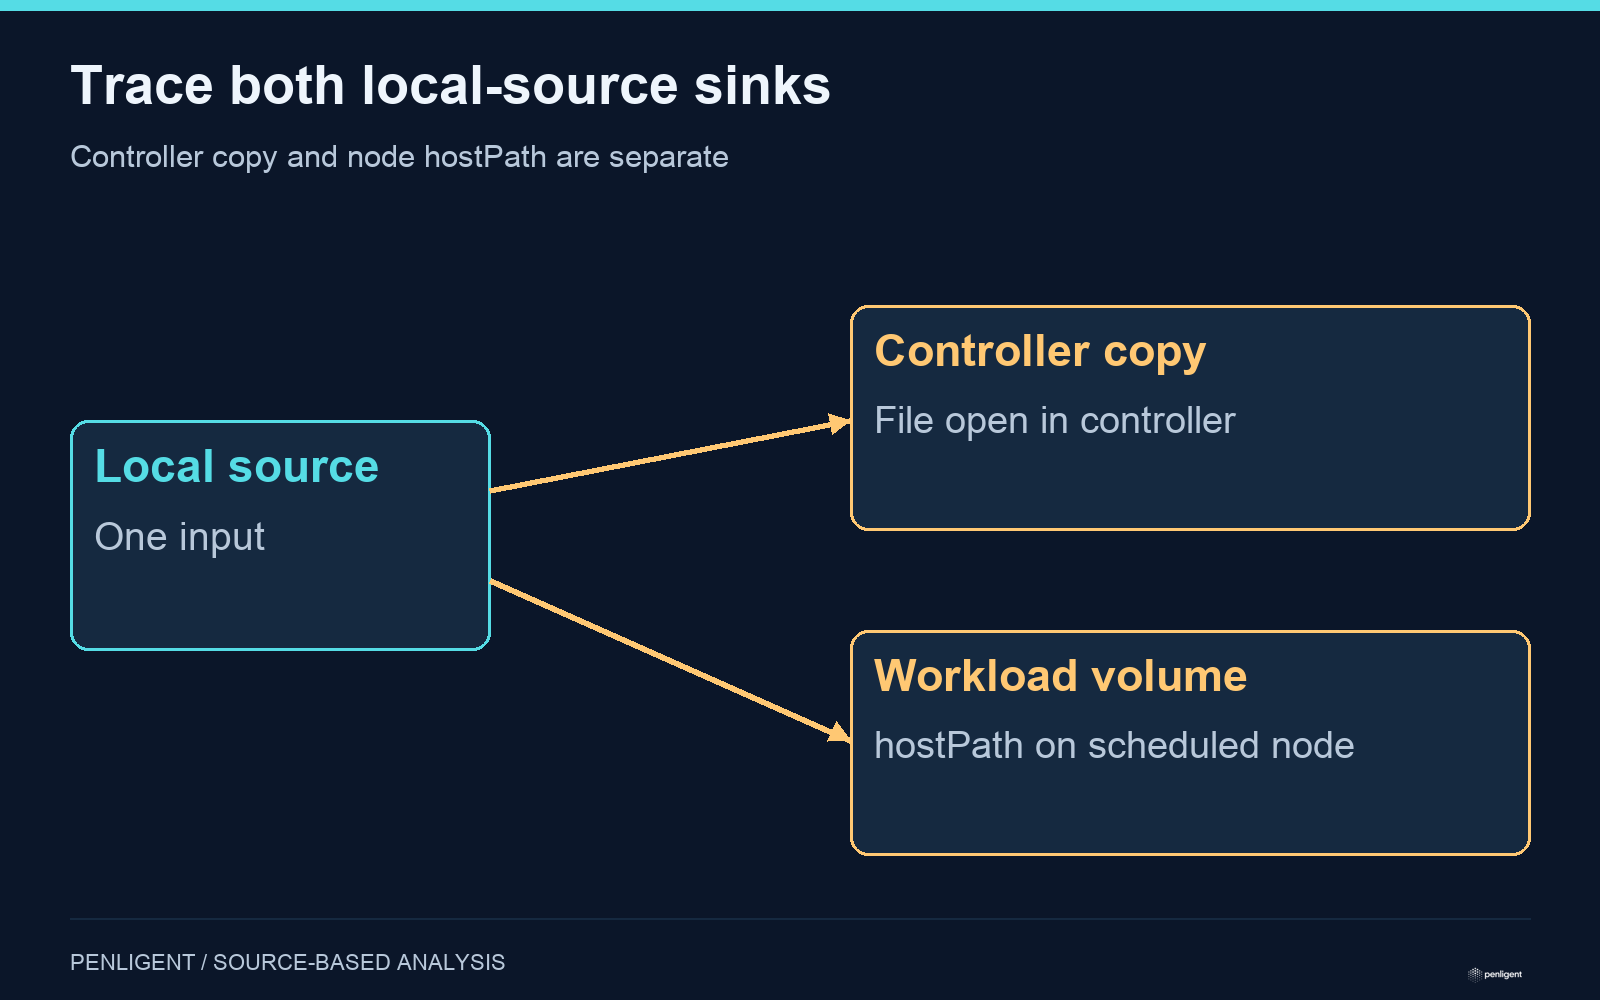
One model source can cross two filesystem boundaries
| Chemin d'accès | Privileged component | Question for the platform owner |
|---|---|---|
| Controller local copy | The controller opens a source path in its own filesystem | Can a tenant-supplied source select a file the controller can read? |
| Generated workload volume | The source becomes a hostPath volume in a workload | Can a namespaced object select a path on the scheduled node? |
These paths have different owners and evidence. A controller-container filesystem is not the same as the node filesystem, and a denied read in one path does not certify the other. Inventory controller mounts and service-account authority separately from node-local mounts and generated pod specifications. The advisory describes broader consequences when exposed credentials carry additional authority; it does not mean every controller automatically has identical cluster-wide permissions.
The patch changes the default for local model sources
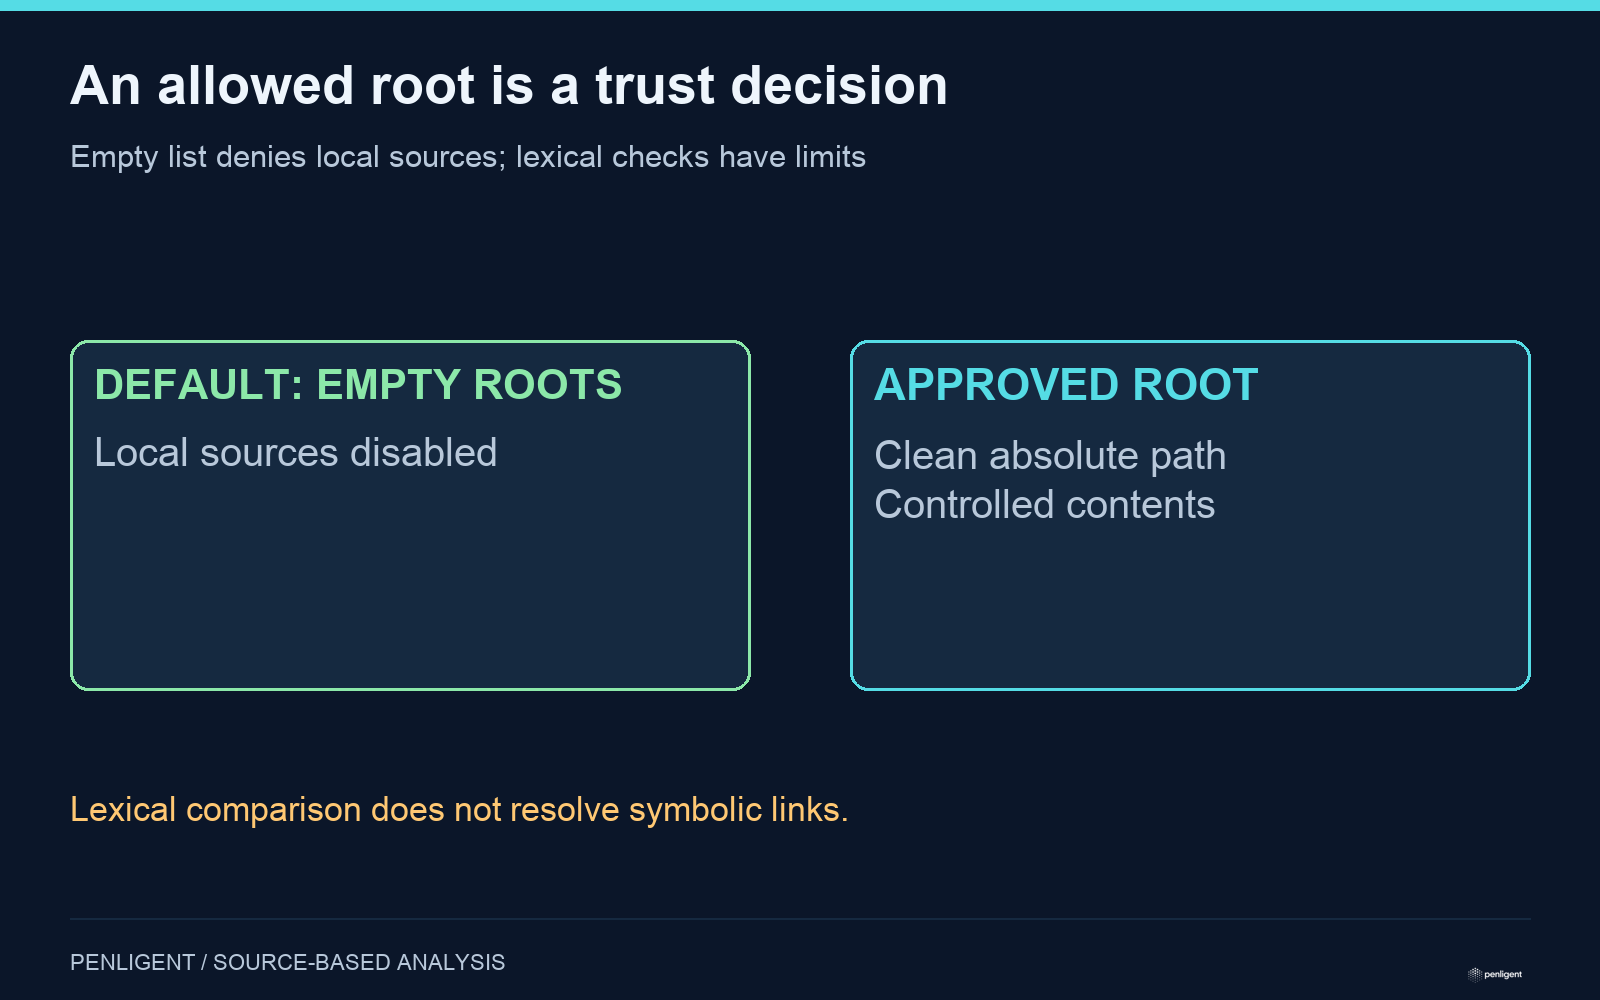
Les official change introduces modelSource.allowedHostPathRoots. An empty list disables local and hostPath sources. A permitted local path must be absolute, cleaned and inside an approved root. The same source classification and checks must protect both the controller copy and generated workload path.
The source explicitly describes the comparison as lexical: it cleans path components but does not resolve symbolic links. Allowlisting a directory therefore trusts the contents of that directory not to redirect elsewhere. This is an operator trust assumption, not a reason to claim the patch automatically rejects every possible symlink escape. Choose narrowly controlled roots and prevent untrusted writers from changing their contents or links.
The commit also aligns scheme classification case-insensitively and introduces guarded HTTP metadata and revalidation clients. Those changes show that model-source handling is broader than one file-open call. Do not assume a local-path allowlist alone describes every remote-source policy or that a local source and an HTTP source traverse the same execution component.
Review compatibility before restoring an old deployment policy
Existing air-gapped or node-local workflows may rely on local source paths that the new secure default rejects. Enumerate those models before rollout and decide whether to migrate to an approved storage source or allow a specific controlled root. Do not restore functionality by allowlisting the entire filesystem. Retain the reason, owner, write permissions and intended model files for each allowed root.
| Staging check using harmless fixtures | Expected evidence | Limit |
|---|---|---|
| No local roots configured | A local-source request is rejected by policy before a copy or volume is produced | A missing file error is not equivalent to policy rejection. |
| Fixture inside one approved root | The intended normal model path works | This does not approve arbitrary files elsewhere. |
| Fixture outside the root or a sibling directory | No copy or hostPath is generated | Exercise both controller and workload creation paths. |
| Changed source scheme or model revision | Classification and revalidation still apply the correct policy | An initial admission check does not certify later changes. |
Use non-sensitive temporary fixtures in an owned test cluster and the project’s regression cases. Do not point a Model resource at real service-account tokens, node credentials or private files for validation. The acceptance plan above is analysis of the source changes; no cluster was tested for this article.
Bind the policy to the running controller
Record the deployed controller image digest and version, chart values, effective allowed roots, CRD writers and the generated workload configuration. Verify the rebuilt controller is active before closing the change. If an affected installation accepted untrusted source objects, preserve relevant object history, controller events and workload specifications and assess the credentials reachable in that environment. Package remediation and historical exposure remain separate decisions.
The following Penligent 3.0 video is a general product workflow demonstration. It is not evidence of exploitation or proof that this vulnerability was remediated.
Methodology, November 19, 2026: AI-assisted drafting with agent verification against the linked primary records and source changes. The deployment decisions and proposed acceptance checks are analysis. No exploit was executed and no first-hand incident response is claimed.
 French
 English
 German
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew