
CVE-2026-97229: How a GitLab CI/CD Regex Vulnerability Became a CVSS 10.0 Remote Code Execution Risk
A regular expression is not something most security teams expect to become an entry point for a complete server compromise. It is usually treated as a small piece of configuration logic: something that matches branch names, filters conditions, or decides when a CI/CD pipeline should run.
That assumption becomes dangerous when the software interpreting the expression contains a memory-safety vulnerability.
On October 12, 2026, GitLab disclosed CVE-2026-97229, a critical remote code execution vulnerability affecting self-managed GitLab Community Edition and Enterprise Edition installations. The flaw received the maximum CVSS v3.1 base score of 10.0, reflecting the possibility of remote exploitation without authentication or user interaction.
The vulnerability originates in the CI/CD regular expression compiler. According to GitLab’s official security advisory, insufficient validation of specially crafted regular expressions could trigger an integer overflow and, under certain conditions, allow an unauthenticated attacker to execute arbitrary code on the GitLab server.
The location of the vulnerability is particularly significant. GitLab is not simply a code hosting platform. In many organizations, it sits at the center of software development, connecting source repositories, build pipelines, container registries, deployment automation, and cloud infrastructure.
Compromising the GitLab application server can therefore create opportunities that extend well beyond the original vulnerable component.
The important question is not merely whether an attacker can exploit a regular expression parser. It is what an attacker might gain access to after compromising infrastructure that helps an organization build and deploy its software.
What Is CVE-2026-97229?
CVE-2026-97229 is an integer overflow vulnerability in GitLab’s CI/CD regular expression compiler that can lead to remote code execution.
The vulnerability affects both GitLab Community Edition (CE) and Enterprise Edition (EE). GitLab credits security researcher joaxcar, who reported the issue through the company’s HackerOne bug bounty program.
| CVE identifier | CVE-2026-97229 |
| Sévérité | Critique |
| CVSS v3.1 | 10.0 |
| Type de vulnérabilité | Integer overflow leading to potential RCE |
| Affected products | GitLab CE and EE |
| Authentication required | No, according to the published CVSS vector |
| Vecteur d'attaque | Réseau |
| Official disclosure | October 12, 2026 |
| Versions corrigées | 19.2.8, 19.3.5, 19.4.2 |
Source : GitLab Critical Patch Release, October 12, 2026.
The official CVSS vector is:
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H
This describes a vulnerability with a network attack vector, low attack complexity, no required privileges, no user interaction, changed scope, and high confidentiality, integrity, and availability impacts.
These characteristics explain why GitLab assigned the vulnerability the maximum severity score. An attacker does not necessarily need an existing developer account, administrator permissions, or a victim clicking a malicious link to exploit the affected functionality.
However, the advisory also qualifies exploitation as occurring under certain conditions. The public description does not establish that every exposed instance can be compromised through an identical request or that a universal exploit works against every configuration.
That distinction matters when evaluating actual exposure.
Why This GitLab Vulnerability Is More Dangerous Than an Ordinary CI/CD Misconfiguration
Most CI/CD security discussions focus on unsafe pipeline permissions, malicious build scripts, exposed variables, or compromised build dependencies. Those are serious risks, but they usually involve a different trust boundary.
In a typical pipeline compromise, an attacker tries to make a runner execute commands it should not execute. The immediate execution environment is often a runner container, virtual machine, or shell executor configured for build tasks.
CVE-2026-97229 is different because GitLab describes potential code execution on the GitLab server itself.
That difference changes the security implications.
A GitLab runner may be isolated from other internal systems, depending on the deployment. The GitLab application server, by contrast, often has access to persistent application data, repositories, internal services, and credentials required for normal operations. Its exact privileges vary substantially between installations, but the potential blast radius can be larger than that of an isolated build job.
Consider an organization that uses a self-managed GitLab instance for several engineering teams. The platform stores private repositories, coordinates deployment pipelines, authenticates users, and integrates with container registries and cloud environments. A server-level compromise could potentially allow an attacker to investigate those relationships and search for ways to move deeper into the development environment.
The consequences might include unauthorized repository access, theft of accessible credentials, manipulation of application data, interruption of development operations, or attempts to compromise downstream software delivery.
These are potential post-exploitation outcomes, not confirmed activities associated with CVE-2026-97229. Their feasibility depends on the privileges of the compromised process, network segmentation, credential storage, and other protections.
The broader lesson is that software delivery platforms are attractive targets because they connect systems that organizations otherwise try to keep separate.
How CVE-2026-97229 Works: From Regular Expression Processing to Remote Code Execution
To understand the vulnerability, it helps to separate three things that are often discussed as though they were the same: a regular expression, a CI/CD pipeline, and the software component responsible for interpreting a pipeline’s configuration.
A regular expression is a pattern used to identify or compare text. Developers use them for everything from validating input to matching file names. GitLab CI/CD also supports regular expressions in pipeline rules, including conditions that match branch names.
For example, the following simplified pipeline configuration uses a regular expression to decide whether a job should run:
stages:
  - test

run_tests:
  stage: test
  script:
    - echo "Running automated tests"

  rules:
    - if: '$CI_COMMIT_BRANCH =~ /^release\/.*$/'
      when: on_success

    - when: never
This example is ordinary, legitimate GitLab configuration. It instructs GitLab to run a testing job when a branch name begins with release/.
GitLab documents this form of matching in its CI/CD rules documentation. Regular expressions can appear inside conditional expressions, making their interpretation part of the normal process of understanding pipeline configuration.
The vulnerability becomes relevant when the implementation responsible for handling an expression does not safely process particular inputs.
The integer overflow at the center of the vulnerability
An integer overflow occurs when an arithmetic operation produces a result that cannot be represented within the integer type used to store it.
Imagine a program calculating how much memory it needs to process a regular expression. The required size might depend on the expression’s length, repetition structure, or internal representation.
In a simplified example, a program might perform a calculation resembling:
// Conceptual example only.
// This is not GitLab's vulnerable source code.

size_t required_size = pattern_length * multiplier;

buffer = allocate(required_size);
If the multiplication exceeds the maximum representable value of size_t, the calculated result can wrap around to an unexpectedly small number.
If subsequent operations assume that the allocated buffer is large enough for the original calculation, memory-safety problems may follow.
Depending on the surrounding implementation, integer overflow bugs can contribute to invalid memory access, heap corruption, crashes, or other unintended behavior. In some cases, attackers can use these conditions to achieve code execution.
Not every integer overflow is exploitable, and an overflow alone does not prove that an attacker can control instruction execution. The danger depends on what the program does with the incorrect value.
For CVE-2026-97229, GitLab specifically identifies insufficient regular expression validation and an integer overflow in the CI/CD regular expression compiler as the cause of a possible remote code execution condition.
The public advisory does not provide enough detail to establish the exact memory layout, allocation calculation, or exploitation technique. Therefore, the example above illustrates the general vulnerability class rather than a confirmed exploit chain.
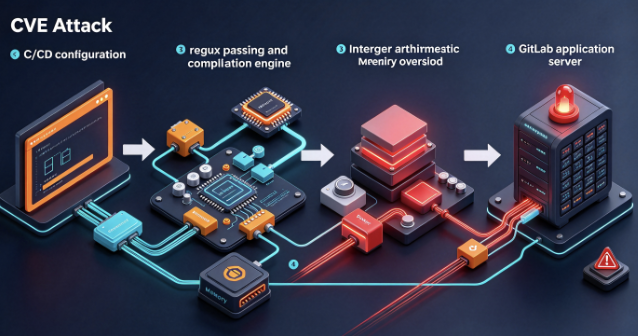
Why the compiler matters more than the expression
The most important security boundary is the point where externally influenced configuration data reaches the component that interprets it.
Consider the conceptual processing sequence:
CI/CD configuration inputRegular expression supplied through a supported configuration path
Expression parsing and validationGitLab interprets the configuration
Vulnerable regular expression compilerInsufficient validation can lead to an integer overflow
Potential arbitrary code executionOn the GitLab application server, under the conditions described by the advisory
Conceptual vulnerability path based on GitLab’s published description. This is not a verified request-level exploit sequence.
A developer writing a pipeline rule normally expects the expression to influence whether a job runs. The expression should not gain authority to manipulate the GitLab server’s memory or execute operating-system commands.
CVE-2026-97229 is serious because the published vulnerability breaks that expected separation between configuration data and program behavior.
And because the flaw is described as unauthenticated, defenders cannot assume that normal login requirements automatically protect every vulnerable execution path.
Is CVE-2026-97229 a ReDoS vulnerability?
No. The publicly documented impact is remote code execution resulting from an integer overflow, not simply a regular expression denial-of-service attack.
Regular expression denial of service, commonly called ReDoS, typically involves a pattern that causes excessive computation when matched against certain input strings. Backtracking behavior can consume CPU resources and make a service slow or unavailable.
CVE-2026-97229 concerns unsafe behavior in the regular expression compiler itself. Although both vulnerability classes involve regular expressions, their underlying mechanisms and potential consequences are different.
This distinction matters for detection and mitigation.
Controls aimed at reducing catastrophic backtracking may help address particular denial-of-service risks, but they should not be treated as a substitute for GitLab’s patch against this integer overflow.
Similarly, changing a project’s normal regex rules does not establish that the server-level vulnerability has been eliminated.
Which GitLab Versions Are Affected by CVE-2026-97229?
GitLab lists the following versions as affected by this specific vulnerability:
| GitLab release branch | Vulnerable versions | Version corrigée |
|---|---|---|
| GitLab 19.2 | 19.2.0–19.2.7 | 19.2.8 |
| GitLab 19.3 | 19.3.0–19.3.4 | 19.3.5 |
| GitLab 19.4 | 19.4.0–19.4.1 | 19.4.2 |
These ranges apply to both GitLab CE and EE. They reflect the version information in the official October 12 patch advisory, not a general statement about all vulnerabilities in earlier GitLab releases.
For example, GitLab 19.1 is not listed in the affected ranges for CVE-2026-97229. That does not mean an older release is secure or should be left unpatched. Unsupported or outdated installations may contain other vulnerabilities that require attention.
GitLab also confirms that GitLab.com is already running a patched version and that GitLab Dedicated customers do not need to take action for this release. The immediate patching responsibility therefore falls primarily on organizations operating self-managed installations.
Why some advisories mention GitLab 19.3.4 instead of 19.3.5
Administrators may encounter different version numbers when reading news reports, automated vulnerability feeds, or cached security advisories.
Some initial coverage identified GitLab 19.3.4 as a release containing the security fix. However, GitLab’s current official release announcement identifies 19.3.5 as the recommended patch version because 19.3.4 introduced a separate issue affecting merge request pages when the Ona integration was enabled.
The sensible operational choice is to deploy 19.3.5 or a newer supported, patched release, rather than intentionally stopping at 19.3.4.
This is a useful example of why security teams should verify recommended remediation versions against the vendor’s latest advisory, particularly during critical patch releases.
Why Does CVE-2026-97229 Have a CVSS Score of 10.0?
A CVSS score of 10.0 represents the maximum severity under the CVSS v3.1 base scoring system.
For CVE-2026-97229, the score is particularly notable because it combines unauthenticated network exposure with potentially severe consequences for confidentiality, integrity, and availability.
Each part of GitLab’s published vector tells us something about the modeled attack.
| CVSS metric | Assigned value | Security significance |
|---|---|---|
| Vecteur d'attaque | Network (AV:N) | The vulnerable behavior can be reached through a network attack surface |
| Attack Complexity | Low (AC:L) | Exploitation is rated as requiring low complexity |
| Privilèges requis | None (PR:N) | A pre-existing authenticated account is not required |
| Interaction avec l'utilisateur | None (UI:N) | Exploitation does not require another user to take an action |
| Champ d'application | Changed (S:C) | The assessed impact crosses a security authority boundary |
| Confidentialité | High (C:H) | Significant unauthorized information exposure is possible |
| Intégrité | High (I:H) | Significant unauthorized modification is possible |
| Availability | High (A:H) | Significant disruption is possible |
The score does not mean that every attacker can instantly compromise every GitLab server, nor does it establish a 100% exploitation success rate.
CVSS measures the inherent severity of a vulnerability under a defined scoring model. It is not a real-time estimate of the likelihood that a specific organization will be attacked.
An internet-facing instance, an isolated internal instance, and an already patched instance have very different exposure profiles, even though the CVE’s published base score remains the same.
For incident prioritization, teams should consider both the CVSS score and local factors such as service exposure, network access, available compensating controls, and the importance of the data accessible from the server.
In this case, however, the absence of authentication requirements and the potential for server-level code execution provide strong reasons to treat vulnerable deployments as urgent patching candidates.
What Could an Attacker Actually Do After Exploiting the Vulnerability?
There is an important difference between the direct security impact described by GitLab and the secondary attacks that might become possible after a server is compromised.
The confirmed vulnerability class is potential arbitrary code execution on the GitLab server.
What happens next depends on how the instance is deployed and what privileges the compromised process has.
To understand the business consequences, consider three hypothetical attack scenarios.
Scenario 1: A compromised GitLab server becomes a source-code theft opportunity
Imagine a technology company operating a self-managed GitLab instance that contains dozens of private repositories. The platform is reachable through a company VPN or a restricted internet-facing interface, and development teams use it throughout the day.
If an attacker successfully exploits CVE-2026-97229 and obtains execution within the application environment, the next objective might be to understand which repositories and services are accessible.
The attacker may try to discover application credentials, repository storage locations, service configuration, or database connections. Depending on the permissions available, that access could expose source code, internal documentation, or sensitive development metadata.
Source-code theft can have consequences beyond intellectual property loss. Private repositories may reveal application architecture, undocumented API paths, defensive controls, and dependencies that help an attacker identify additional opportunities.
This does not establish that CVE-2026-97229 automatically permits unrestricted repository access. It illustrates why arbitrary code execution on a source-code management platform is especially concerning.
Scenario 2: CI/CD credentials become a path into production infrastructure
Many organizations use GitLab to automate deployment.
A pipeline might build a container, push it to a private registry, and deploy it to a Kubernetes cluster. Another might use cloud credentials to create infrastructure or publish a software release.
The resulting environment often includes credentials and trust relationships distributed across GitLab, runners, secret managers, deployment systems, and cloud accounts.
A compromised GitLab server might expose some of these relationships, depending on how secrets are stored, accessed, and protected.
An attacker who obtains usable credentials could then attempt unauthorized deployment, access to artifact storage, or cloud-resource manipulation.
Again, the direct RCE vulnerability does not prove that every secret can be extracted. Encrypted credential storage, external secret managers, scoped tokens, isolation, and privilege boundaries can substantially alter the outcome.
The security issue is the possibility of a chain: an initial server compromise may create an opportunity to attack the systems that trust the server.
GitLab’s own token security guidance recommends avoiding broadly scoped personal access tokens in CI/CD where possible and prioritizing more narrowly scoped credentials.
Scenario 3: A development platform compromise threatens software integrity
The third scenario concerns software supply-chain security.
Suppose an organization uses GitLab to manage both application source code and automated release workflows. Its build system publishes packages or container images that eventually reach production environments or external customers.
If an attacker gains sufficient control over the development platform, they may attempt to modify repository contents, pipeline definitions, build artifacts, release metadata, or deployment settings.
An unauthorized change introduced into a trusted release process can be more difficult to identify than a direct attack against a production web application, particularly if downstream systems assume that artifacts produced by the official pipeline are trustworthy.
That concern is not hypothetical as a general attack category. In an April 2026 analysis of software supply-chain incidents, GitLab described multiple attacks involving development dependencies and pipeline security.
Those incidents are separate from CVE-2026-97229, and there is no basis for attributing them to this vulnerability. They nevertheless illustrate why attackers value access to build and release workflows.
The common thread across these scenarios is that a GitLab instance can function as a trust hub. The more services that rely on it, the more important it becomes to protect the infrastructure hosting it.
Has CVE-2026-97229 Been Exploited in the Wild?
As of October 13, 2026, the GitLab advisory and CERT-EU’s security notice do not report confirmed exploitation of CVE-2026-97229 in real-world attacks.
Public reporting available at the time of writing also does not establish the existence of a publicly verified proof-of-concept exploit. BleepingComputer’s October 12 report describes the vulnerability and the vendor’s patching warning, but does not document a confirmed attack campaign.
That absence of reporting should not be interpreted as evidence that exploitation is impossible or that no attempts have occurred.
There are several reasons to remain cautious.
First, the vulnerability is new. Publicly confirmed exploitation frequently depends on investigation, vendor disclosure, or the discovery of evidence within affected environments. The time between initial exploitation and public reporting can vary considerably.
Second, the vulnerability carries a maximum-severity score and an unauthenticated network attack vector. These attributes are likely to attract attention from both vulnerability researchers and potential attackers.
Third, public patches can provide researchers with information about what changed in the vulnerable implementation. That can sometimes accelerate the development of independent proof-of-concept code, although the success and timing of such efforts cannot be predicted for this specific vulnerability.
GitLab’s advisory states that detailed issues associated with security fixes are normally made public on its issue tracker 90 days after the release. The initial advisory therefore should not be treated as a complete technical disclosure.
For defenders, the immediate priority is patching and exposure assessment, not waiting for a publicly confirmed exploit.
An organization should also distinguish between the following statements: a vulnerable GitLab version is installed, the vulnerable functionality is reachable, exploitation is technically possible in that environment, and an attacker has actually exploited the instance. Those are different findings requiring different levels of evidence.
How to Check Whether Your GitLab Instance Is Vulnerable
For most administrators, determining exposure begins with identifying the running GitLab version.
This is more reliable than attempting to recreate the vulnerability in production, particularly when public technical details are incomplete.
Check the GitLab version using the web interface
Authenticated users of self-managed GitLab installations can find the version under Help → Help, where GitLab displays the product version.
This method is particularly convenient for teams that administer GitLab through the web interface but do not have direct shell access to the host.
GitLab describes the process in its official version identification documentation.
Check the GitLab version from the server
Administrators with shell access to a Linux package installation can run:
sudo gitlab-rake gitlab:env:infoThe resulting diagnostic information includes the GitLab version and relevant environment details. For example, a vulnerable installation might report:
GitLab information
Version: 19.4.1-ee
This sample output is illustrative. A real installation may report a different version and edition.
GitLab documents this command in its maintenance Rake tasks guide.
For an Ubuntu or Debian installation managed through Linux packages, administrators can also check the package inventory:
dpkg-query -W gitlab-ce gitlab-ee 2>/dev/nullOn RPM-based systems, the equivalent package inventory can be checked with:
rpm -qa | grep -E '^gitlab-(ce|ee)-'These commands are non-exploitative version and package checks. They do not attempt to trigger the vulnerability or determine whether the instance has previously been compromised.
Containerized and Kubernetes-based installations should be assessed using their actual deployed image tags, Helm release configuration, and running workload versions rather than assuming that a repository value describes every running node.
How to interpret your findings
If the instance is running GitLab 19.4.1, it falls within the affected range and should be upgraded to 19.4.2 or a subsequent patched version.
A GitLab 19.3.3 instance should be upgraded to at least 19.3.5. A GitLab 19.2.7 instance should be upgraded to at least 19.2.8.
A deployment already running a fixed version is not vulnerable to CVE-2026-97229 according to the published version ranges, assuming the deployed software genuinely includes the vendor’s fix.
In multi-node deployments, however, checking a single frontend is not enough. Every applicable GitLab application node and workload should be accounted for so that an outdated node is not left behind a load balancer or in a secondary environment.
The correct question is not simply, “What version does GitLab show?” It is, “Are all relevant running components using a fixed build?”
How to Fix CVE-2026-97229 Safely
GitLab’s primary remediation is to upgrade affected self-managed CE/EE installations to a version containing the security fix.
The vendor recommends immediate upgrades and prioritization of vulnerable deployments. CERT-EU’s October 12 advisory specifically emphasizes internet-facing installations.
The challenge is that GitLab upgrades can involve more than replacing an application binary. Large installations may depend on database migrations, external PostgreSQL services, Redis, Gitaly, runners, container registries, and related infrastructure.
A rushed upgrade without understanding these dependencies can create an availability incident. At the same time, delaying a critical security patch because the environment is complicated can leave the organization exposed.
The objective is to move quickly without losing control of the deployment.
Back up the environment before changing it
Before making production changes, administrators should verify that recent backups are available and restorable.
GitLab’s pre-upgrade documentation specifically discusses backing up the instance and preserving the secrets and configuration files necessary for restoration.
A database backup alone may not be sufficient to restore all GitLab functionality. Repository storage, configuration files, application secrets, uploaded data, and other deployment-specific resources need to be considered.
For a possible security incident, preserve relevant logs and forensic evidence as well. Backups created after a suspected compromise may already contain attacker modifications and should not automatically be considered clean.
Upgrade to the correct fixed release
For a single-node Ubuntu or Debian installation managed through GitLab’s official package repositories, the following commands illustrate explicit package-version installation for each edition.
For GitLab Enterprise Edition 19.4:
sudo apt update
sudo apt install gitlab-ee=19.4.2-ee.0
For GitLab Community Edition 19.4:
sudo apt update
sudo apt install gitlab-ce=19.4.2-ce.0
Administrators staying on the 19.3 branch should use the corresponding 19.3.5 package, while those staying on the 19.2 branch should use 19.2.8.
These are examples for compatible Linux package installations, not universal upgrade commands. The required procedure depends on the operating system, package availability, deployment architecture, and upgrade history.
GitLab’s Linux package upgrade guide explains the installation syntax and describes supported single-node and multi-node upgrade procedures.
Administrators should also examine the GitLab upgrade path requirements. Skipping required upgrade stops when moving between minor or major releases can create problems with database migrations and compatibility.
An organization operating a much older GitLab version should not assume that jumping directly to 19.4.2 is supported.
Verify the upgrade after installation
After completing the patch, confirm the running version using the server-side diagnostic command:
sudo gitlab-rake gitlab:env:infoFor Linux package installations, examine service status and run GitLab’s supported health checks:
sudo gitlab-ctl status

sudo gitlab-rake gitlab:check SANITIZE=true
GitLab documents these checks in its upgrade troubleshooting guide.
The next step is functional verification. Confirm that users can authenticate, repositories can be accessed, merge requests load correctly, and expected CI/CD jobs operate normally.
Production-critical deployment pipelines should also be tested through the organization’s established release procedures, rather than using untrusted or destructive test payloads.
One detail deserves special attention: patch verification and compromise assessment are separate activities.
A successful upgrade establishes that the patched software is running. It does not establish whether an attacker exploited the earlier version before the patch was installed.
That question requires investigation.
Detecting Possible CVE-2026-97229 Exploitation
The difficulty with a newly disclosed vulnerability is that defenders may not yet have reliable, vulnerability-specific indicators of compromise.
For CVE-2026-97229, the public advisory does not provide a verified malicious HTTP signature, exploit payload, attacker infrastructure list, or forensic artifact that can serve as a definitive detection rule.
Security teams should therefore avoid treating a generic signature for a suspicious regular expression as a reliable detector for this particular CVE.
A better initial approach is to combine exposure information with broader evidence of unusual server activity.
Examine GitLab application and reverse-proxy logs
On GitLab Linux package installations, relevant log files include:
| Log file | What it can help investigate |
|---|---|
/var/log/gitlab/nginx/gitlab_access.log | Incoming web requests and unusual request patterns |
/var/log/gitlab/nginx/gitlab_error.log | Reverse-proxy errors and abnormal request handling |
/var/log/gitlab/gitlab-rails/production_json.log | Structured Rails controller request information |
/var/log/gitlab/gitlab-rails/api_json.log | Structured API request activity |
/var/log/gitlab/gitlab-rails/production.log | Application request processing and error context |
These locations are documented in GitLab’s logging reference. They may differ for self-compiled installations or Kubernetes deployments.
Investigators should pay attention to unexpected bursts of requests, unusual error patterns, repeated application failures, or configuration-related activity that does not fit normal development operations.
For example, a sudden increase in server errors associated with previously unseen clients may justify further investigation.
However, an HTTP 500 response is not proof of exploitation. GitLab installations can produce server errors for many legitimate operational reasons, particularly during upgrades or infrastructure problems.
Conversely, the absence of obvious errors does not rule out successful code execution.
For this reason, log analysis should be correlated with process-level telemetry and other available evidence instead of relying exclusively on HTTP status codes.
Look for unexpected processes and outbound connections
Since the documented impact involves possible code execution on the server, endpoint and host monitoring can provide valuable complementary evidence.
On Linux servers, useful defensive questions include whether application service accounts initiated unexpected processes, whether unfamiliar executables appeared in temporary directories, and whether GitLab application processes began connecting to unusual external destinations.
For a read-only snapshot of running processes and listening network sockets, administrators can use:
ps auxww

sudo ss -tulpn
These commands can help establish a current view of the host, but they are not comprehensive forensic tools and do not establish what happened before the commands were executed.
A sophisticated attacker may also interfere with host visibility. Where available, historical endpoint detection telemetry, process-execution auditing, centralized logs, and network records are more valuable than a single live command output.
Investigators should compare suspicious observations with the instance’s established baseline. GitLab legitimately launches background workers, interacts with repositories, and connects to other services, so unusual behavior must be evaluated in context.
Review changes to CI/CD configuration and access credentials
Even when the suspected initial vulnerability exists in the GitLab server rather than a runner, the surrounding development environment remains important to an investigation.
Review unexpected modifications to .gitlab-ci.yml, unexplained pipeline executions, recently created access tokens, changes to protected branches, and unfamiliar administrative actions.
These observations are general post-compromise hunting opportunities rather than CVE-specific indicators.
GitLab recommends reviewing audit information for suspicious users, tokens, pipelines, code changes, and project-setting modifications when investigating security incidents. Its security incident response guidance also emphasizes assessing credential scope before deciding how to revoke or rotate potentially exposed secrets.
For deployments with appropriate licensing, instance audit events can provide additional information. These can be accessed through administrative audit interfaces or the documented audit events API.
What if suspicious activity is discovered?
An organization that finds credible indications of compromise should treat the situation as an incident rather than simply a patching task.
The investigation needs to preserve evidence, establish the likely compromise window, identify affected assets, and assess whether the attacker gained persistence or obtained credentials.
Where necessary, isolate affected systems using approved incident response procedures while preserving evidence that would otherwise be lost.
Credentials exposed to an attacker may remain useful after the vulnerable server is patched. In serious cases, restoring the service from a known-clean deployment and systematically replacing compromised secrets may be safer than assuming an in-place update removed every attacker-controlled change.
The objective is to establish both that the original vulnerability has been eliminated and that no unauthorized access remains.
Why Patching GitLab Alone Is Not Enough to Protect CI/CD Infrastructure
CVE-2026-97229 highlights a broader security challenge: modern development infrastructure is interconnected, and a compromised platform can create risks for systems that were not directly vulnerable.
Patching eliminates the documented vulnerable behavior in the updated software. It does not automatically correct overprivileged service accounts, weak network segmentation, long-lived credentials, or excessive trust between development and production systems.
Those weaknesses matter because they can determine how far an attacker can move after obtaining initial access.
Reduce unnecessary network exposure
An internet-facing GitLab instance is exposed to a larger population of potential attackers than an instance available only through controlled internal access.
Organizations should review whether their GitLab servers genuinely need to be accessible from the public internet and whether access can be restricted to trusted networks, approved users, or controlled application gateways.
Network restrictions can reduce opportunities for exploitation while an emergency patch is being prepared. They are not guaranteed mitigations for CVE-2026-97229, especially if an attacker already has access to an allowed network or another internal entry point.
It is also important to distinguish network exposure from application authentication. A server protected by a login screen may still contain vulnerable pre-authentication functionality.
Because this CVE is classified as unauthenticated, teams should not assume that requiring users to log in eliminates the attack surface.
Give deployment credentials the minimum permissions required
CI/CD systems often need elevated access to perform legitimate tasks. A deployment pipeline may create cloud resources, publish artifacts, or update production applications.
The danger arises when a single credential grants much more authority than the corresponding task requires.
A pipeline responsible for publishing one container image should not need administrative access to an entire cloud account. A staging deployment should not automatically inherit production secrets. A testing job should not be able to change release configurations merely because the same CI/CD platform manages both activities.
GitLab’s pipeline security documentation recommends using secrets management solutions for sensitive credentials and appropriately restricting access to protected variables and runners.
These practices do not fix the integer overflow in CVE-2026-97229. Their value is in limiting the consequences of a successful compromise and reducing opportunities for subsequent attacks.
Keep untrusted pipeline code away from sensitive resources
Development teams routinely execute code from branches, merge requests, imported repositories, and third-party dependencies.
Not all of that code deserves the same level of trust.
Protected runners and protected branches can provide additional separation between ordinary development tasks and sensitive deployment workflows. Carefully designed runner isolation also reduces the chance that one build environment can interfere with other jobs or access credentials unrelated to its purpose.
GitLab specifically warns that changes to .gitlab-ci.yml can expose CI/CD variables and recommends reviewing pipeline configuration before executing untrusted changes in sensitive contexts.
That guidance is documented in GitLab’s CI/CD variable security reference.
The connection to CVE-2026-97229 is architectural rather than mechanical. A strong pipeline security model cannot eliminate a vulnerable application parser, but it can help prevent the development platform from becoming an unrestricted bridge into every other environment.
Treat the GitLab application server as critical infrastructure
Many organizations apply strict controls to production Kubernetes clusters, cloud accounts, and customer-facing applications while treating development infrastructure as a lower-risk environment.
That distinction is increasingly difficult to defend.
A GitLab application server may manage the code, identities, automation, and artifacts that determine what ultimately enters production. Its security therefore deserves the same operational discipline applied to other business-critical infrastructure.
That includes security patch management, centralized monitoring, tested backups, privileged-access reviews, appropriate network isolation, and a documented incident response process.
The discovery of a CVSS 10.0 vulnerability is a reminder that security failures can occur in unexpected parts of the development stack, not only at obvious authentication or network boundaries.
CVE-2026-97229 Is Not the Only Important Vulnerability in the October GitLab Update
Although CVE-2026-97229 is the most severe issue in the October 12 release, it is not the only reason to install the update.
GitLab’s patch announcement addresses 24 security issues, including several vulnerabilities that affect how development systems enforce access controls, interpret repository content, and protect CI/CD operations.
Three additional vulnerabilities are particularly relevant to teams responsible for software supply-chain security.
| Vulnérabilité | Sévérité | Potential impact |
|---|---|---|
| CVE-2026-92883 | CVSS 8.7 | Crafted repository content could trigger cross-site scripting in other users’ browser sessions |
| CVE-2026-16301 | CVSS 8.5 | Developer-role users could execute pipelines on protected branches without the intended authorization |
| CVE-2026-14814 | CVSS 8.2 | Repository file cache poisoning could cause targeted pipelines to execute crafted content and potentially expose protected variables |
These issues are distinct from CVE-2026-97229, and they should not be combined into a fictional single exploit chain.
Nevertheless, they show how multiple security boundaries in a development platform can fail in different ways.
An authorization flaw can expose a protected pipeline. A cache-poisoning vulnerability can affect the content a pipeline consumes. A regular expression compiler bug can create a potential code execution path in the application server itself.
For defenders, the patch release is therefore not merely about fixing one dangerous function. It is an opportunity to address a broader set of weaknesses affecting the development environment.
GitLab’s October 12, 2026 patch advisory contains the affected version information and descriptions for each issue.
What CVE-2026-97229 Tells Us About the Future of CI/CD Security
The most interesting aspect of CVE-2026-97229 is not the maximum severity score. It is the location of the vulnerability.
A regular expression compiler is not an obvious high-profile attack surface to many organizations. It is part of the software infrastructure that quietly interprets configuration and helps automate development tasks.
Yet that infrastructure may process information from numerous users, repositories, integrations, and automated workflows.
The security of the entire platform depends on correctly handling those inputs.
This creates a difficult problem for defenders. Conventional access-control reviews may examine who can create projects or modify deployment settings, but they may not detect memory-safety vulnerabilities within components that process configuration.
Likewise, code review and dependency scanning are useful for securing the applications produced by a CI/CD platform, but those controls do not guarantee the security of the platform’s own implementation.
Organizations need to protect both sides of the development workflow: the software being built and the infrastructure responsible for building it.
The limits of configuration-based defenses
One tempting reaction to this vulnerability is to search for regular expressions in existing .gitlab-ci.yml files and remove anything that looks complicated.
Reviewing unusual configuration is a reasonable security practice, but it should not be confused with remediation.
The vulnerability exists in the software handling expressions, not necessarily in a legitimate project’s decision to use regular expressions.
An attacker-controlled expression may reach vulnerable functionality through a particular workflow that is not yet fully documented in public technical material. Removing regular expressions from a handful of known project files would not establish that every potential input path has been closed.
In the absence of a vendor-verified workaround, replacing the vulnerable implementation with a fixed release remains the dependable remediation.
Why continuous security validation matters
The traditional practice of assessing development infrastructure during occasional security reviews leaves a gap between disclosures and the next scheduled assessment.
A vulnerability such as CVE-2026-97229 can require action within hours of a vendor announcement, not months later.
Effective security validation should therefore include routine software inventory, automated version assessment, prioritized patching, and ongoing monitoring of critical infrastructure.
Automated security testing can help teams identify exposed services, outdated versions, insecure configurations, and unexpected changes. It can also support verification that remediation has been deployed correctly.
However, responsible vulnerability validation requires a clear distinction between detecting a potentially affected version and demonstrating actual exploitability.
A scanner that identifies GitLab 19.4.1 can reasonably report an affected version. Without additional reliable evidence, it should not claim to have demonstrated arbitrary code execution.
For a live production service, trying an unverified exploit simply to confirm a vendor-reported critical vulnerability may introduce unnecessary operational risk.
The more useful approach is to combine authenticated version checks, vendor advisory correlation, secure configuration review, and appropriate testing in controlled environments.
For CVE-2026-97229, a well-designed remediation process should produce evidence that the vulnerable software has been replaced, the relevant systems are functioning correctly, and any credible signs of earlier compromise have been investigated.
Frequently Asked Questions About CVE-2026-97229
Is CVE-2026-97229 a real GitLab vulnerability?
Yes. CVE-2026-97229 is an officially disclosed vulnerability affecting GitLab Community Edition and Enterprise Edition. GitLab describes an integer overflow issue in its CI/CD regular expression compiler that could permit unauthenticated remote code execution under certain conditions.
The official advisory was published on October 12, 2026.
What is the CVSS score of CVE-2026-97229?
GitLab assigns CVE-2026-97229 a CVSS v3.1 base score of 10.0, the highest possible score under that system.
The published vector indicates network exploitation with low attack complexity, no required privileges, no user interaction, and high potential impacts on confidentiality, integrity, and availability.
Can CVE-2026-97229 be exploited without authentication?
According to GitLab, yes, under certain conditions. The CVSS vector includes PR:N, indicating that privileges are not required.
However, the public advisory does not fully document the request-level exploitation requirements. Administrators should rely on the vendor’s affected-version guidance rather than assuming that a particular login setting or repository permission automatically prevents exploitation.
Which versions of GitLab fix CVE-2026-97229?
The official fixes are GitLab 19.2.8, 19.3.5, and 19.4.2.
Administrators should install the latest supported patched release appropriate to their upgrade path. GitLab 19.3.5 is preferred over 19.3.4 because the latter contained an additional merge request page issue that was subsequently fixed.
Is GitLab 19.4.1 vulnerable?
Yes. GitLab 19.4.1 is included in the affected version range. Organizations running this release should upgrade to 19.4.2 or a newer release containing the patch.
Does CVE-2026-97229 affect GitLab.com?
GitLab states that GitLab.com is already running a patched version. GitLab Dedicated customers also do not need to perform a customer-managed upgrade for this patch.
The primary remediation requirement concerns self-managed GitLab CE and EE deployments.
Does CVE-2026-97229 affect GitLab Runner?
The official advisory identifies the affected product as GitLab CE/EE and the vulnerable functionality as the CI/CD regular expression compiler.
It does not describe CVE-2026-97229 as a standalone vulnerability in the GitLab Runner executable.
However, a compromised GitLab application server may create risks for connected CI/CD infrastructure. Runner security should therefore be considered during broader impact assessment.
Can a firewall prevent exploitation?
Restricting access to a vulnerable GitLab instance can reduce exposure, particularly when access is limited to trusted networks.
However, firewall rules are not a confirmed comprehensive fix for CVE-2026-97229. An attacker may already have access to an allowed network, and the public advisory does not establish a narrowly defined set of network requests that can safely be blocked to eliminate the flaw.
The recommended fix remains a software upgrade.
Is there a public exploit for CVE-2026-97229?
As of October 13, 2026, the sources reviewed for this article do not establish a publicly verified proof-of-concept exploit or confirmed widespread exploitation.
That status may change. The absence of a public exploit should not be treated as a reason to delay patching.
Can CVE-2026-97229 lead to software supply-chain attacks?
Potentially, as a secondary consequence of a successful compromise.
The direct vulnerability concerns possible code execution on the GitLab server. An attacker who subsequently gains sufficient access to repositories, credentials, or release infrastructure might attempt to compromise software integrity.
The extent of that risk depends on the organization’s architecture, available privileges, and security controls. A complete supply-chain attack is not an automatically demonstrated consequence of the CVE.
How can an organization verify that remediation worked?
Administrators should confirm that every relevant GitLab application node is running a fixed version, execute supported health checks, and verify normal repository and CI/CD functionality.
They should also examine available security logs and incident-response evidence where the instance may have been exposed before patching.
Successful version verification demonstrates patch deployment, not the absence of previous compromise.
Final Thoughts: A Small Configuration Feature With Server-Level Consequences
CVE-2026-97229 demonstrates how a seemingly ordinary component can become a serious security risk when it operates inside critical development infrastructure.
The vulnerability does not involve a sophisticated-looking administrative feature or an obviously dangerous command-execution interface. It originates in regular expression processing, a capability used routinely in software configuration.
Yet under the conditions described by GitLab, insufficient validation of a specially crafted expression can lead to an integer overflow and potential arbitrary code execution on the application server.
That is why the CVSS score reaches 10.0.
For organizations operating self-managed GitLab instances, the immediate course of action is clear: identify affected deployments, apply the official security update, verify the installed version across the environment, and investigate suspicious activity where exposure warrants it.
The longer-term lesson concerns the trust placed in development infrastructure.
A modern GitLab environment may control source code, build automation, deployment credentials, release processes, and integrations with other important systems. Its compromise can therefore threaten more than one server.
CVE-2026-97229 is ultimately a reminder that the security of software delivery depends on the security of the platforms that make software delivery possible.
The most effective defense combines timely patch management with strong isolation, limited privileges, credential protection, reliable monitoring, and an incident response process capable of detecting and containing failures when they occur.
The vulnerability may begin with a regular expression. The security consequences depend on everything the surrounding platform is trusted to do.
 French
 English
 German
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew