
Last updated: November 4, 2026.
Breach and attack simulation and penetration testing create different kinds of evidence. BAS platforms repeatedly execute defined simulations to check whether security controls observe or block expected behavior. Penetration testing investigates a scoped environment to discover and validate weaknesses, including combinations and business logic that may not fit a predefined simulation.
The two are complementary when teams keep their claims precise. A successful simulation proves the tested control response for that scenario; it does not prove the absence of vulnerabilities. A pentest finding proves a specific failed control under stated conditions; it does not provide continuous monitoring.
For the assessment framework, consult MITRE ATT&CK and map the relevant guidance to the actual environment and authorized scope.
Compare the questions each method answers
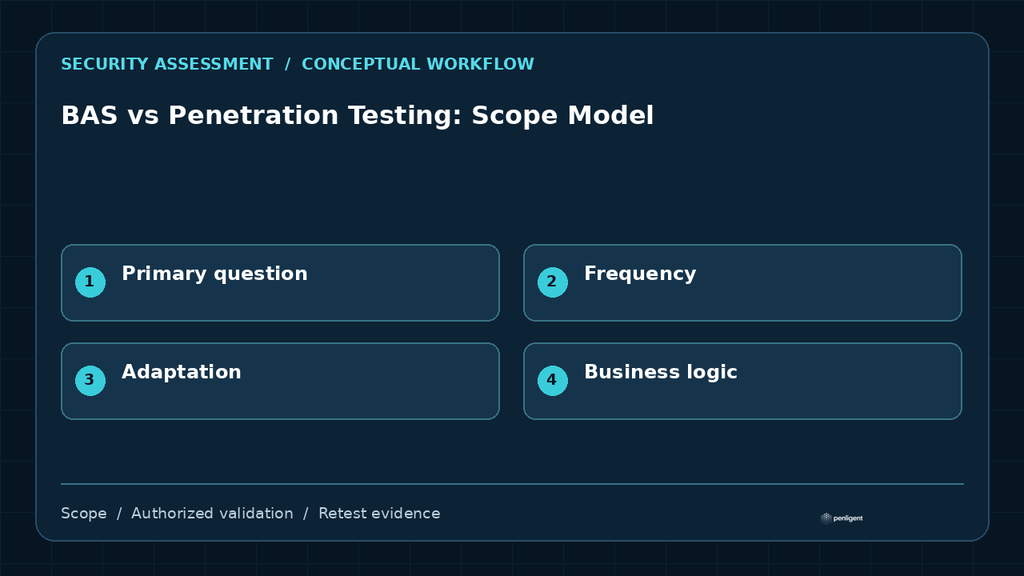
Use the operating question rather than tool category to choose the method.
| Dimension | BAS | Penetration testing |
|---|---|---|
| Question principale | Did defined controls respond to this simulation? | Can a tester find and validate a material weakness? |
| Frequency | Continuous or scheduled automation | Periodic or release-triggered engagement |
| Adaptation | Predefined scenarios and integrations | Human investigation and path changes |
| Business logic | Usually limited | Can test roles, state and workflow abuse |
| Preuves | Control telemetry and scenario result | Attack path, impact and remediation evidence |
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Use BAS for repeatable control assurance
BAS is useful for regression checks of prevention, logging, alerting and response across known scenarios. Stable identifiers and repeatable schedules help teams detect control drift after configuration or product changes.
Use pentesting for discovery and context
Pentesters can change direction when identity, architecture or business state reveals a new path. They can test authorization and workflow assumptions that are difficult to encode as generic simulations.
Create a shared validation backlog
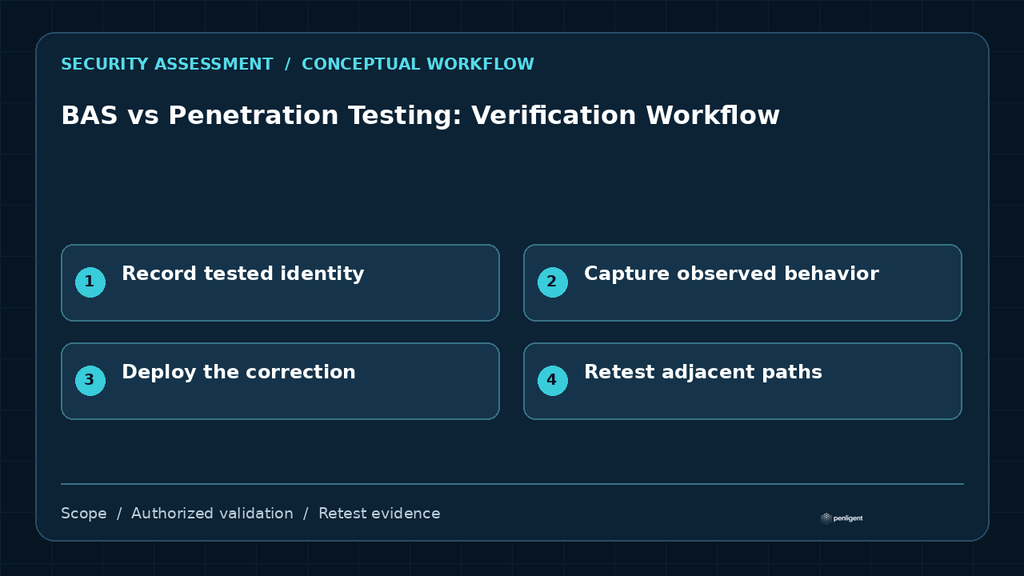
Turn recurring pentest findings into safe simulations when appropriate. Use BAS failures to prioritize configuration investigation and focused human testing. Store both results under the same asset and control ownership model.
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Questions buyers should ask
- Do you need continuous regression checks or discovery of unknown paths?
- Can the scenario safely produce meaningful control telemetry?
- Which business workflows require human role and state analysis?
- How will both result types feed one remediation backlog?
Conclusion
Use BAS to repeat known control checks and penetration testing to discover and validate context-dependent weaknesses. A mature program converts lessons between them while preserving the limits of what each result proves.
 French
 English
 German
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew