
CVE-2026-90436 affects end-of-life Apache Axis 1.x through 1.4; Apache does not expect to publish a fixing Axis 1.x release. Les Apache-authored record recommends migration to a different SOAP engine, such as Axis 2/Java, or a build containing its specified source patch. CISA added the issue to KEV on November 18, 2026, with forensic triage marked “Yes” and a November 21 due date in the applicable directive context.
Inventory the component before assigning the product risk
The record identifies Maven coordinates axis:axis et org.apache.axis:axis, as well as the Axis 1.x source repository. Search the dependency graph and deployed application libraries for the actual component. A transitive, embedded or repackaged copy may not appear as a separately installed server. Conversely, an Apache-branded product name is not proof that Axis 1.x is present.
Record which deployed application loads the library, its exact binary or supplier build, and whether incoming SOAP messages reach that engine. Keep the affected component and the containing product separate in the asset record. This CVE should not be relabeled as a Confluence vulnerability without independent evidence about a particular product distribution.
Service authentication happens after the dangerous parser step
The vendor describes untrusted SOAP fault data selecting a class before service-specific handler chains run. Loading can trigger static initialization; constructing a suitable class can produce code execution in the application process. The outcome depends on the application classpath. Authentication configured only in a per-service handler does not protect the earlier parsing boundary.
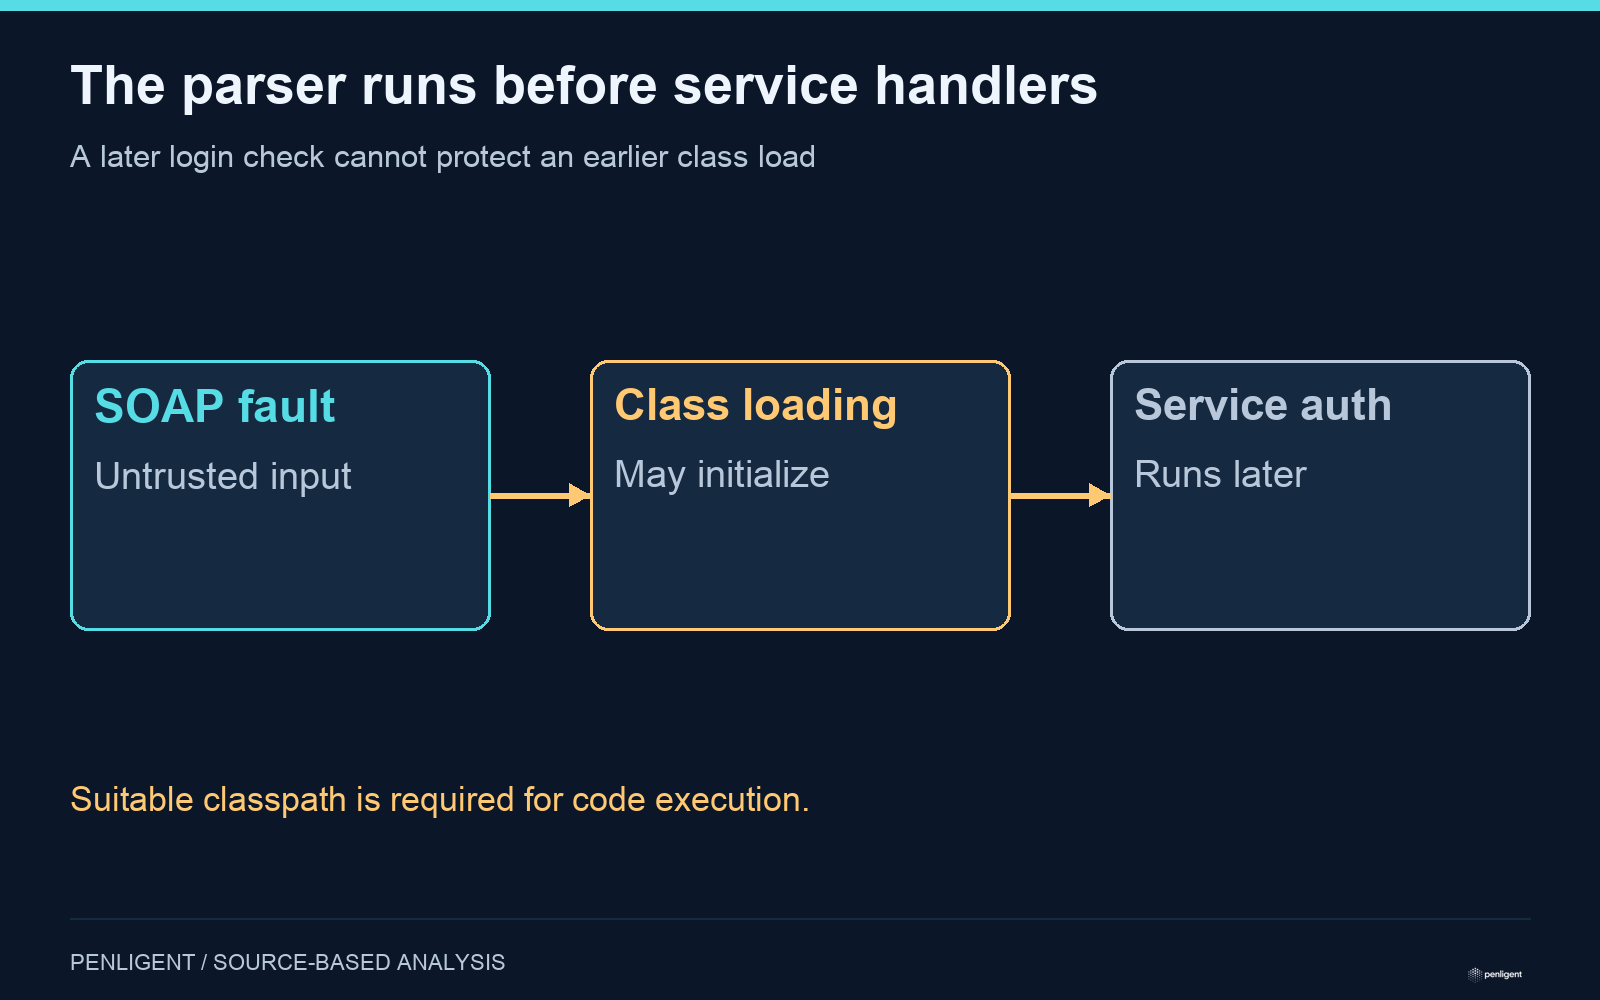
This is why “the service requires login” is insufficient closure evidence. It describes the later handler, not necessarily access to fault parsing. Network restrictions can reduce who reaches the application while the engine is replaced, but do not transform an unpatched parser into a fixed one. Do not remove arbitrary libraries from production as a substitute for a supported migration or reviewed patch.
The official patch closes more than the final cast
| Source change | Security property | Build evidence to request |
|---|---|---|
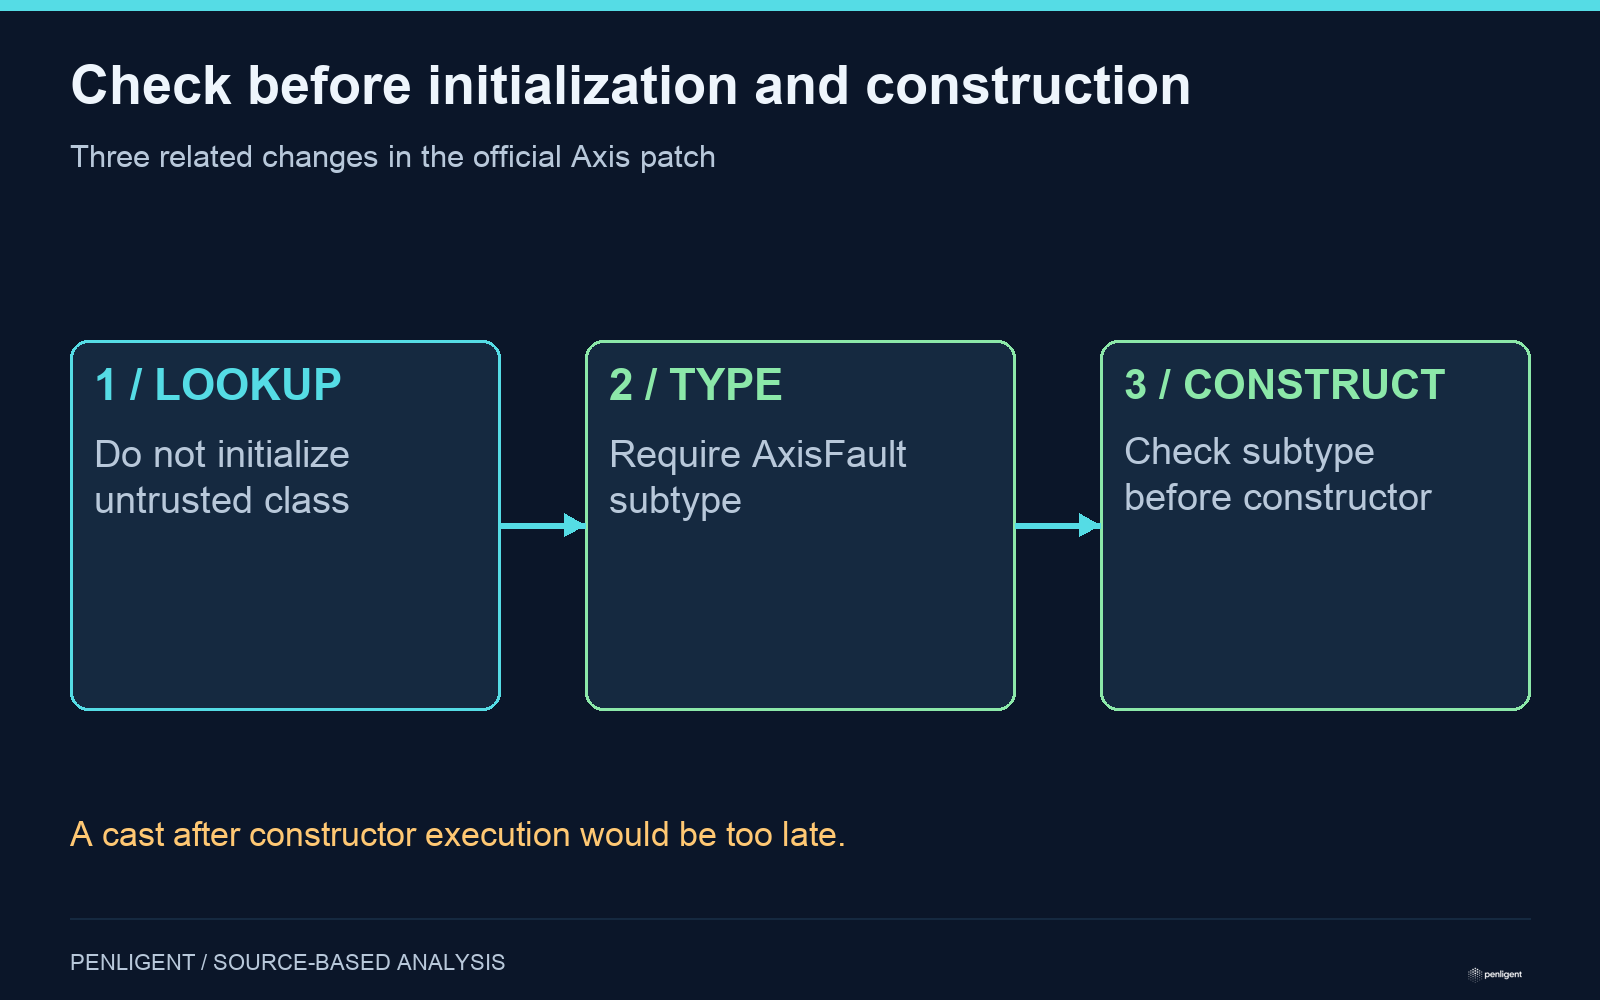
| ClassUtils initialization control | Supports loading without running the selected class initializer | The changed helper and its callers are included, not only a constructor edit. |
| SOAPFaultDetailsBuilder | Loads without initialization and accepts only AxisFault subtypes | The subtype gate precedes recording the selected fault class. |
| SOAPFaultBuilder | Checks subtype before reflective construction | An invalid class is rejected before its constructor can run. |
These observations come from Apache commit 41f3b4e8. The patch also adds tests using a harmless probe to check that a non-fault class is neither initialized nor constructed, while a legitimate fault still works. A cast that rejects an object after its constructor executes would be too late. Our review is of the source difference; no test execution or binary certification is claimed.
Choose migration or a controlled patched build
Migration changes the supported engine and can require SOAP compatibility work. Plan normal request, fault-handling, client and integration tests rather than treating Axis 2/Java as a filename replacement. If a vendor supplies an interim patched Axis 1.x build, obtain its provenance, patch mapping, binary identifier and support position. There is no vendor promise here of an official new 1.x release number that a scanner can simply wait for.
For a custom backport, require a reproducible build record tied to the complete patch and the deployed artifact. Confirm which classloader actually loads it when multiple application libraries exist. A corrected JAR stored on disk does not prove a running application stopped using an older loaded copy.
Close the software change and the historical review independently
Retain deployment and restart evidence, legitimate SOAP success and fault behavior, and any remaining compatibility limits. Preserve relevant application and host evidence from the exposed period before normal maintenance removes it. KEV establishes known exploitation of the vulnerability; it does not prove that every Axis application has a suitable execution class or that a particular application was compromised.
The following Penligent 3.0 video is a general product workflow demonstration. It is not evidence of exploitation or proof that this vulnerability was remediated.
Methodology, November 19, 2026: AI-assisted drafting with agent verification against the linked primary records and source changes. The deployment decisions and proposed acceptance checks are analysis. No exploit was executed and no first-hand incident response is claimed.
 French
 English
 German
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew