
Continuous penetration testing is a change-aware validation program, not a scanner that runs every day. It should select tests based on releases, assets, identities and trust-boundary changes, then produce validated evidence and verify remediation.
Choose meaningful triggers
| הדק | Testing response | Evidence of completion |
|---|---|---|
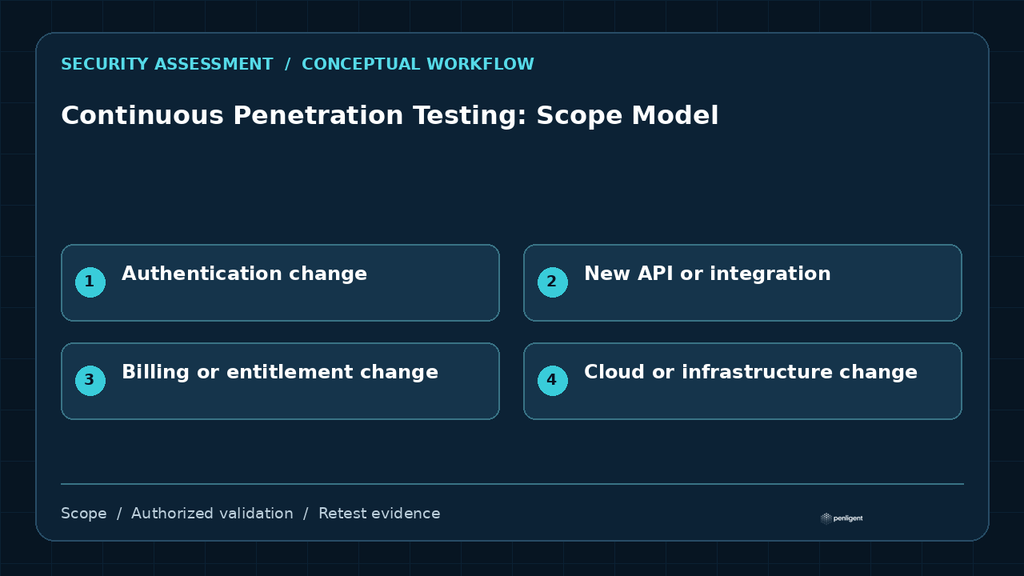
| Authentication change | Test enrollment, SSO, MFA, recovery, rotation and revocation | Identity-state matrix and negative tests |
| New API or integration | Test object and function authorization, secrets, callbacks and failure paths | Role, resource and downstream decision evidence |
| Billing or entitlement change | Test replay, race, downgrade and cancellation state | Before-and-after transaction state |
| Cloud or infrastructure change | Validate exposure, identity, network and data boundaries | Active resource configuration and access result |
| Critical CVE | Inventory affected components, validate prerequisites and verify the fix | Package, runtime, configuration and exposure evidence |
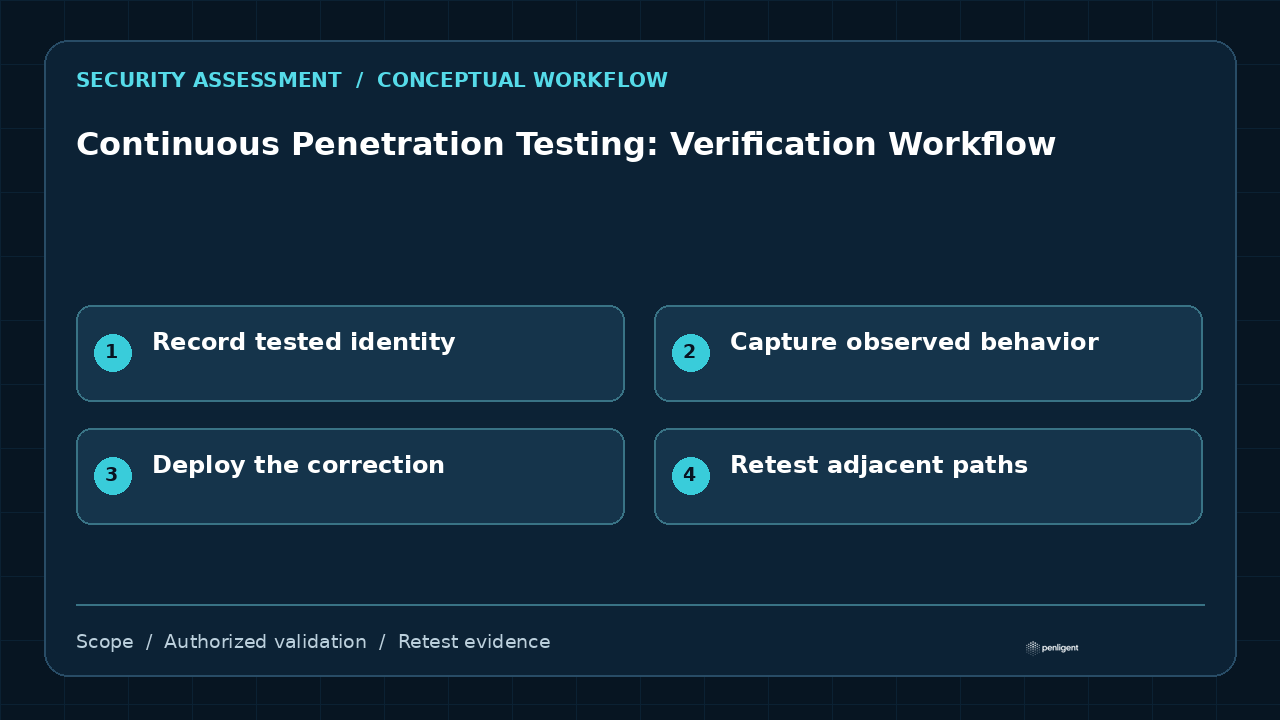
| תיקון | Repeat the original invariant and check related paths | Retest tied to the original finding |
For the assessment framework, consult NIST Secure Software Development Framework and map the relevant guidance to the actual environment and authorized scope.
ה NIST Secure Software Development Framework supports integrating security practices into development. The OWASP ASVS ו OWASP WSTG can supply requirements and test ideas. Continuous testing still needs product-specific risk selection.
Separate coverage layers
- Every change: fast controls, dependency checks, secrets, policy and targeted security regressions.
- Risk-triggered: adaptive testing of changed trust boundaries and workflows.
- Scheduled deep dives: broader application, API, cloud and business-logic assessment.
- Independent assurance: periodic external review for blind spots and governance needs.
Trying to run the deepest test on every commit creates noise and slows delivery. Running only fast checks leaves architectural and stateful flaws untested.
Maintain scope as data
Track applications, domains, APIs, owners, environments, roles, tenants, critical data, integrations and prohibited actions in a versioned scope inventory. Testing automation should consume approved scope, not infer authorization from DNS or repository access.
Evidence and deduplication
Continuous programs can repeatedly rediscover the same root cause. Use a stable finding identity based on the violated security property, component and affected boundary. Preserve first-seen, last-seen, remediation and retest evidence without inflating counts.
Stop controls
Test target allowlists, rate ceilings, approval gates and cancellation. A CI job that times out should not leave browsers, agents or callbacks running. State-changing actions should require explicit policy or human approval.
Metrics
| Useful metric | What it shows |
|---|---|
| Time from change to relevant test | Whether the program responds to risk |
| Accepted finding precision | How much engineering attention is wasted |
| Developer reproduction rate | Whether evidence is actionable |
| Time to verified remediation | Whether testing closes the loop |
| Scope drift | Whether new assets and roles enter coverage |
| Escaped-scope events | Whether execution controls work |
Operating model
- Application owners register assets, roles and critical workflows.
- Release and infrastructure events update the change context.
- Policy selects safe automated checks and deeper review.
- Findings are validated and assigned with reproducible evidence.
- Remediation triggers a targeted retest.
- Periodic review identifies coverage and control gaps.
Change classification
Not every release needs the same test. Classify changes by affected security boundary. A copy update may need no new adversarial work, while a new identity provider, billing state or file processor should trigger targeted testing. Record why a change received a particular test depth so risk acceptance remains auditable.
Use a security regression catalog
Convert confirmed findings into durable regression cases. Each case should state the security invariant, required roles and state, safe test action and expected result. Keep the catalog separate from raw exploit payloads so it can run safely in CI or staging. Review cases when architecture changes; a test that still passes may no longer reach the relevant decision point.
Human review points
| Decision | Why human review remains useful |
|---|---|
| New high-impact action | Automation may not understand business consequence or production timing |
| Critical severity | Impact, prerequisites and exploit chain require accountable validation |
| Scope expansion | Authorization cannot be inferred from technical reachability |
| Customer-data access | Evidence should minimize exposure and follow incident procedures |
| Finding closure | Package or code changes may not activate across every runtime |
False-positive and false-negative handling
Track rejected findings with reasons and retain enough evidence to improve rules. Also sample negative results: choose critical workflows and independently review whether the continuous system actually exercised them. Precision without meaningful coverage creates false confidence; broad coverage without validation overwhelms engineering.
Governance and ownership
Assign an owner for scope inventory, testing policy, critical notifications and platform credentials. Product teams should own workflow context and remediation, while security owns test standards and independent challenge. A continuous program fails when everyone receives alerts but nobody owns the security property being tested.
Final decision
Continuous penetration testing is valuable when it reduces the time between a risky change and a verified correction. It is not proven by scan frequency. Evaluate Penligent or another platform by its trigger quality, evidence, scope controls and retest workflow.
Annual penetration testing is a calendar trigger, not a complete strategy
An annual assessment can provide a predictable assurance point, but software and infrastructure often change between calendar tests. Treat the annual engagement as one trigger in a broader validation plan.
| הדק | פעולה מומלצת |
|---|---|
| Annual assurance date | Run the agreed baseline scope and preserve a consolidated report. |
| Major authentication or authorization change | Retest the affected roles, tenants and recovery paths. |
| New API, cloud account or agent capability | Assess the new trust boundary before or immediately after release. |
| Material vulnerability remediation | Replay the original finding and adjacent regression cases. |
| Incident or credible threat change | Run focused validation against the relevant exposure and controls. |
The program should keep scope, evidence and closure status comparable across triggers. Continuous penetration testing does not mean uncontrolled scanning; it means testing at the moments when risk assumptions change.
 Hebrew
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish