
SvelteKit's October 29, 2026 advisories cover different boundaries: Node process availability, request rerouting, Vercel route configuration and Cloudflare redirect generation. The package that needs correction depends on the deployed adapter and build path. A single “SvelteKit version” does not identify all four exposures.
This review reconciles the maintainer advisories with release notes and a Cloudflare patch. Two version statements remain inconsistent as checked November 16. Keep those exceptions visible in a change ticket instead of turning an ambiguous range into a confident safe-version claim.
Match the advisory to the package and execution stage
| Advisory | Package or path | Security property to review |
|---|---|---|
| CVE-2026-128123 | @sveltejs/adapter-node, proxying via fetch | Attempted mutation of immutable headers can crash the process |
| CVE-2026-128117 | @sveltejs/kit, a custom reroute hook on Node | Rewriting a malformed pathname can leave an unhandled URI error |
| CVE-2026-128121 | @sveltejs/adapter-vercel ו @sveltejs/adapter-static | Prerendered paths must remain literal paths in generated route patterns |
| CVE-2026-128122 | @sveltejs/adapter-cloudflare | Prerendered redirect paths must not become additional redirect rules |
ה Node proxy advisory concerns an adapter. The reroute advisory instead lists the Kit package. Updating one dependency does not establish that the other changed. Capture the resolved dependency tree, lockfile revision, selected adapter, build job and deployed artifact together.
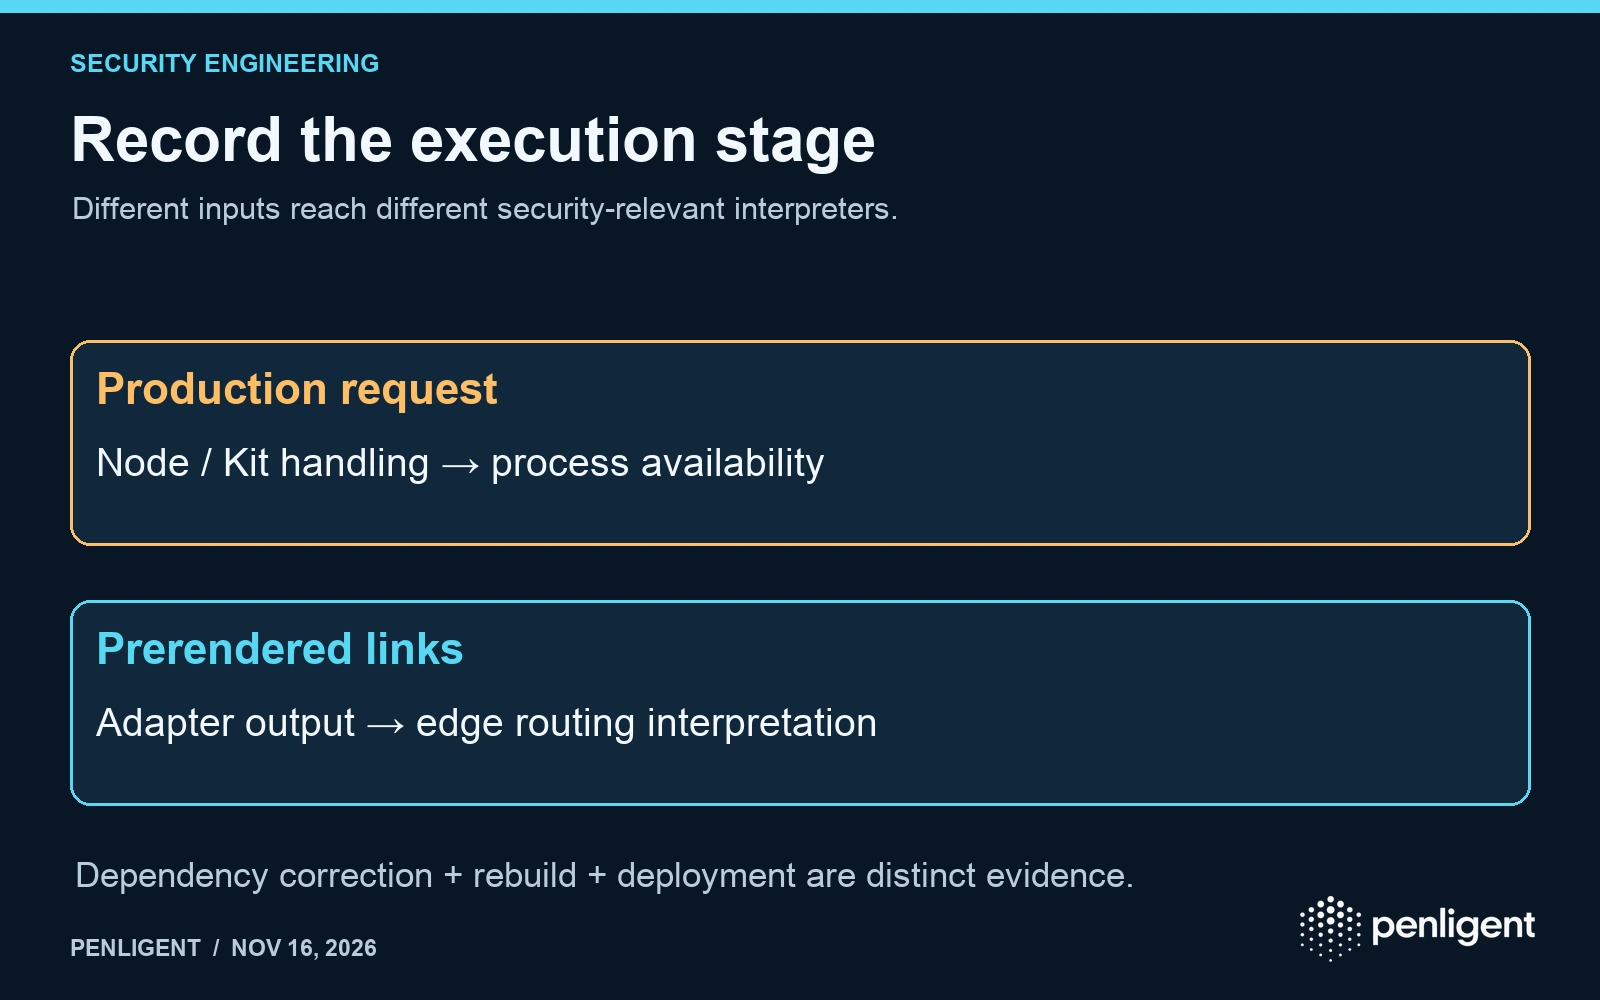
The generated-configuration issues also have input prerequisites. The Vercel advisory concerns influence over prerendered paths. The Cloudflare advisory concerns redirect paths discovered while prerendering. Check whether externally supplied content can affect the build's crawled links or paths. These are not blanket claims that every incoming production request can rewrite a deployment.
Resolve the version exceptions before approving a branch
| רכיב | Maintainer's listed correction | Qualification as of November 16 |
|---|---|---|
@sveltejs/kit reroute issue | 2.70.4 or 3.1.1 | Advisory lists affected versions through 2.70.3 and 3.0.0–3.1.0 |
| Node adapter proxy issue | 6.0.1 | Advisory's affected range includes 5.5.8, whose release notes describe a corresponding fix |
| Vercel adapter | 6.3.5 or 7.0.2 | Advisory also includes 6.3.5 in its affected range |
| Static adapter | 3.0.11 or 4.0.1 | Match the package's own branch rather than Vercel numbering |
| Cloudflare adapter | 7.2.10 or 8.0.2 | Advisory lists 4.7.0–7.2.9 and 8.0.0–8.0.1 as affected |
The official Node adapter 5.5.8 release says it avoids a crash when a text/event-stream response has immutable headers. That conflicts with treating every version below 6.0.1 in the advisory range as necessarily uncorrected. This review therefore does not certify 5.5.8 or another 5.x build as safe. For a maintained 5.x deployment, obtain a supplier determination tied to the exact fix; a compatible supported 6.x release containing the explicitly listed correction avoids relying on that disputed boundary.
The official Vercel adapter 6.3.5 release describes escaping prerendered paths used in route patterns. This supports the presence of a correction in that release, but the advisory's simultaneous affected and patched labels remain an editorial inconsistency. A deployment staying on 6.x should retain the maintainer's clarified determination and patch identity. The separately listed 7.0.2 correction does not have that overlap. Major-version migration still requires application compatibility checks.
Read the Cloudflare change as an artifact boundary
ה linked Cloudflare correction changes redirect generation rather than adding an application login check. Its escaping routine percent-encodes separators, control characters and relevant Unicode characters in generated from/to tokens. The generator also skips paths containing wildcard or placeholder syntax and emits a warning.
The change also keeps wildcard paths out of generated route exclusions, preserving exact handling in the worker. That detail matters when reviewing the build: merely finding an escaped _redirects entry is not enough if an associated route exclusion would make a different component handle the request.
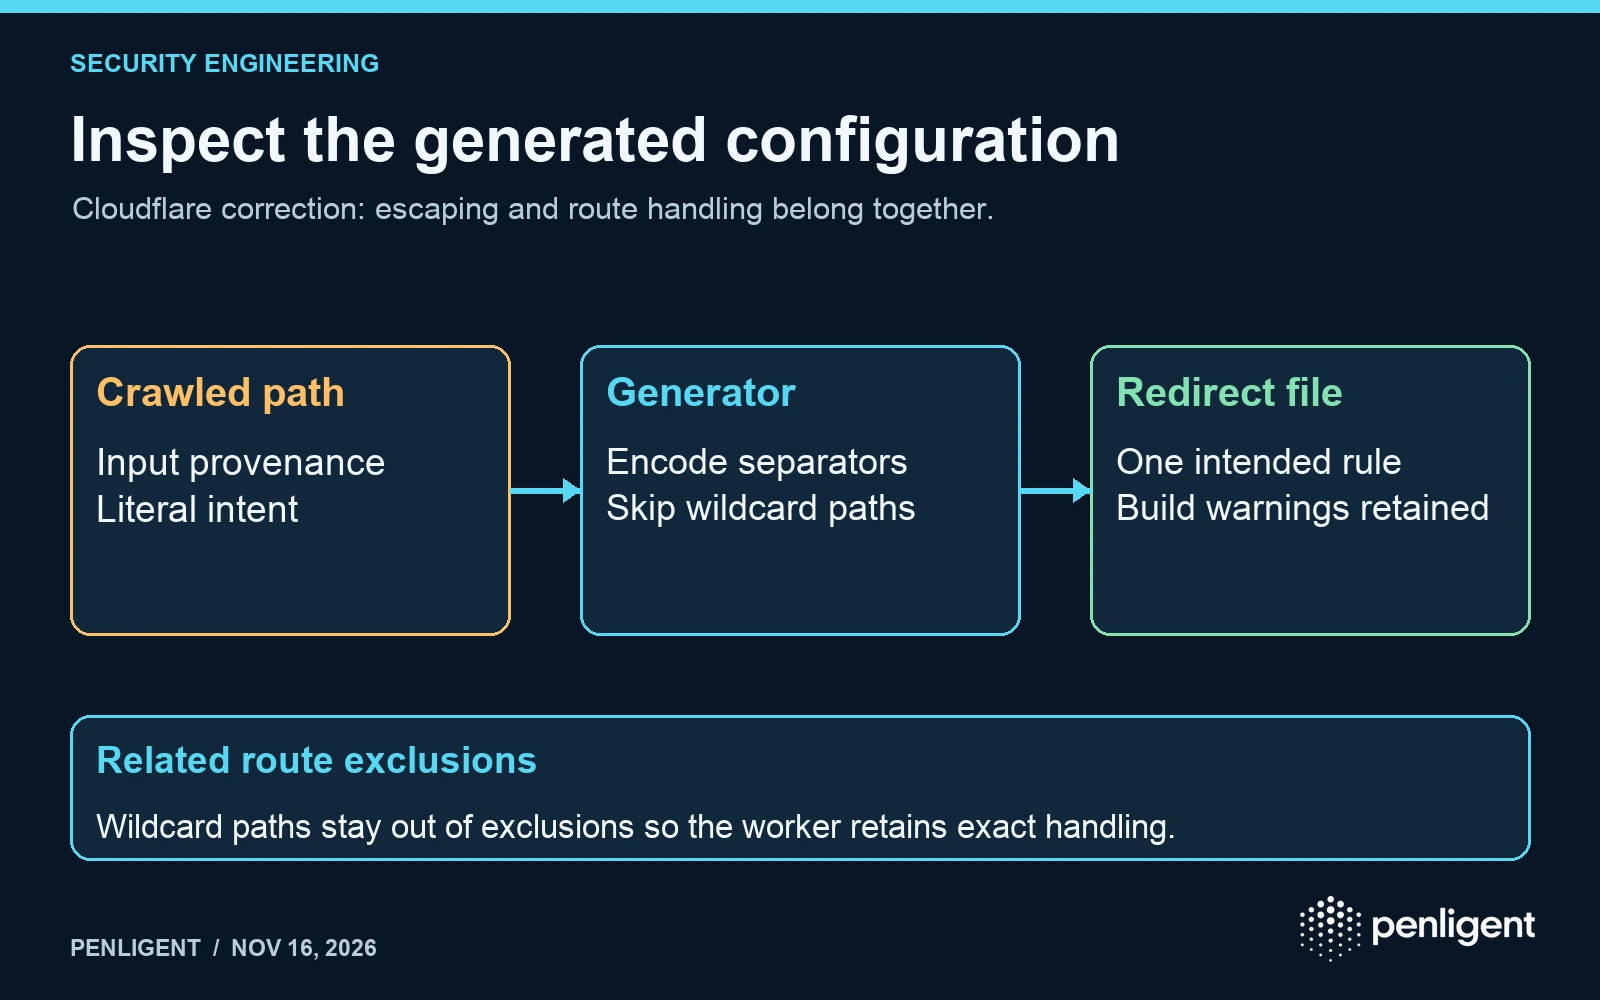
Inspect the actual output retained by the deployment job. Relate each generated entry to the intended application route, its literal or pattern interpretation, and the component that handles it. Keep warnings from the build and check whether they indicate a route was omitted. Do not assume that changing a lockfile republishes the configuration already running at the edge.
Use two acceptance records
For runtime issues, record the active Node artifact and an approved staging check of the relevant proxy or reroute behavior. A normal request should work, and a bounded malformed-input check should not terminate the process. This article does not supply a public-target crash payload or claim that such a test has been executed.
For generated configuration, retain a clean rebuild's route files, the source revision, dependency resolution and publication record. Compare representative literal paths and redirects with the intended routing behavior. An ordinary page-loading check may miss a rule that only applies to a different path. Run tests within an owned staging deployment using benign paths selected by its maintainer.
The closure decision needs both the supplier correction and evidence that the corrected artifact serves traffic. Record any unresolved branch ambiguity explicitly. These package advisories alone do not establish exploitation of a reader's service or provide an incident-wide clean bill of health.
Method: AI-assisted review of maintainer advisories, release notes and the linked Cloudflare code change, checked November 16, 2026. The acceptance model is proposed analysis; no application, exploit or performance benchmark was run.
ה patch verification workflow provides the broader evidence handoff. For SvelteKit, keep runtime activation and regenerated routing artifacts as distinct observations in that record.
General product workflow
The official Penligent 3.0 demonstration shows a general authorized testing workflow. It does not verify these adapters, resolve the version inconsistencies or demonstrate exploitation of the listed CVEs.
 Hebrew
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish