
CVE-2026-90817 is an unauthenticated REDCap remote-code-execution vulnerability that requires knowledge of a valid public survey hash. CISA added it to KEV on November 18, 2026, with forensic triage marked “Yes” and a November 21 due date in the applicable directive context. The practical task is to identify the installed REDCap branch, obtain its supported remediation and assess public survey routing without accessing participant data.
Unauthenticated does not mean without a prerequisite
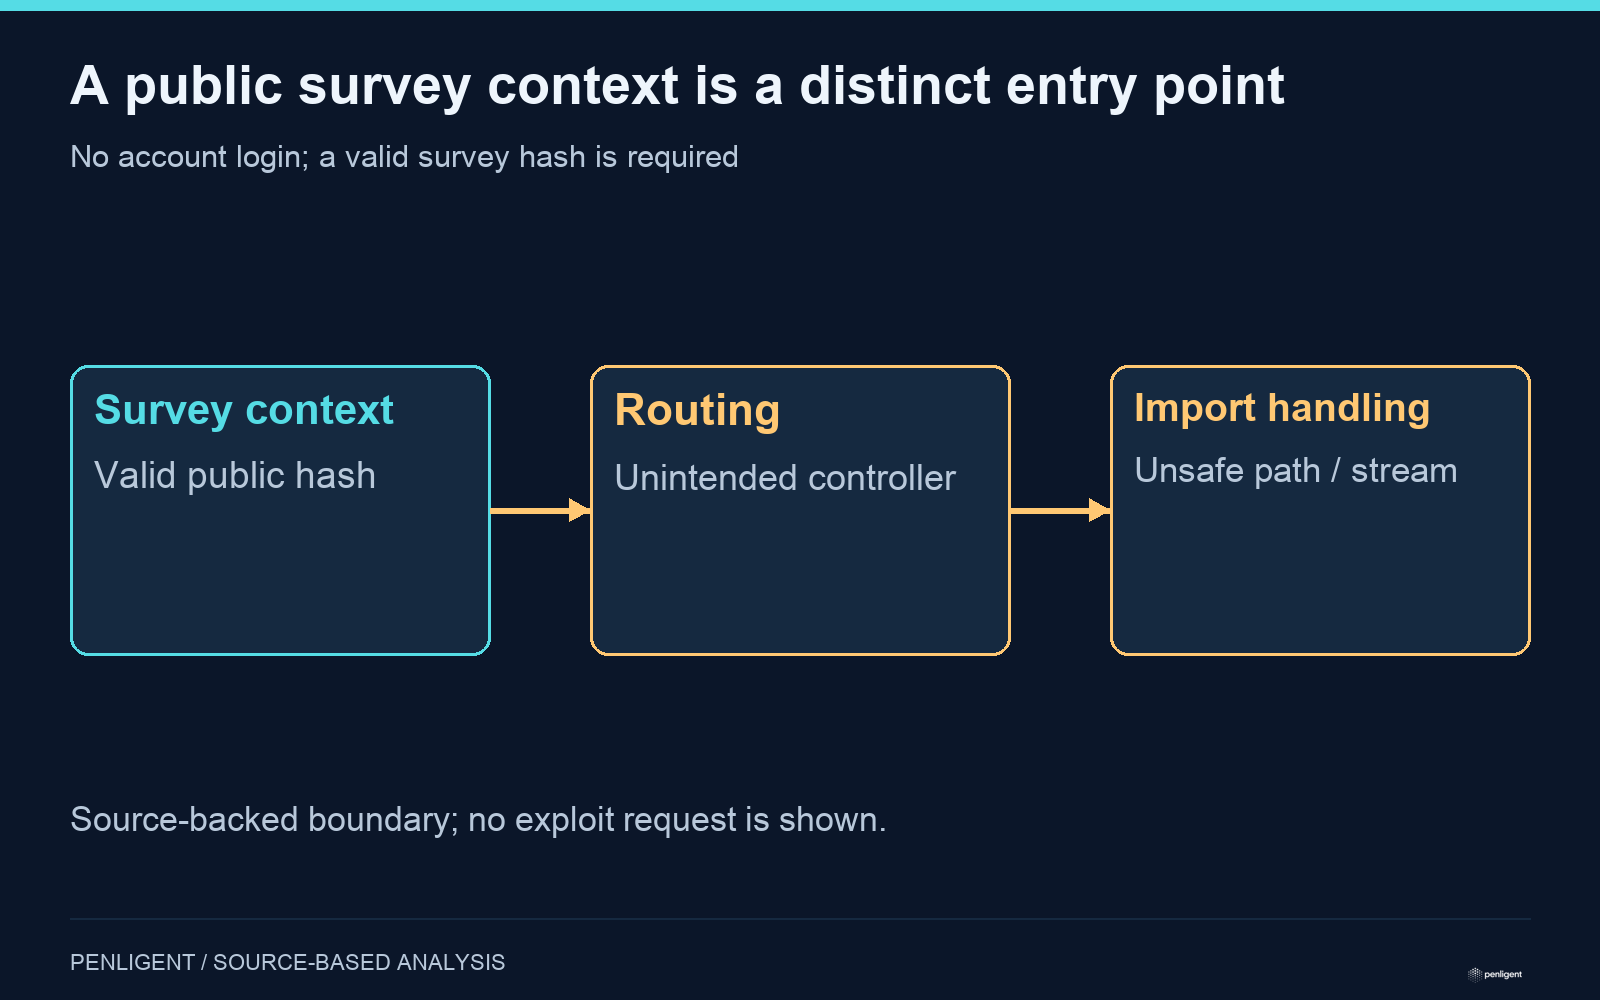
The CNA record describes survey passthrough routing that reaches an unintended controller path and unsafe file-path or stream handling during data import. It explicitly requires a valid public survey hash. A public-survey link is not a user login, so disabling ordinary account registration does not answer this exposure question.
Inventory the application’s public survey entry points, reverse-proxy routes and deployment ownership using approved administrative records. Do not collect live survey responses to establish reachability. A missing survey link in one asset spreadsheet is not proof that no public survey exists, and a single public survey does not establish that an unpatched server was exploited.
Use the enumerated releases without inventing a full range
| CVE record evidence | Supported conclusion | What remains to verify |
|---|---|---|
| Description says 13.3.0 and higher | The vulnerable behavior dates to that line according to the CNA | The prose is not a complete branch-by-branch patch table. |
| 16.0.49 marked unaffected | This exact release is explicitly identified as unaffected | Confirm the correct supported update path for the installed branch. |
| 17.3.10 marked unaffected | This exact release is explicitly identified as unaffected | Do not map its number onto the 16.0 branch. |
| 17.4.4 marked unaffected | This exact release is explicitly identified as unaffected | Check current vendor guidance for later supported maintenance. |
| Default structured status is unknown | Unlisted releases are not automatically certified unaffected | Obtain vendor confirmation or the branch-specific advisory. |
The narrative and structured fields have different precision. It would be misleading to convert “13.3.0 and higher” into a claim that the listed unaffected builds are vulnerable, or to infer a complete set of fixed ranges that the record does not enumerate. Preserve the exact installed release and its supplier evidence. A later-looking version string alone is insufficient for an unsupported branch or a locally modified deployment.
Get the branch-specific advisory through the supported channel
CISA points operators to the REDCap community. Access may require an institutional account; the community’s restricted remediation details were not reviewed for this article. The public version statements above are limited to the CNA record. Ask the authorized institutional REDCap administrator or vendor channel for the applicable patch package, upgrade requirements and change notes.
Do not improvise a route filter or remove a controller based only on the short CVE description. A partial routing change can disrupt legitimate survey or import behavior and may leave another supported route reachable. Use vendor instructions and separately verify normal public surveys and authorized imports in an owned staging environment with synthetic records.
Maintain three evidence tracks
| Track | Evidence to retain | Separate question |
|---|---|---|
| Software remediation | Branch, active release, vendor advisory, deployment and restart evidence | Did the intended fixed code reach every relevant application node? |
| Public survey boundary | Owned survey entry points, proxy mapping and expected access behavior | Which routes were reachable during the exposure window? |
| Historical triage | Available application, access, host and change records under approved handling | What evidence exists of activity before remediation? |
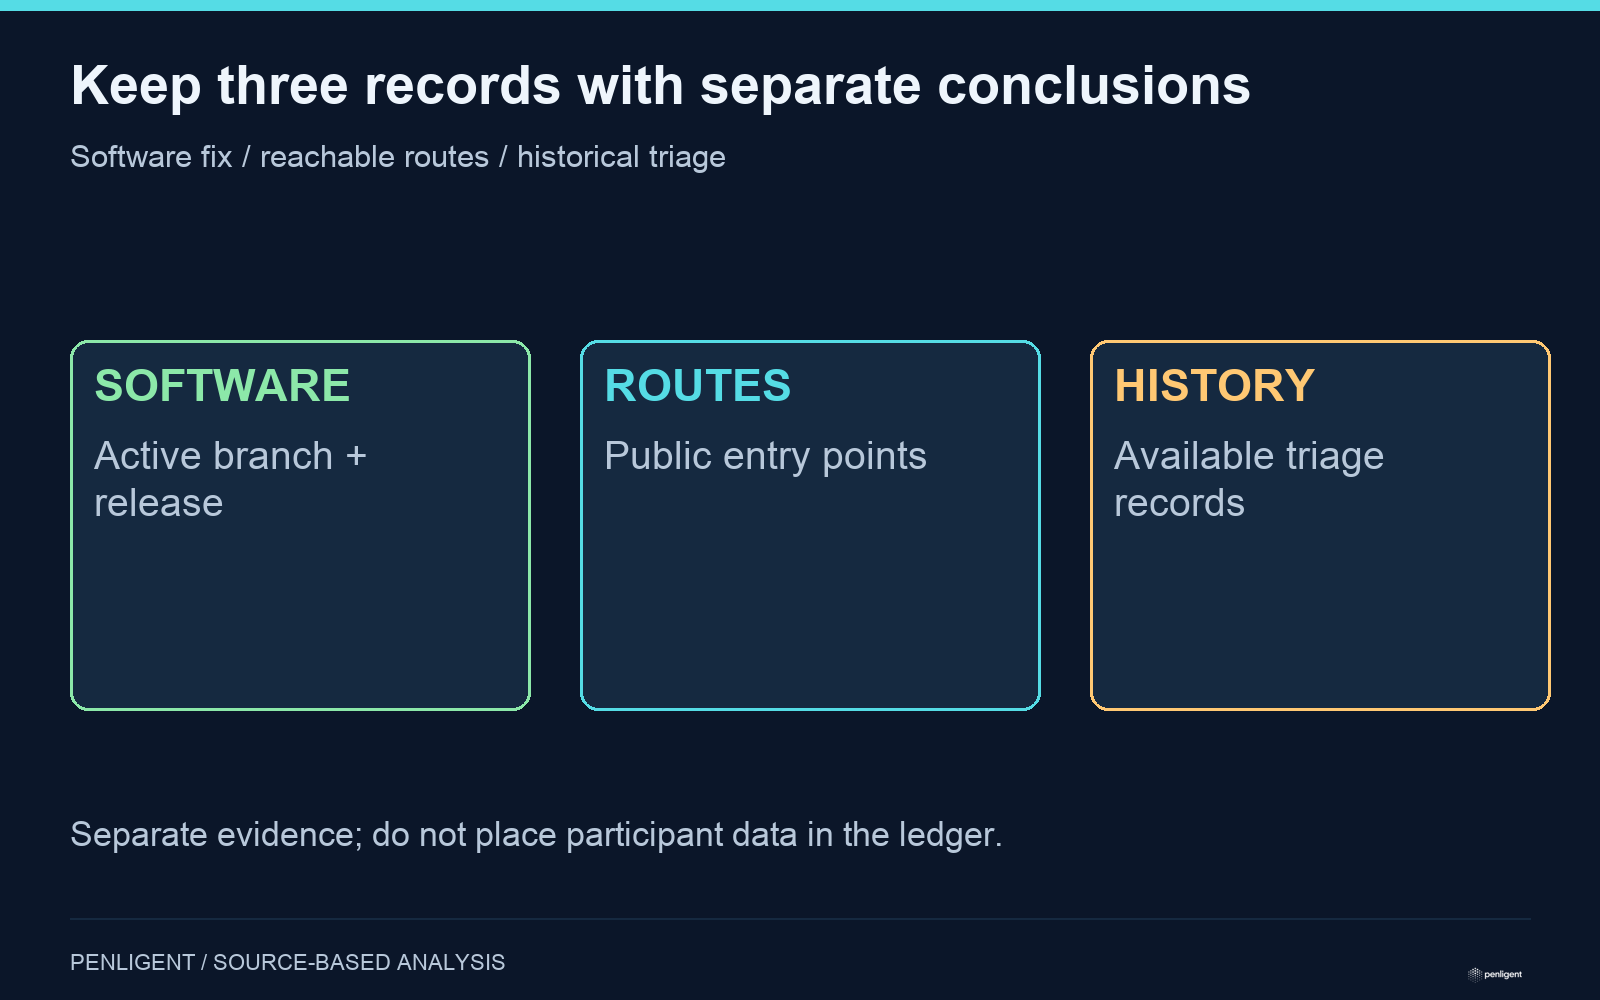
The proposed ledger should contain identifiers and evidence locations, not participant responses, medical information, survey hashes or credential values copied into public tickets. Known exploitation increases urgency but does not identify which institution or dataset was affected. Preserve the available evidence before routine maintenance overwrites it, following institutional incident procedures.
Close the actual deployment, not just the change ticket
Verify the active release across application nodes, the approved route behavior and a normal synthetic import after the supported update. Record what could not be verified. If the vendor community record is unavailable to the responder, that is a specific missing dependency for branch confirmation, not a reason to invent remediation details or certify the deployment safe from the public summary alone.
The following Penligent 3.0 video is a general product workflow demonstration. It is not evidence of exploitation or proof that this vulnerability was remediated.
Methodology, November 19, 2026: AI-assisted drafting with agent verification against the linked primary records and source changes. The deployment decisions and proposed acceptance checks are analysis. No exploit was executed and no first-hand incident response is claimed.
 Hindi
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Arabic
 Turkish
 Hebrew