
The European Commission publicly confirmed an AI-related cybercampaign on November 19, 2026, and said it had detected the incident on October 22. These are different dates. The event should not be described as a new November 20 intrusion. Reuters’ report of spokesperson Thomas Regnier’s briefing says several applications were temporarily taken down as a precaution, most had been restored, and investigation continued.
What the public statement does and does not establish
The spokesperson characterized the campaign as involving AI and said there was no evidence of a breach affecting Commission staff as a whole. He did not attribute the attack publicly and was not aware of a ransom demand. Preserve those qualifications: the statement is neither proof of complete data safety nor confirmation of a staff-wide breach. Exact scope remained unresolved in the reported briefing.
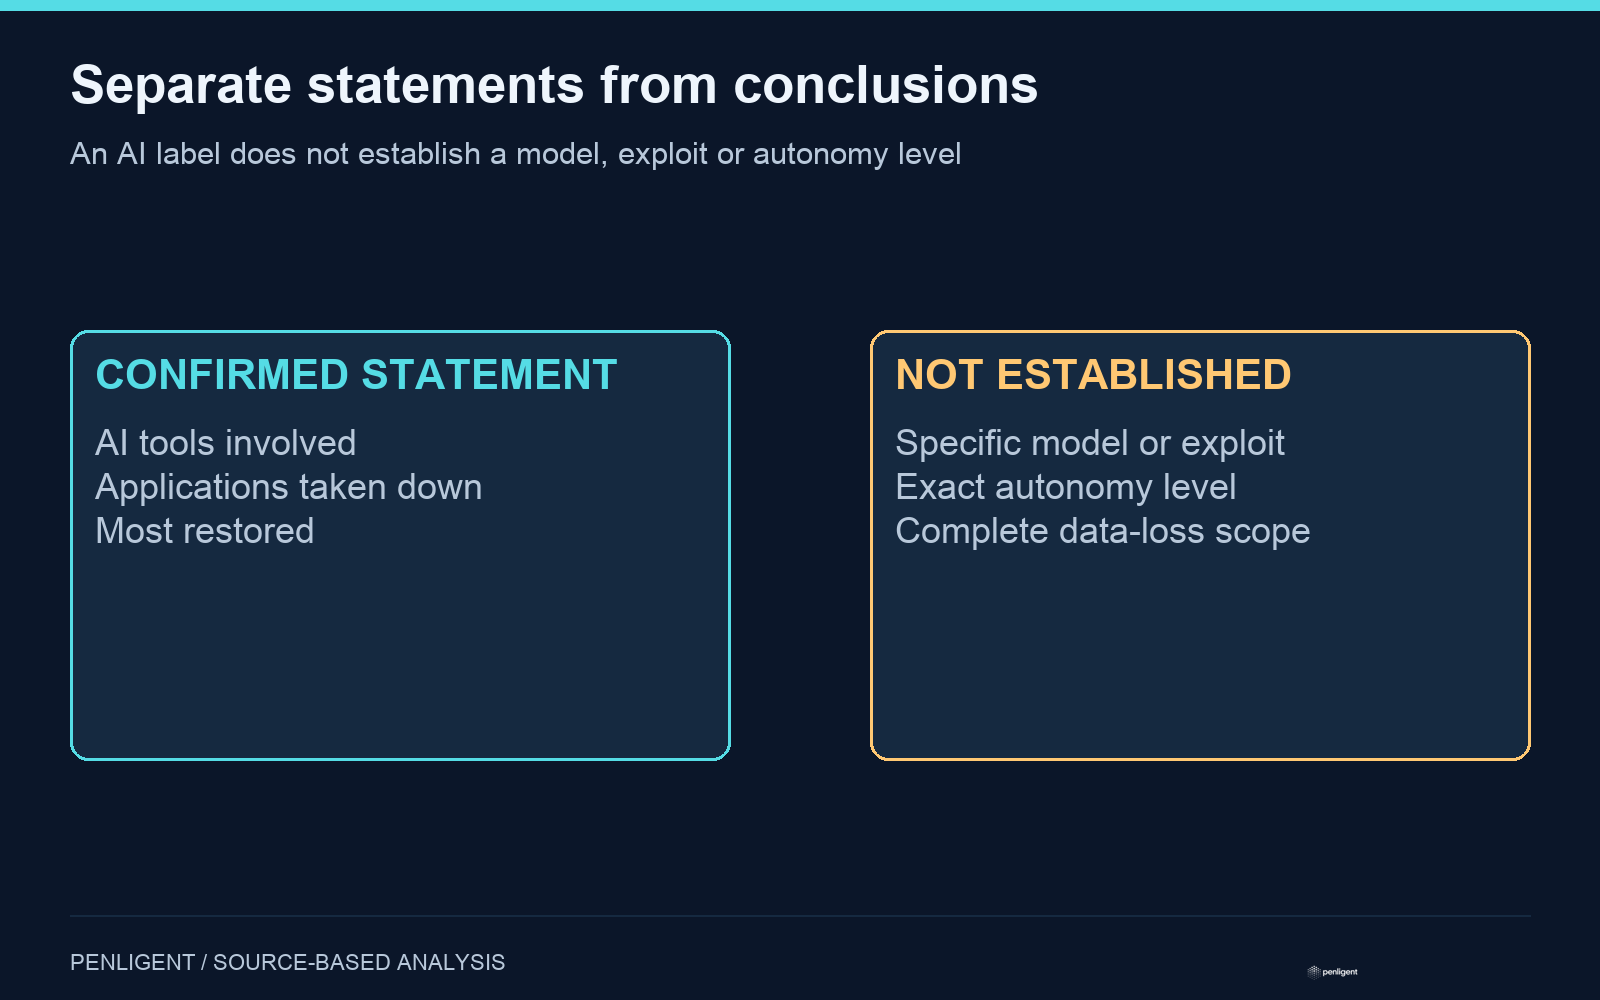
The public account does not identify the full technical chain, exact model, amount of human supervision or a verified exploit. An AI-related incident is also not automatically an attack against an AI application. It may describe the attacker’s tooling. A defender should determine which meaning the source supports before creating detections, assigning a vulnerability or changing a system.
Use an evidence ladder for AI attack claims
The following framework is proposed analysis for security engineers evaluating similar reports. It separates evidence that an organization was targeted from evidence of the attacker’s implementation. Each step requires its own supporting artifacts; a polished generated report is not a substitute.
| Claim | Evidence that would support it | Do not infer |
|---|---|---|
| AI tools were involved | Attributed official statement or a research report with disclosed method | The specific model or provider. |
| An agent acted autonomously | Tool-action traces, operator decisions and the boundaries of the observed run | Complete independence from a human based only on the word AI. |
| A vulnerability was exploited | Affected component and code path plus correlated technical evidence | A new zero-day from an application shutdown. |
| Data was accessed or removed | Authorized investigation findings tied to records and time | Staff-wide data theft from precautionary downtime. |
Build a timeline that separates detection from exposure
For an organization’s own incident, keep first observed activity, detection, containment, restoration and disclosure as separate timestamps. Record the timezone and the source for every entry. An unknown start remains unknown even if the detection time is precise. A later public announcement should not reset the exposure window or imply that mitigation began only on that date.
In a response ledger, add the affected application, identity boundary, available logging period and the owner responsible for each gap. Collect only the information necessary for the approved investigation. Retain relevant identity and application records before routine expiration, and document absent telemetry without converting absence into a negative compromise result.
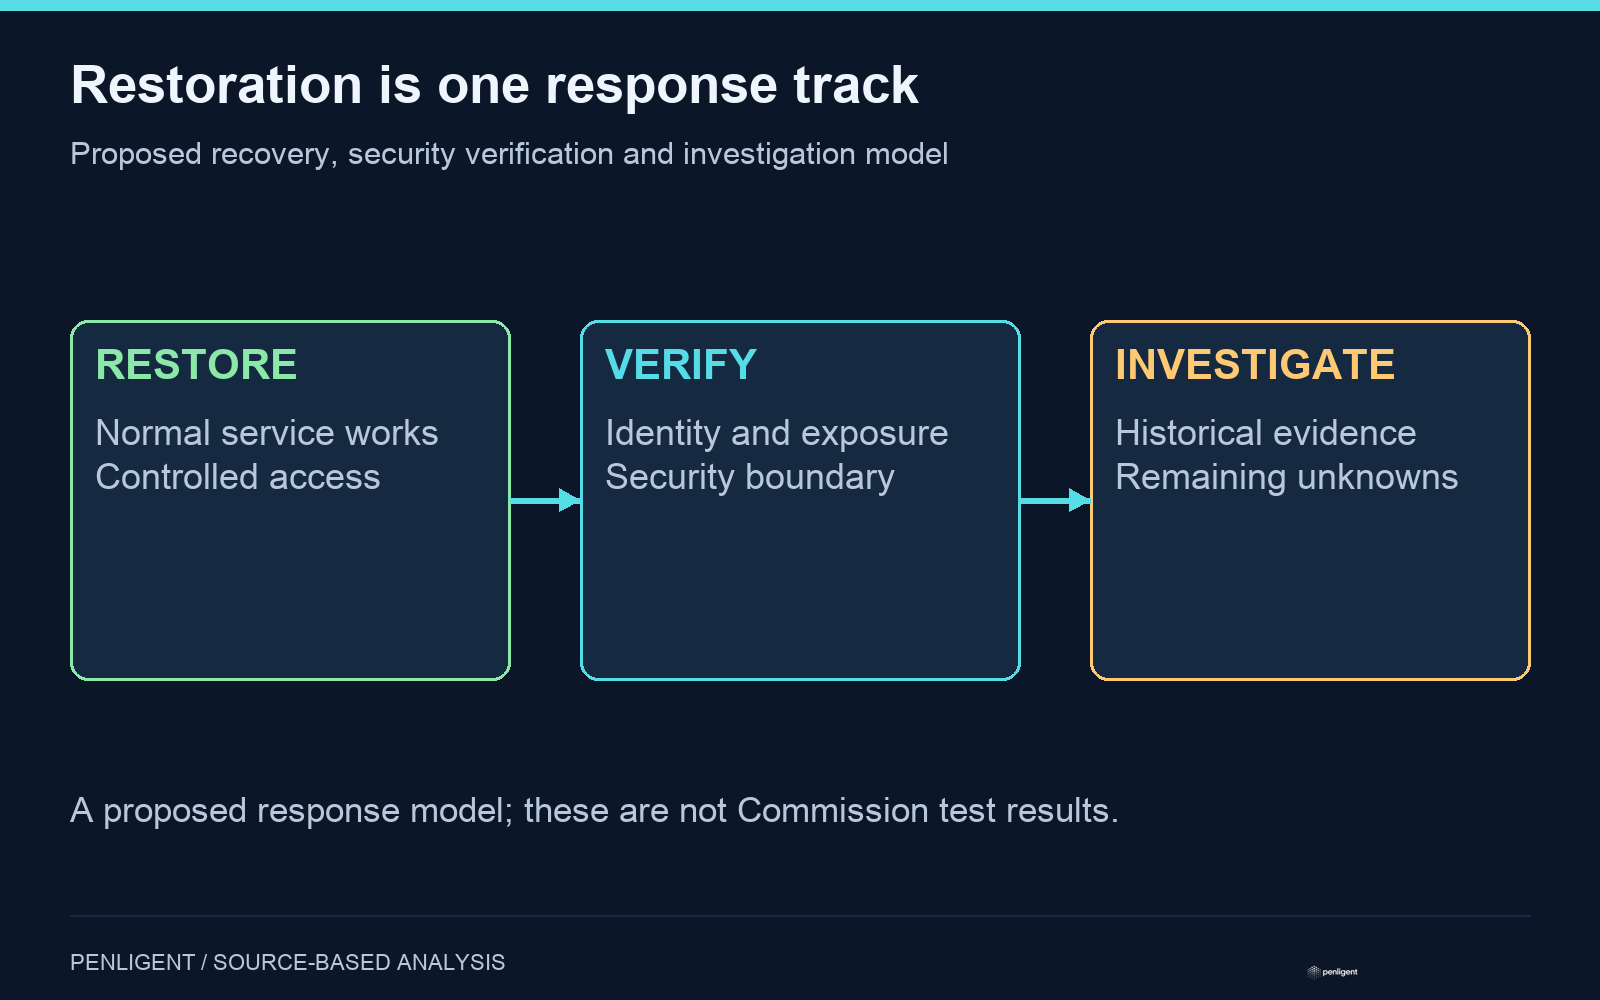
Treat restoration and security closure as separate decisions
A restored application shows that a selected workflow is available. To support a security closure decision, define a separate acceptance condition: the relevant access path has been contained or corrected, expected authorized use still works, and an explicitly unauthorized operation remains denied in an owned test environment. Use synthetic records and dedicated test identities. Do not test a third party’s live systems to investigate a news report.
An incident owner can close an operational recovery ticket while historical investigation remains open. Give unresolved questions an owner and a next evidence source. This is more useful than assigning a single green status to the whole event or treating every precautionary shutdown as confirmed attacker control.
Choose defensive work that survives uncertainty
Review the organization’s exposed applications, identity permissions and deployment evidence against verified advisories. If authorized automation assists testing, enforce target scope and tool permissions outside generated text, retain the tested identity and observed result, and stop when evidence cannot support the next action. These are proposed testing controls, not claims about the Commission’s architecture or the attacker’s exact workflow.
The immediate value of this disclosure for defenders is a disciplined distinction between public statements, technical evidence and remaining uncertainty. It does not justify inventing a payload, exploit signature or affected-version list that has not been disclosed.
The official Penligent 3.0 video below demonstrates a general product workflow. It is not evidence of this incident, exploitation or remediation.
Methodology, November 20, 2026: AI-assisted drafting with agent verification of the public briefing statements reported by Reuters. No Commission system, private investigation record or attack artifact was accessed. The evidence ladder and response worksheets are analysis; no first-hand exploit or incident-response work is claimed.
 Japanese
 English
 German
 French
 Spanish
 Portuguese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew