
Last updated: November 4, 2026.
Fintech penetration testing must examine how identity and business state control money movement. Traditional web and API vulnerabilities still matter, but the highest-impact failures often involve account recovery, payment authorization, transaction replay, limit enforcement, refunds, ledger consistency or privileged operations.
Testing should use synthetic accounts and approved transaction paths wherever possible. The rules of engagement must define real payment processors, settlement systems, fraud controls, notifications and third-party services that could be affected.
For the assessment framework, consult OWASP ウェブ・セキュリティ・テスト・ガイド and map the relevant guidance to the actual environment and authorized scope.
Map the complete money and authority flow
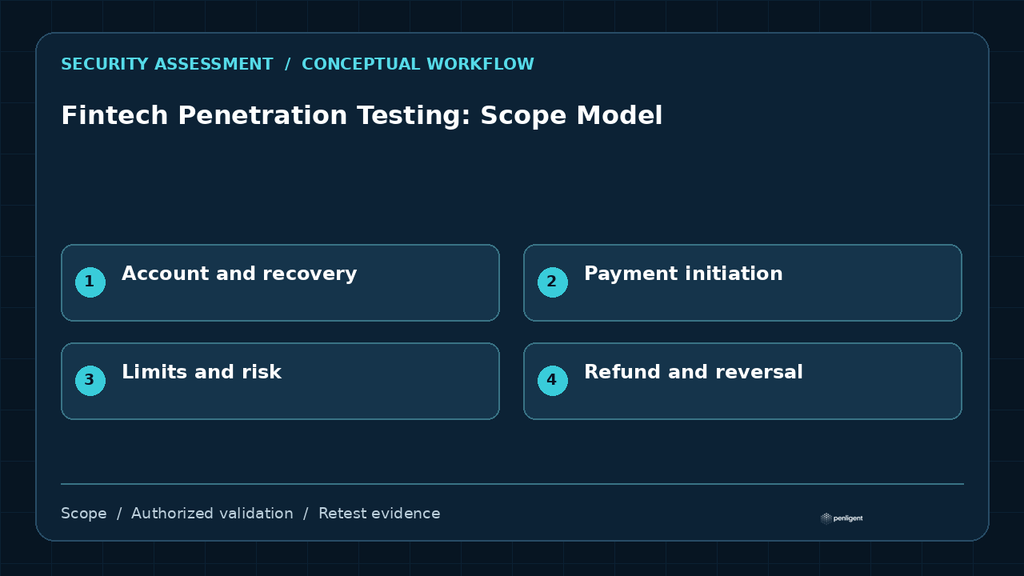
Document who can initiate, approve, reverse, refund, withdraw or administer a transaction, and how the state changes across synchronous and asynchronous components.
| Workflow | Security question | エビデンス |
|---|---|---|
| Account and recovery | Can an attacker take over or weaken a trusted identity? | Session, recovery and step-up results |
| Payment initiation | Are amount, recipient and funding source bound to authorization? | Signed request and state transition |
| Limits and risk | Can concurrency, retries or alternate channels bypass controls? | Counter, timing and decision evidence |
| Refund and reversal | Can state or entitlement be duplicated or detached? | Order, refund and ledger linkage |
| Administration | Can privileged actions be invoked or approved by the wrong role? | Role matrix and audit event |
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Test race, replay and idempotency safely
Concurrent requests and retries can expose double-spend or duplicate-action conditions. Use capped synthetic values, dedicated accounts and explicit stop conditions. Record request identifiers, timestamps and final ledger or workflow state instead of generating uncontrolled volume.
Include fraud and support operations
Customer support, manual review, promotions, dispute workflows and administrative overrides frequently cross trust boundaries. Test whether ordinary users can reach privileged states and whether internal roles have excessive or unaudited authority.
Deliver evidence across engineering and risk teams
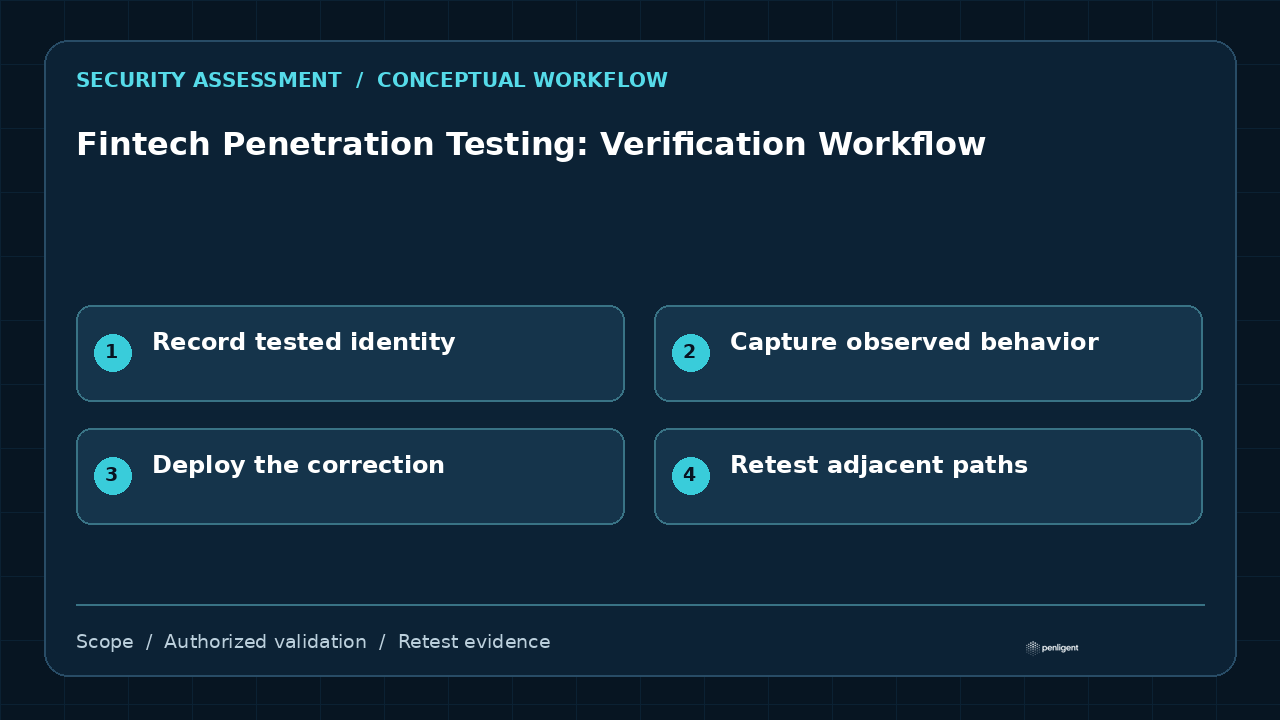
A finding should show the user role, account or tenant, transaction state, expected invariant and observed result. The retest should confirm the fix under normal, retry and concurrent conditions and verify the relevant audit trail.
Turn the scope into testable evidence
Define an authorized target, validate meaningful attack paths, and keep the evidence connected to remediation and retesting.
Questions buyers should ask
- Which synthetic payment, refund and withdrawal actions are authorized?
- Are support, fraud and administrative roles included?
- How will concurrency and replay be tested without financial impact?
- Does the report connect application evidence to ledger and audit state?
結論
Fintech testing is effective when it proves that identity, transaction state and risk controls preserve financial invariants. Scope the entire workflow, use safe synthetic transactions and require retest evidence for normal and adversarial sequences.
 Japanese
 English
 German
 French
 Spanish
 Portuguese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew