
Devin Security deserves evaluation around a concrete risk decision: what could go wrong in your application, which evidence supports the finding, and what would let its owner close the work? A scan result, an approved risk exception and a deployed correction require different records. A useful pilot makes those differences visible before the team grants broad access or commits to a larger deployment.
This review examines the public announcement available on October 27, 2026. We have not run Devin Security, measured its detection rate or inspected a customer engagement. The access matrix and payment-webhook scenario below are proposed evaluation methods, not descriptions of a tested product integration.
What the Devin Security announcement establishes
In its October 26 announcement, Cognition describes an enterprise upgrade combining threat modeling, deep scans using Claude Mythos and other models, imported findings, contextual prioritization and remediation. It says risk adjustments require human approval, retain the original CVSS score and exclude KEV-listed vulnerabilities from relabeling. With configured access, infrastructure mitigation can reduce exposure while leaving the flaw open. Its code-fix workflow uses independent VMs, reproduction checks, existing tests and evidence-bearing pull requests.
The announcement offers enterprise scans and remediation credits through contact with Cognition. It does not provide a numeric price for the engagement described there. Confirm eligibility, scope, allowance, expiration and subsequent charges in writing. These are vendor statements and an offer, not independently measured coverage or savings.
The separate Devin Vulnerability Fixes repository contains three Agent Skills for runtime remediation. Installing those instructions does not establish entitlement to the enterprise service. Evaluate the product and the Skills as different purchasing and operating questions.
Decide what the assessment may read and change
Start with a written permission boundary. Repository visibility, test execution, deployment access and permission to change production controls are separate grants. An operator who needs to inspect a service should not automatically receive authority to alter its network policy. Stage the permissions so the first assessment can finish with a reviewable proposal before any broader change is enabled.
NIST SP 800-115 frames technical testing as planning, execution, analysis and mitigation, with attention to technique limitations. For an agent-driven pilot, make the planning record operational: name the owned targets, permitted accounts, allowed methods, data restrictions, stop conditions and person able to halt execution. An instruction in a task description should not be the only boundary protecting an unrelated repository or account.
| Permission | First-pilot boundary | Record before expanding |
|---|---|---|
| Code and configuration reads | Named repository, branch and deployment manifests | Inventory of material made available and omissions |
| Test execution | Owned staging service with synthetic records | Allowed traffic, test identities and stop contact |
| Proposed code changes | Dedicated branch; human review before merge | Diff, test results and unresolved assumptions |
| Infrastructure changes | Review proposal first; separate authorization to apply | Exact rule, affected service and rollback owner |
| Production rollout | Existing release process and responsible owner | Serving artifact and post-deployment checks |
Ask the supplier how secrets, tool outputs and source material move through the proposed configuration. Request the relevant retention, deletion, model-provider and support-access terms. A product demonstration cannot answer these contractual questions for a private application. Keep anything not yet confirmed as an open procurement item, rather than filling the gap with assumptions about the deployment label.
Use a payment webhook to test the quality of the threat model
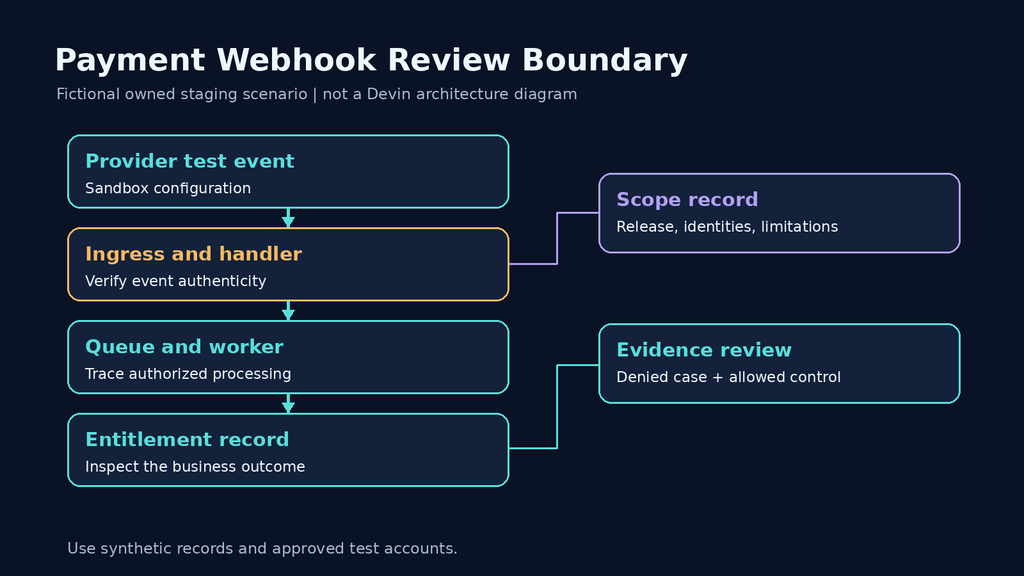
Consider a fictional SaaS service in an owned staging environment. A payment provider sends an event to an ingress route; the handler authenticates the event, places work on a queue, and a worker updates subscription entitlement. The business concern is a paid entitlement being granted without an authorized payment event. This is an evaluation scenario, not a reported vulnerability in Devin, Stripe or Penligent.
The application owner supplies the intended rule and names each relevant component. Give the evaluator only sandbox credentials, synthetic customers and a non-production payment configuration. Record whether ingress, application code, queue configuration and entitlement processing are all available for review. A missing worker should become a stated scope gap, not an implicit assumption that the handler controls the whole outcome.
Stripe’s webhook documentation requires signature verification using the raw request body, signature header and endpoint secret, and warns that changing the raw body breaks verification. For a Stripe-based fixture, use its supported testing workflow and SDK guidance. The review should establish where verification occurs and whether the business action is gated on its success; a recognizable header name alone is insufficient evidence.
Ask for a traceable explanation of the proposed finding: the event entry point, the relevant configuration, the decision that authorizes queueing, and the resulting entitlement transition. If the evaluator cannot establish one of those links, the finding should identify what remains unverified. The useful artifact is an argument an engineer can challenge, not a confident narrative built from an incomplete route map.
Give each disposition its own acceptance test
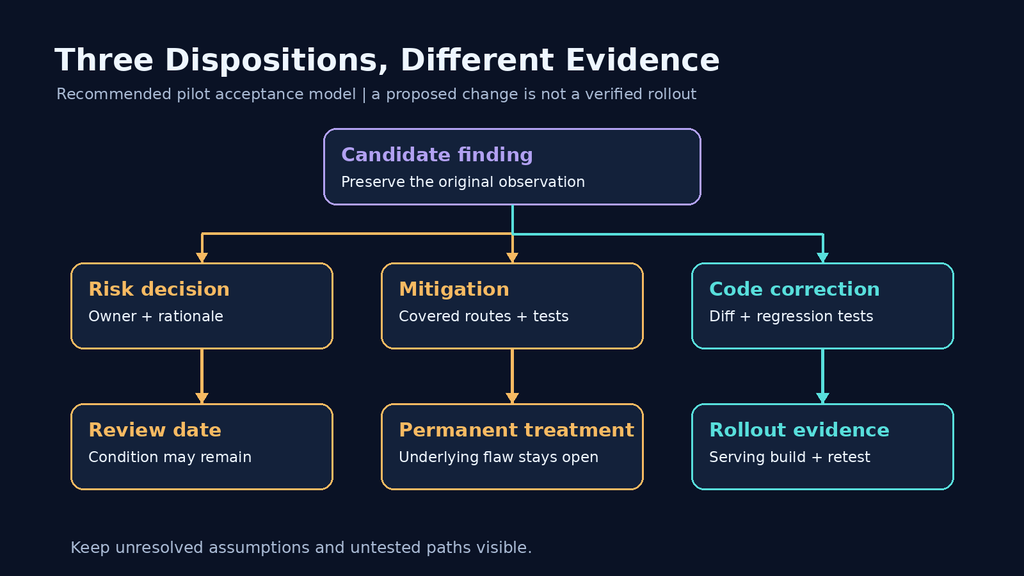
The same candidate issue may lead to a documented exception, an exposure-reducing infrastructure change or a source-code correction. Define which outcome the pilot is intended to demonstrate. A changed severity label does not alter the handler. A new network rule does not change an authorization decision inside the application. A corrected branch does not prove that the serving release contains it.
For the fictional webhook, an ingress rule could reduce exposure to the affected route. Record which path the rule covers, whether another ingress remains reachable and how legitimate payment events continue to arrive. If the underlying application defect is still present, preserve its status and assign a permanent treatment owner. Availability loss should not be mistaken for a successful security correction.
| Disposition | Evidence to request | What remains open |
|---|---|---|
| Risk adjustment or acceptance | Reasoning, original observation, owner approval and review date | The technical condition and validity of the assumptions |
| Infrastructure mitigation | Applied configuration, covered routes, rejected case and legitimate flow | Underlying defect and any uncovered access path |
| Code correction | Reviewed change, affected behavior and regression results | Rollout to each relevant deployment |
| Deployment verified | Serving artifact identity and scoped application checks | Untested paths, later changes and any incident investigation |
For a code correction, use an approved invalid-event case that cannot grant entitlement, plus a valid provider test event that produces the expected sandbox state. Add the relevant repeated-delivery behavior required by your application. Check the business outcome, not only the HTTP status: an accepted response with an unauthorized queued job is different from a rejected request, and an error response may still leave side effects.
Keep the test identity and configuration consistent enough to interpret the comparison. If the replacement deployment changes queueing or processing behavior, update the test plan before reporting closure. Record an unresolved observation as unresolved. A security reviewer needs to see the mismatch rather than discover later that a failed case was removed from the comparison.
Budget the pilot around a completed decision
Before accepting a free evaluation or a paid proposal, agree the unit of work. “One application” could mean a repository, an exposed service, several authenticated workflows or a larger deployment estate. Name the included environments, assessment depth, reviewer handoff and retest obligation. Ask what happens when the first useful finding requires access beyond the initial scope.
Build a pilot estimate from supplier charges, model or runtime charges where separately applicable, environment preparation, engineer review, regression testing and rollout work. Record which amounts are quoted, included, measured or still unknown. A promotional allowance can reduce an invoice while leaving substantial internal work; conversely, a low finding count may be reasonable for a well-tested application.
Measure the time until an owner can make a supported decision. Track how long it takes to resolve an access blocker, review a candidate issue, reproduce the relevant behavior and assess the proposed treatment. Keep supplier waiting time and your own engineering time visible. Do not calculate return on investment from the number of tickets closed without reviewing why they were closed.
Choose the testing workflow around the missing evidence
Different assessments can answer different questions about the same service. Code and deployment review can explain how a decision is implemented; authorized application testing can examine observable behavior through approved identities and routes. The pilot should expose what each assessment actually saw. Access to source code does not itself demonstrate that a production configuration was tested, and an external observation may leave the implementation cause unresolved.
| Buyer’s immediate question | Evaluation to request | Acceptance boundary |
|---|---|---|
| Why might this code path be exploitable? | Code and configuration reasoning tied to the threat model | State the unavailable deployment context |
| Does an approved application route permit the wrong outcome? | Controlled behavior test using synthetic data | Identify the tested identities, release and route |
| Did the proposed treatment work? | Specific rejected case and legitimate operation control | Distinguish proposal, tested artifact and deployed state |
| Will the recipient accept the report? | Sample deliverable and agreed assessment requirements | Confirm independence and scope requirements before purchase |
Penligent can be considered for a separate authorized application-testing evaluation. Use the same owned scope and acceptance questions when reviewing its workflow, evidence and report format. This article does not demonstrate an integration between the products, a shared finding pipeline or a comparative benchmark. Choose a workflow on the basis of the assessment it can complete in your environment.
사용 OWASP’s reporting guidance to review the handoff: explicit scope and limitations, stable finding references, actionable remediation information and protected sensitive evidence. Give the recipient enough sanitized context to understand the result and locate the restricted original. If an independent assessor or a particular engagement format is required, confirm that requirement before treating any exported report as an accepted deliverable.
A successful pilot ends with one decision another engineer can recheck. The record should explain the observation, the treatment chosen, the evidence reviewed and the work still open. That is a useful basis for expanding access or purchasing more capacity. An impressive scan or a merged pull request, on its own, leaves the most consequential part of the review unfinished.
The following video introduces a Penligent application-testing workflow. It is not a Devin Security demonstration or a head-to-head evaluation.
 Korean
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Hindi
 Arabic
 Turkish
 Hebrew