
Patching the web application that enabled initial access does not remove a remote-access process already installed on its Linux host. Microsoft’s November 11 GSocket research describes that separation directly. A useful investigation must connect application activity, process execution, persistence and outbound communication while distinguishing authorized remote administration from malicious use.
What the original research supports
Microsoft reports multiple incidents in which attackers deployed GSocket after compromising Linux web applications. It describes persistence through several host mechanisms and communication through the shared Global Socket Relay Network. GSocket also has legitimate remote-administration uses, and the relay is not infrastructure uniquely owned by one attacker.
Those observations support a behavioral investigation, not a verdict from a filename or destination alone. This guide does not download GSocket, execute its installation scripts or reproduce persistence. It proposes evidence and closure questions for systems your organization owns or is authorized to investigate.
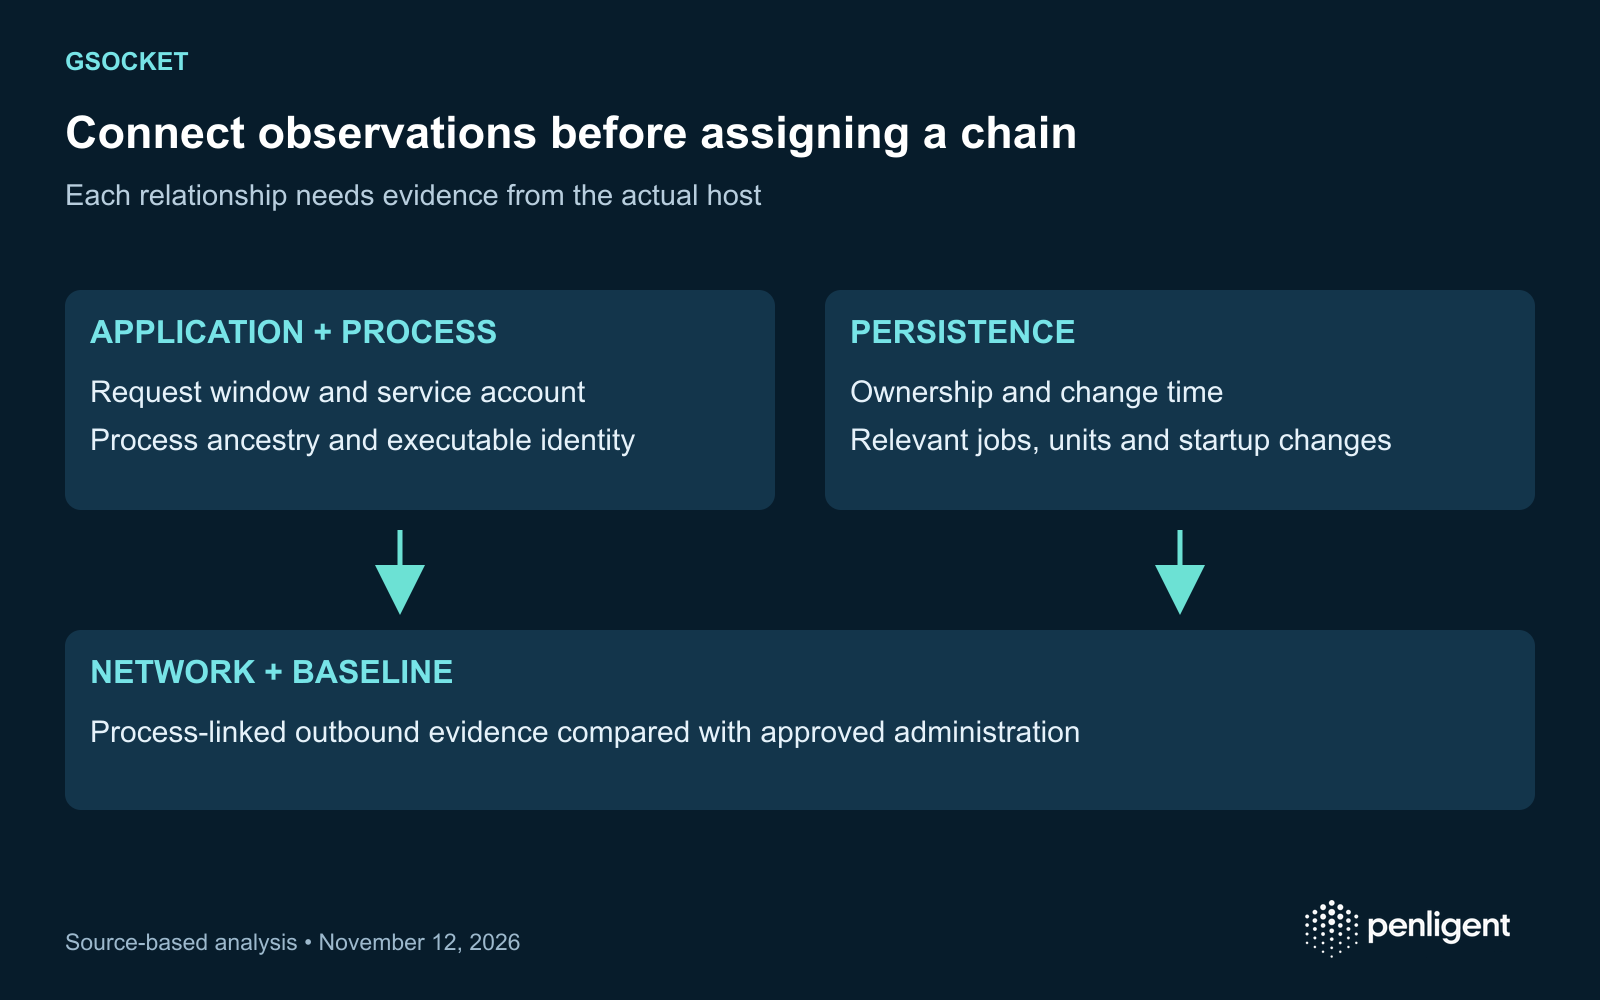
Build a timeline that can support a relationship
Start with the affected application and its service identity. Retain the suspected time window, process ancestry, file activity and available network records. Look for relationships among a web-service process, unexpected shell activity, a new executable, a persistence change and an outbound session. Do not fill a missing parent event with an assumed exploit.
| Evidence layer | What to retain | Conclusion to avoid |
|---|---|---|
| Application entry | Relevant request window, deployment version and service owner | A later remote-access process identifies the exact initial CVE. |
| Host execution | Process ancestry, executable identity, account and time | A service-like display name establishes a legitimate system process. |
| 지속성 | Relevant scheduled jobs, units and startup changes with ownership | Stopping the current process removes all ways to restart it. |
| Outbound connection | Process association, destination context and approved baseline | A shared relay uniquely attributes one actor. |
| Telemetry coverage | Collection sources, retention and missing periods | No alert means no activity occurred. |
Compare observations with the organization’s approved remote-access inventory. A documented administrator session and a new process under a web-service account deserve different interpretations. Record who authorized the tool, its expected host population and the normal account and connection pattern. An unexplained deviation is a reason to investigate, not proof of every stage of an intrusion.
Review persistence with the host owner
Microsoft describes layered persistence across cron, systemd, shell startup and other mechanisms. Review the relevant surfaces using the organization’s approved collection tools and preserve original artifacts. Determine ownership and change time where the evidence supports it. Avoid deleting suspicious files before responders have captured what they need.
Account for privilege level and identity changes in the timeline. A process running as a web account and a later root-owned service may be related, but that relationship needs evidence. Do not infer a particular privilege-escalation vulnerability merely from the final account. The article’s source observations are not a universal chain for every affected host.
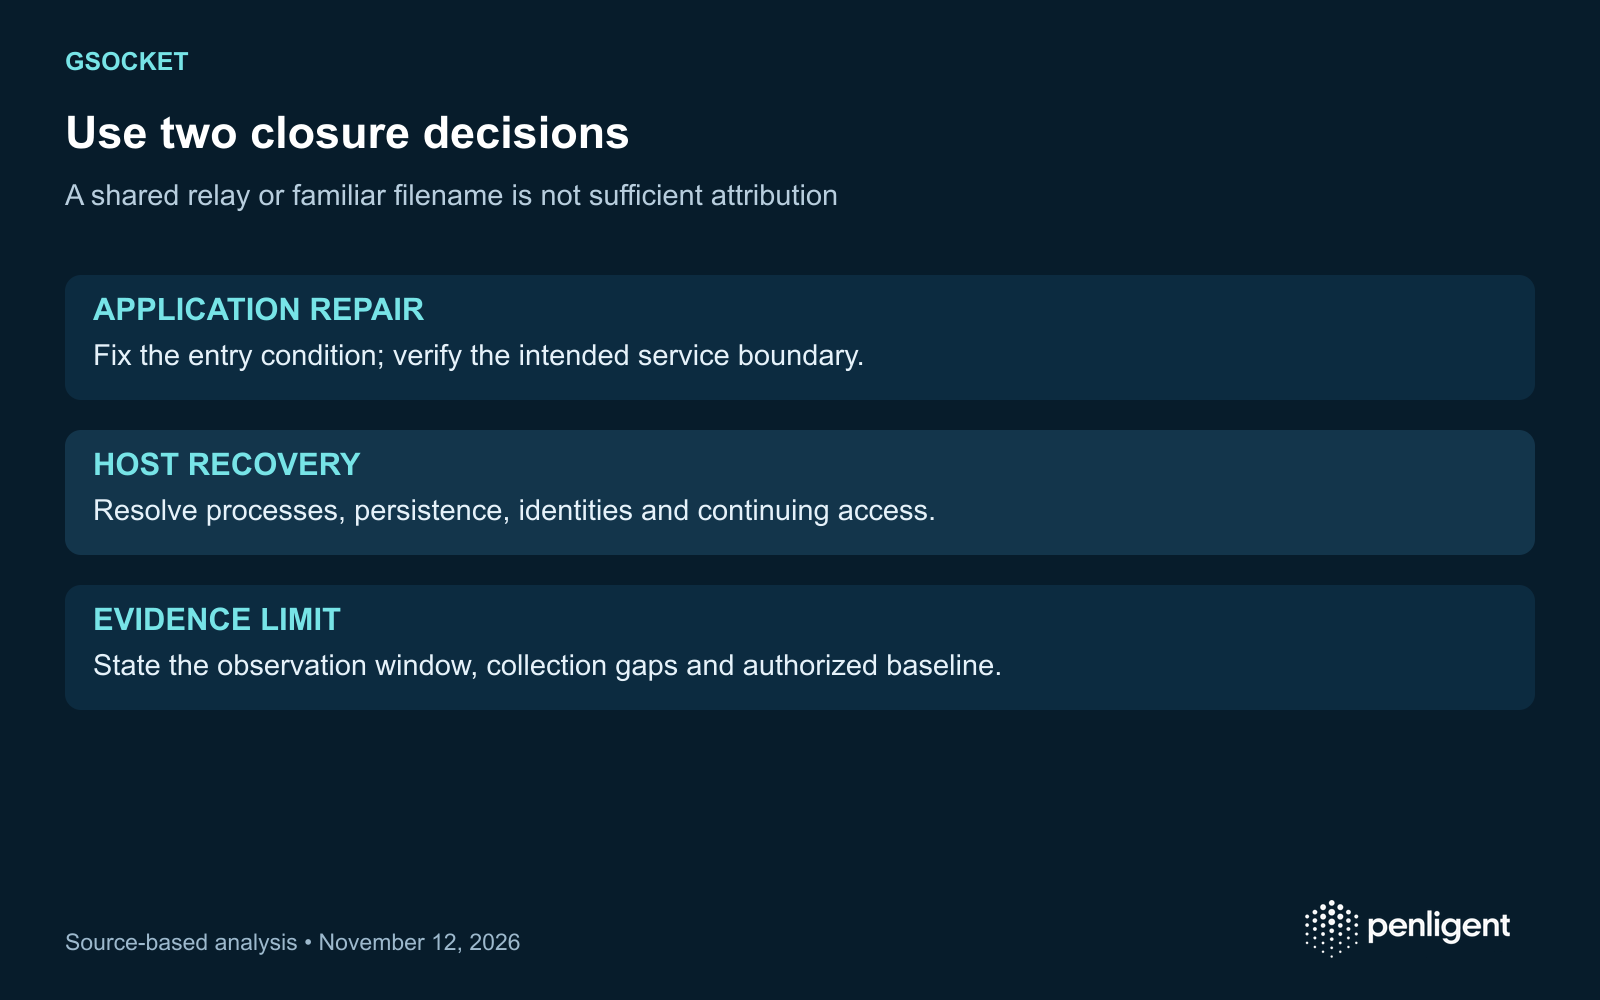
Close the application and host tracks separately
The application track identifies the entry condition, the corrective update or configuration and a controlled verification of the intended application boundary. The host track addresses unauthorized processes, persistence, credentials and continuing communication through the organization’s response or rebuild process. Track one can complete while track two still has unresolved evidence.
Application track: entry evidence, fix, active version, bounded retest
Host track: process, persistence, identity and outbound evidence
Authorized administration baseline
Containment / rebuild decision and owner
Credentials reviewed and dependent workloads
Observation window after remediation
Missing evidence and remaining exceptions
A quiet observation window has value only when the necessary collection is active. State which host and network signals were available and how long they were reviewed. Reconnection absence in one sensor does not establish that every alternate access path was removed.
Specify the right validation engagement
If purchasing a follow-up security assessment, state whether it covers the repaired application boundary, host recovery assurance or both. Require the provider to retain asset identity, expected behavior, observed result and limitations. A routine application scan should not be sold or accepted as proof that a compromised Linux host is clean.
Keep eBPF and other kernel-level investigation topics separate unless evidence in the actual case supports them. A general Linux persistence query is not sufficient reason to assert an eBPF rootkit. The useful report follows observed behavior and identifies what remains unknown.
Host incident response requires the relevant forensic and administrative evidence. An authorized application assessment using 펜리전트 should have a separate scope for the repaired entry surface.
The official Penligent 3.0 video below demonstrates the general product workflow. It illustrates product use; the article’s assessment proposals and source findings are evaluated separately.
Method: AI-assisted review of the linked primary sources, checked November 12, 2026, with an original assessment framework. No exploit, production target or customer environment was tested for this article.
 Korean
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Hindi
 Arabic
 Turkish
 Hebrew