
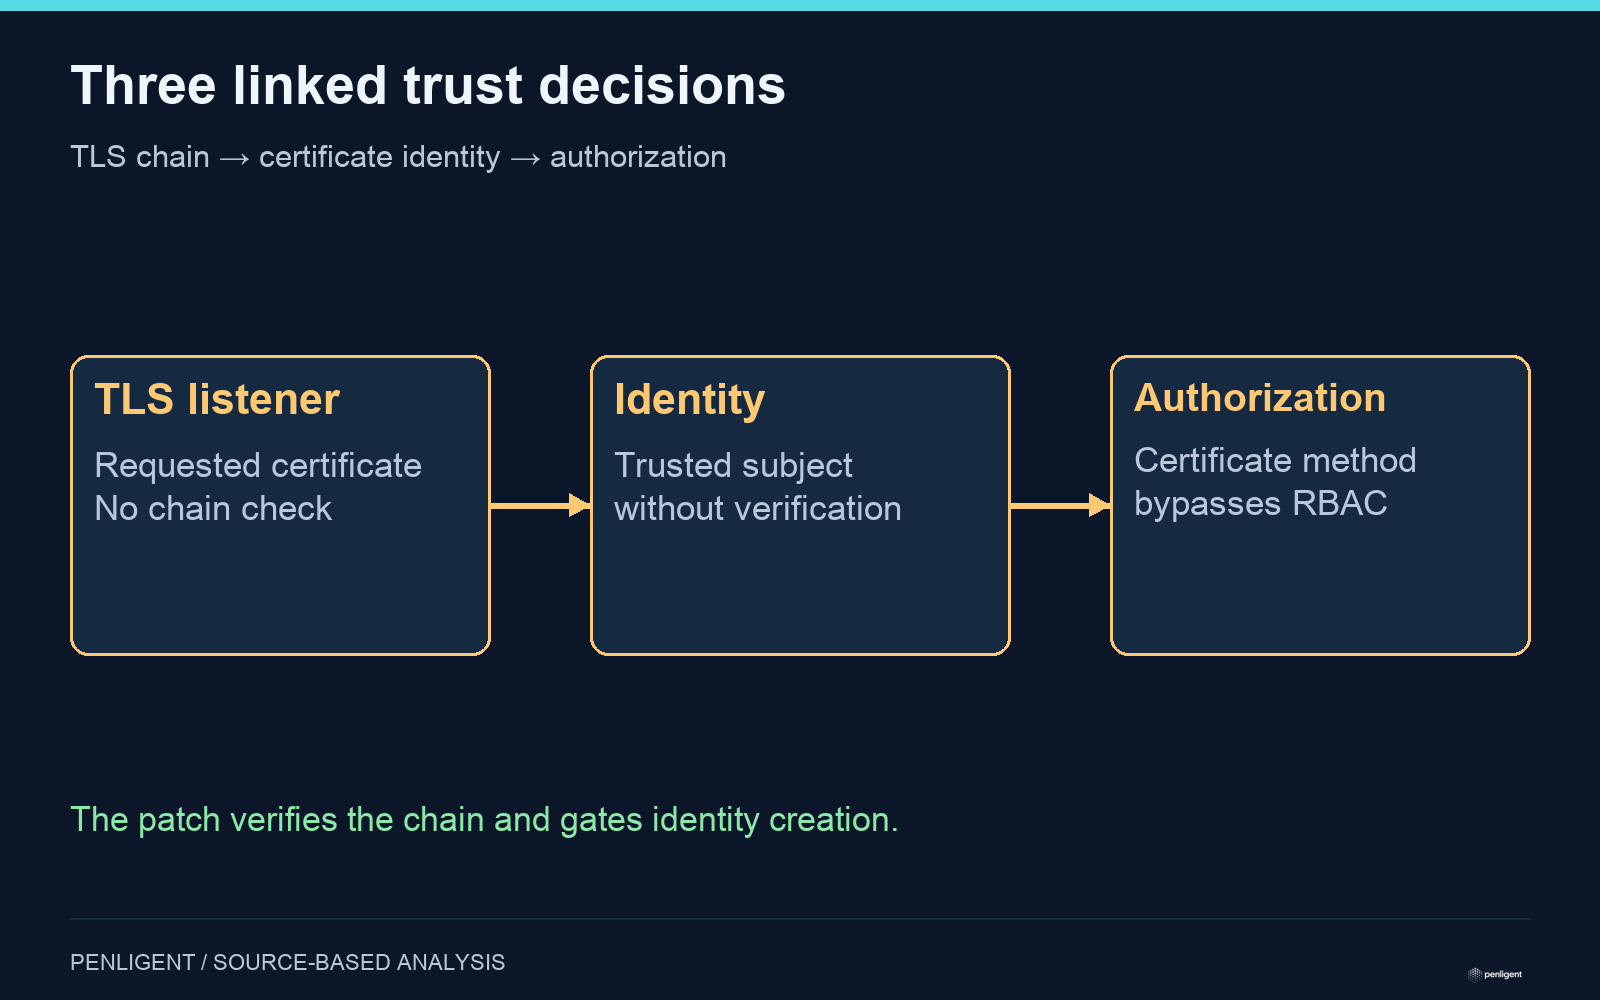
Miren Runtime versions before 0.11.1 have a cluster-control-plane authentication bypass, CVE-2026-75521. Bu maintainer advisory says the QUIC/HTTP3 RPC listener, on default port 8443, requested client certificates without verifying their chains. It then derived an identity from a presented certificate, while certificate identities bypassed RBAC. Upgrade to 0.11.1 or later and restart the server so the corrected listener takes effect.
Reachability and trust are separate questions
The advisory makes network reachability the exposure prerequisite. An Internet-accessible listener and a listener restricted to a management network have different reachable audiences, but the latter is still vulnerable to an actor with access to that network. Inventory the actual configured RPC port, ingress rules, published container ports and management paths rather than searching only for the default number.
A visible client certificate does not establish authenticated identity. The server must verify it against the intended cluster CA before using its subject. In this case, the authentication mistake crossed directly into authorization because the resulting certificate method had broad authority. Restricting the network is temporary containment; it does not repair either trust decision.
What the patch verifies—and what it intentionally still allows
Bu official patch changes the configured listener to verify a supplied client certificate. It also adds a non-empty VerifiedChains requirement in both RPC authenticators before creating a certificate identity. Checking only PeerCertificates would establish presentation, not verification. Both layers matter if future code changes accidentally weaken one of them.
The advisory explains that VerifyClientCertIfGiven admits certificate-free callers that authenticate with JWT/OIDC through the Authorization header. It is not the same policy as requiring every caller to present a client certificate. The patch also contains a required-client-certificate configuration case. Preserve the intended deployment mode rather than adopting an unrelated blanket TLS setting as a workaround.
| Caller in an owned test environment | Property to verify | Neden önemli |
|---|---|---|
| Approved CA-issued client certificate | Valid chain produces the intended certificate identity | Legitimate certificate access remains functional. |
| Presented certificate without a verified chain | No certificate identity or privileged operation is granted | Presentation alone must not create authorization. |
| No client certificate; valid intended JWT/OIDC path | Normal token authentication still works where configured | A security rollout must not silently remove the supported token mode. |
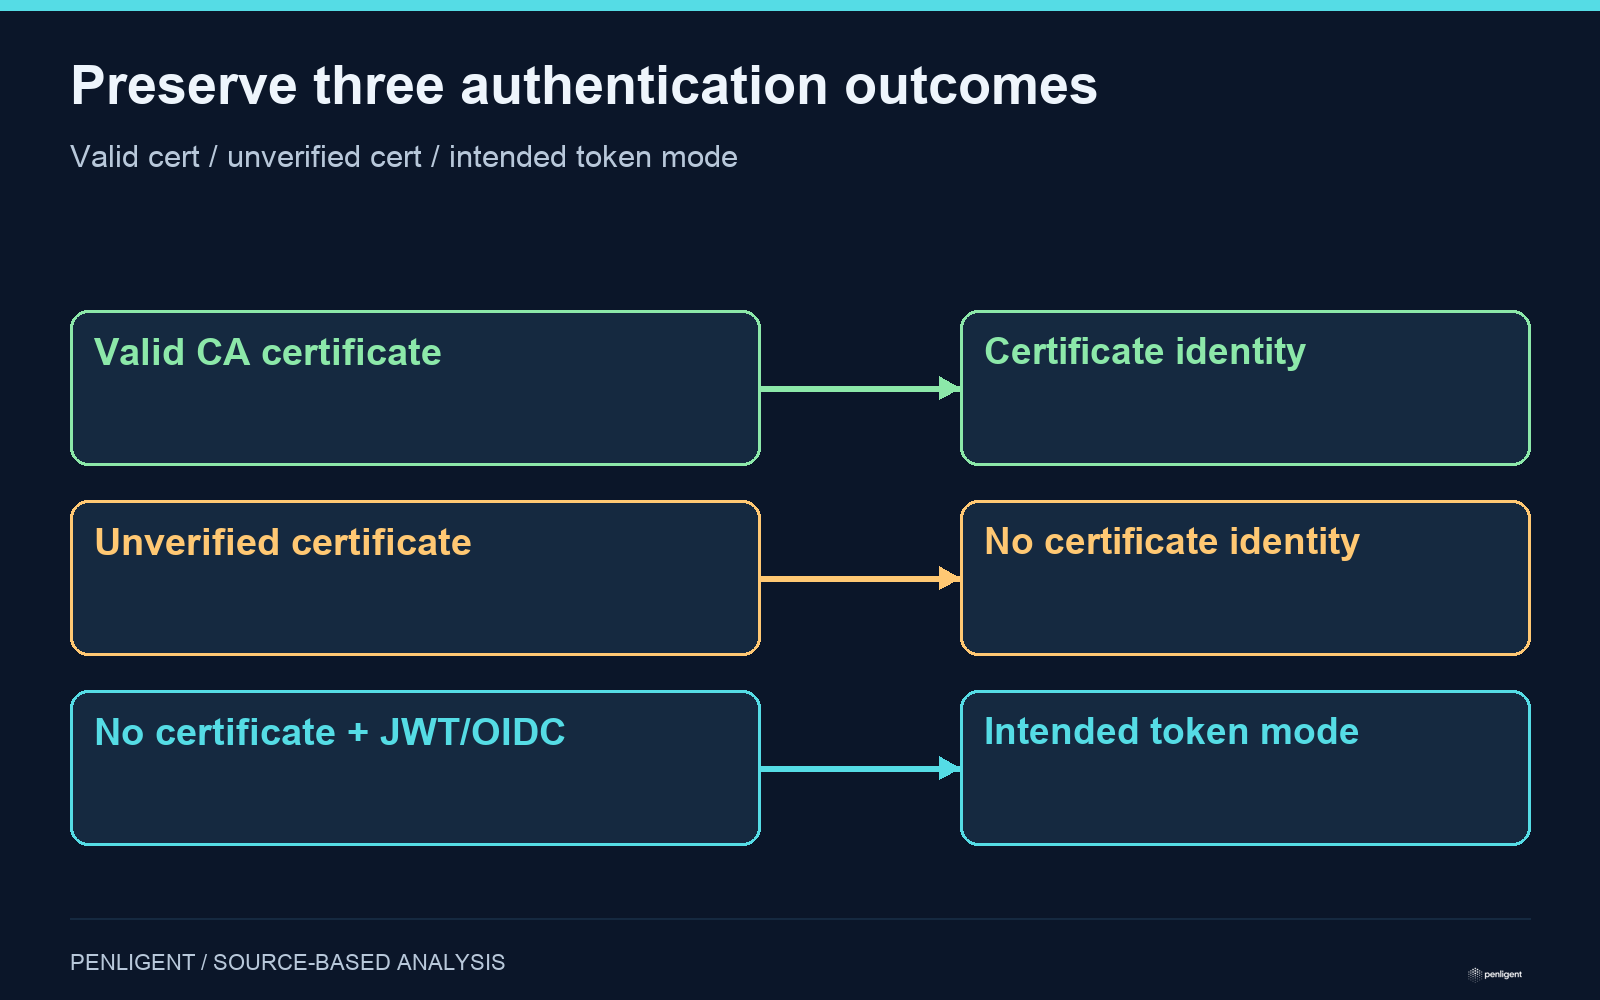
This is a proposed acceptance matrix derived from the patch, not a report of a live Miren test. Use the project’s regression tests and supported staging controls; do not manufacture certificates for an external cluster. Retain the listener mode, CA configuration, runtime version and restart evidence alongside the result.
Recovery extends beyond restarting the control plane
The maintainer says prior unauthorized RPC access cannot reliably be detected and recommends redeploying all applications and rotating credentials referenced in environment variables. That is stronger than simply checking a quiet access log. Record the recommendation, the environments covered, credential owners and replacement completion, with any exceptions clearly assigned.
A useful recovery ledger has one row per affected application: trusted deployment artifact, redeployment time, environment credential identifiers and issuer-side rotation evidence. Keep secret values out of the ledger. Review standing access and recent cluster changes using trusted administrative tooling. The advisory links a read-only audit helper; inspect its source and handling requirements before deciding to run it. No helper was executed for this article.
Track containment, repair and recovery independently
Close network containment only after the intended ingress audience is verified. Close the code change after the patched runtime is active and authentication modes pass their expected checks. Close application recovery and credential actions from their own evidence. A fixed listener cannot undo an action completed through previously obtained cluster authority, and absent telemetry cannot prove no earlier access occurred.
The following Penligent 3.0 video is a general product workflow demonstration. It is not evidence of exploitation or proof that this vulnerability was remediated.
Methodology, November 19, 2026: AI-assisted drafting with agent verification against the linked primary records and source changes. The deployment decisions and proposed acceptance checks are analysis. No exploit was executed and no first-hand incident response is claimed.
 Turkish
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Hebrew