
CVE-2026-119351 can cause a Next.js application to reuse cached content across root-parameter values when Cache Components and a particular nested 'use cache' pattern are present. The maintainer advisory lists next versions 16.2.0 through 16.4.4 as affected and 16.4.5 as fixed. For applications that use a root parameter to separate tenants, installation evidence should be followed by an isolation test using synthetic data.
Identify what the root parameter protects
A root parameter is not necessarily a tenant identifier. It may select a locale, site or other routing context. First map the parameter to the data returned by the cached function. A wrong language response and exposure of a private tenant record have different consequences, even when the underlying cache dependency bug is the same.
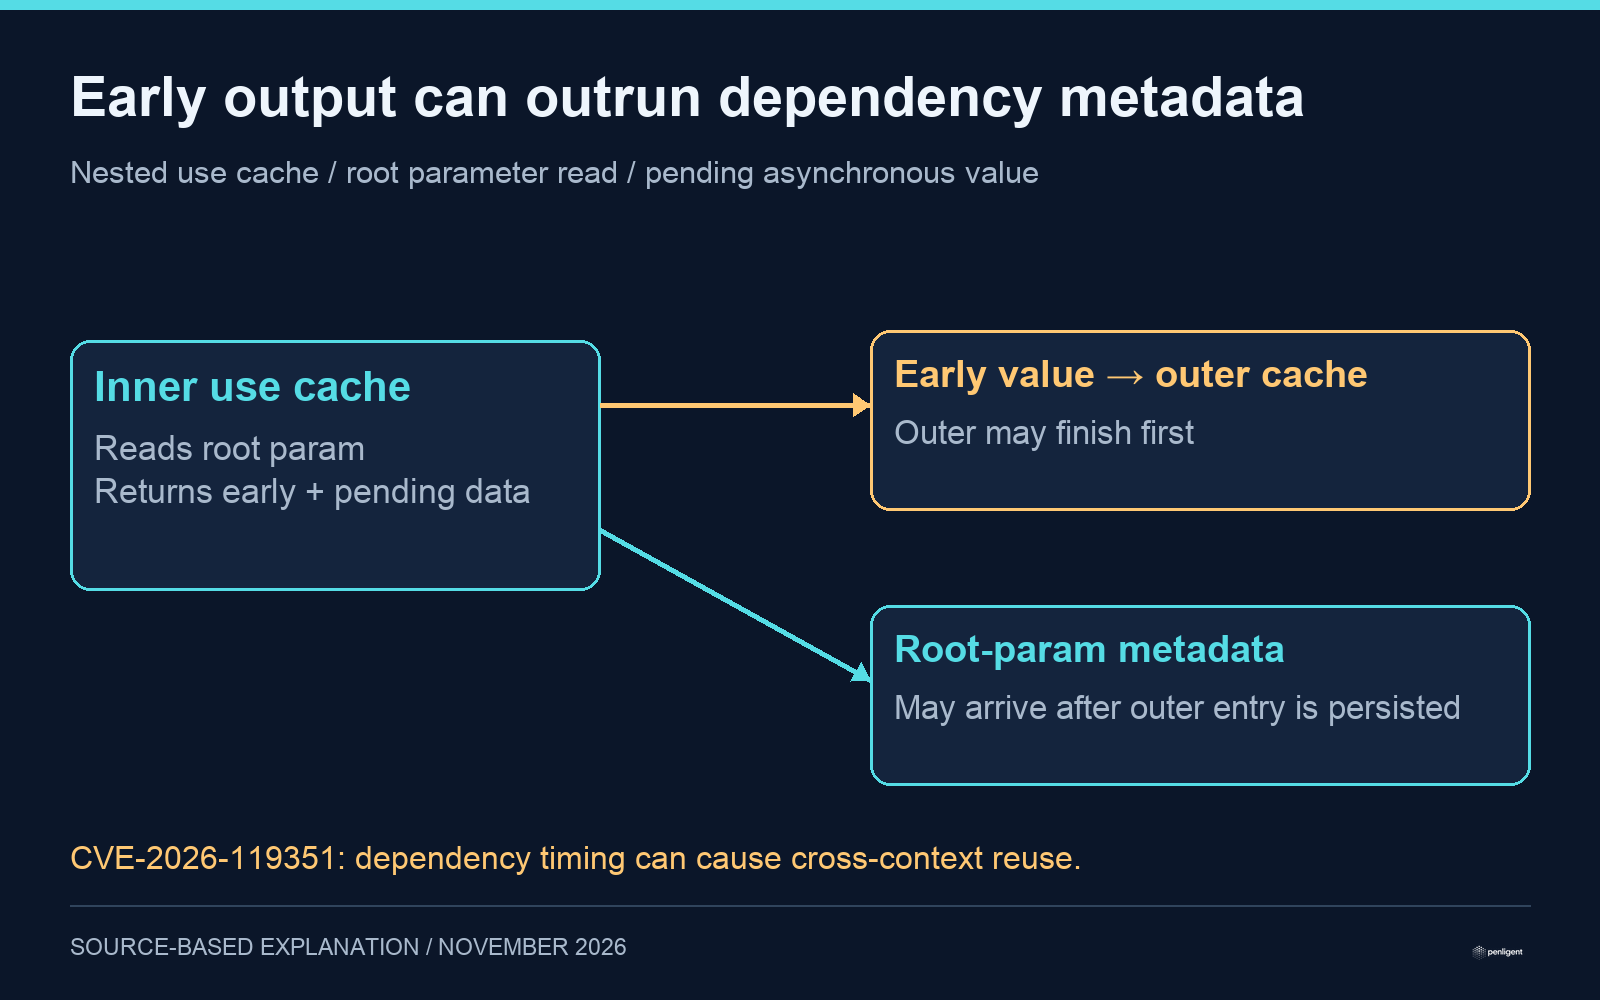
The advisory describes an inner cached function that reads a root parameter and returns a value containing pending promises. React Flight can deliver the ready portion before the inner cache has published all its root-parameter dependencies. If the outer function finishes in that interval, its entry can omit the dependency and be reused across values. Tag invalidation and nested cache lifetimes may also be missed. The attacker does not choose arbitrary injected response content; the incorrectly reused content is generated by the application.
Do not confuse two cache disclosures
| Issue | Relevant application shape | Affected range and fix |
|---|---|---|
| CVE-2026-119351 | Nested public use cache calls; inner root-param read; early data alongside pending asynchronous data | 16.2.0–16.4.4; fixed in 16.4.5 |
| CVE-2026-119790 | Same public cached function called directly and through unstable_cache; root-param read; concurrent first fill after process start | 16.3.0–16.4.4; fixed in 16.4.5 |
The second row comes from its separate maintainer advisory. Avoiding the unsupported use cache içeride unstable_cache() combination is its complete documented workaround. That does not establish a workaround for the delayed-metadata issue in the first row. Likewise, removing a cold-start race test from a test plan does not make the first issue disappear.
Bu November release post covers additional issues and identifies 16.4.5 and 15.5.29 as release targets for their respective supported branches. Do not infer that both CVEs affect 15.x merely because that branch received a security release. Use each advisory’s package range for applicability. The release post is dated November 3, whereas the GitHub advisory for CVE-2026-119351 was published November 17; neither date should be rewritten as a first disclosure on November 18.
Build a canary test around your tenant boundary
Use an owned staging environment with two synthetic routing contexts, A and B. Put a distinct non-sensitive marker in each expected response, such as tenant-a-canary ve tenant-b-canary. Ensure the accounts, fixtures and route parameters all correspond to the intended contexts. Keep security-significant data out of the test.
| Test condition | What to observe | Failure meaning |
|---|---|---|
| First fill, then warm reads for A and B | Each context retains only its own marker | A wrong marker establishes an isolation failure in this tested path |
| Early and delayed values in the nested return | The outer result preserves the correct routing dependency | Asynchronous response shape needs investigation |
| Concurrent first fills after a controlled restart | Direct and wrapped call paths remain isolated | The related cold-start pattern may still be reachable |
| Application-supported tag invalidation | The intended context refreshes with the new fixture | Stale data may have a different cache cause; do not automatically assign a CVE |
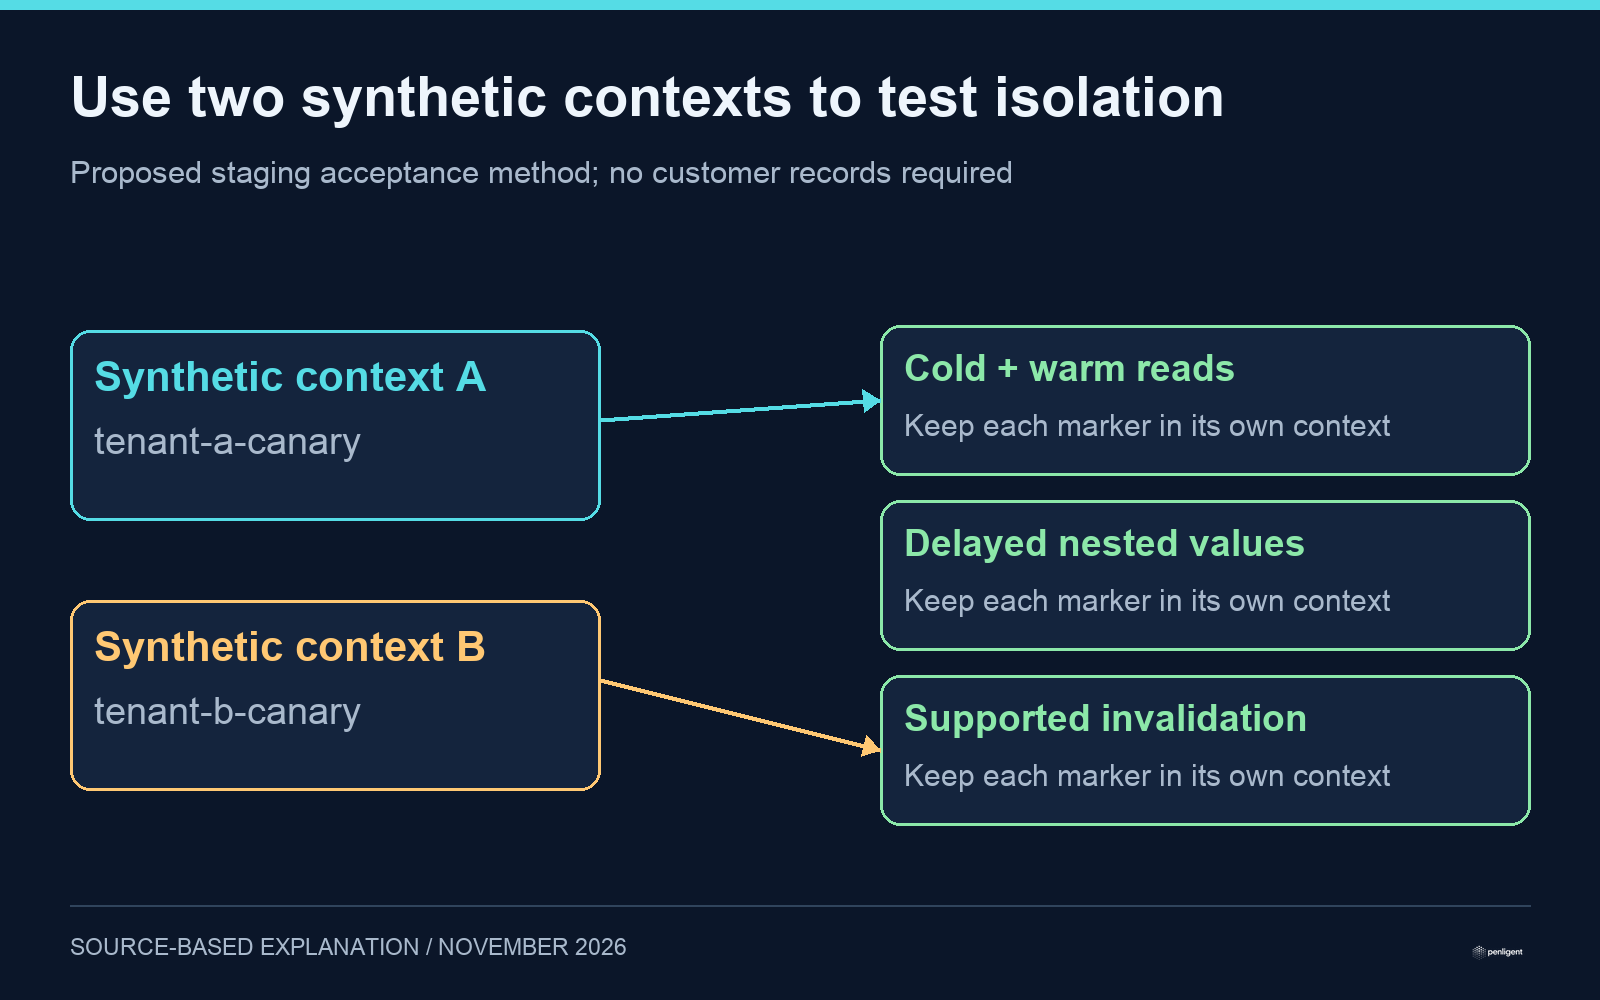
This is an acceptance-test design, not a claim that we executed the application. Record the application commit, installed next version, deployment identifier, cache configuration and observations. Repeat across relevant deployment nodes or cache namespaces; a successful test on one fresh instance does not describe every warm instance.
Ship the fixed code and retire stale evidence
Update the dependency and lockfile through the project’s supported process, rebuild and redeploy, then confirm the version used by the running deployment. Review existing cached content as part of the change plan. A fix stops the vulnerable behavior in the updated code; it does not, by itself, prove that every response previously persisted outside the application has disappeared.
If a marker crosses contexts, preserve the precise request context and deployment evidence without collecting another customer’s data. Investigate application authorization and other cache layers as well. The advisory is a useful hypothesis, while the test result establishes only what that particular environment returned.
For teams organizing an authorized Penligent assessment, synthetic tenancy fixtures and explicit expected responses make cache findings easier to verify and retest. No product demonstration establishes coverage of these exact Next.js conditions.
Method: maintainer advisory, patch and release review checked November 18, 2026. AI assisted drafting; agent validation checked the claims. The canary matrix is a proposed defensive method, not a first-hand exploitation result. The Penligent 3.0 video below demonstrates a general workflow.
 Turkish
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Hebrew