
CVE-2026-123007 affects NGINX configurations that process HTTP/2 traffic. Die NGINX security list identifies open-source 1.31.9 and 1.30.7 as fixed branches. The F5-authored CVE record describes flow-control memory corruption in the data plane, typically followed by a worker segmentation fault. Remote code execution additionally depends on ASLR being disabled or bypassed. The nickname nginx2root is not a guarantee of root access.
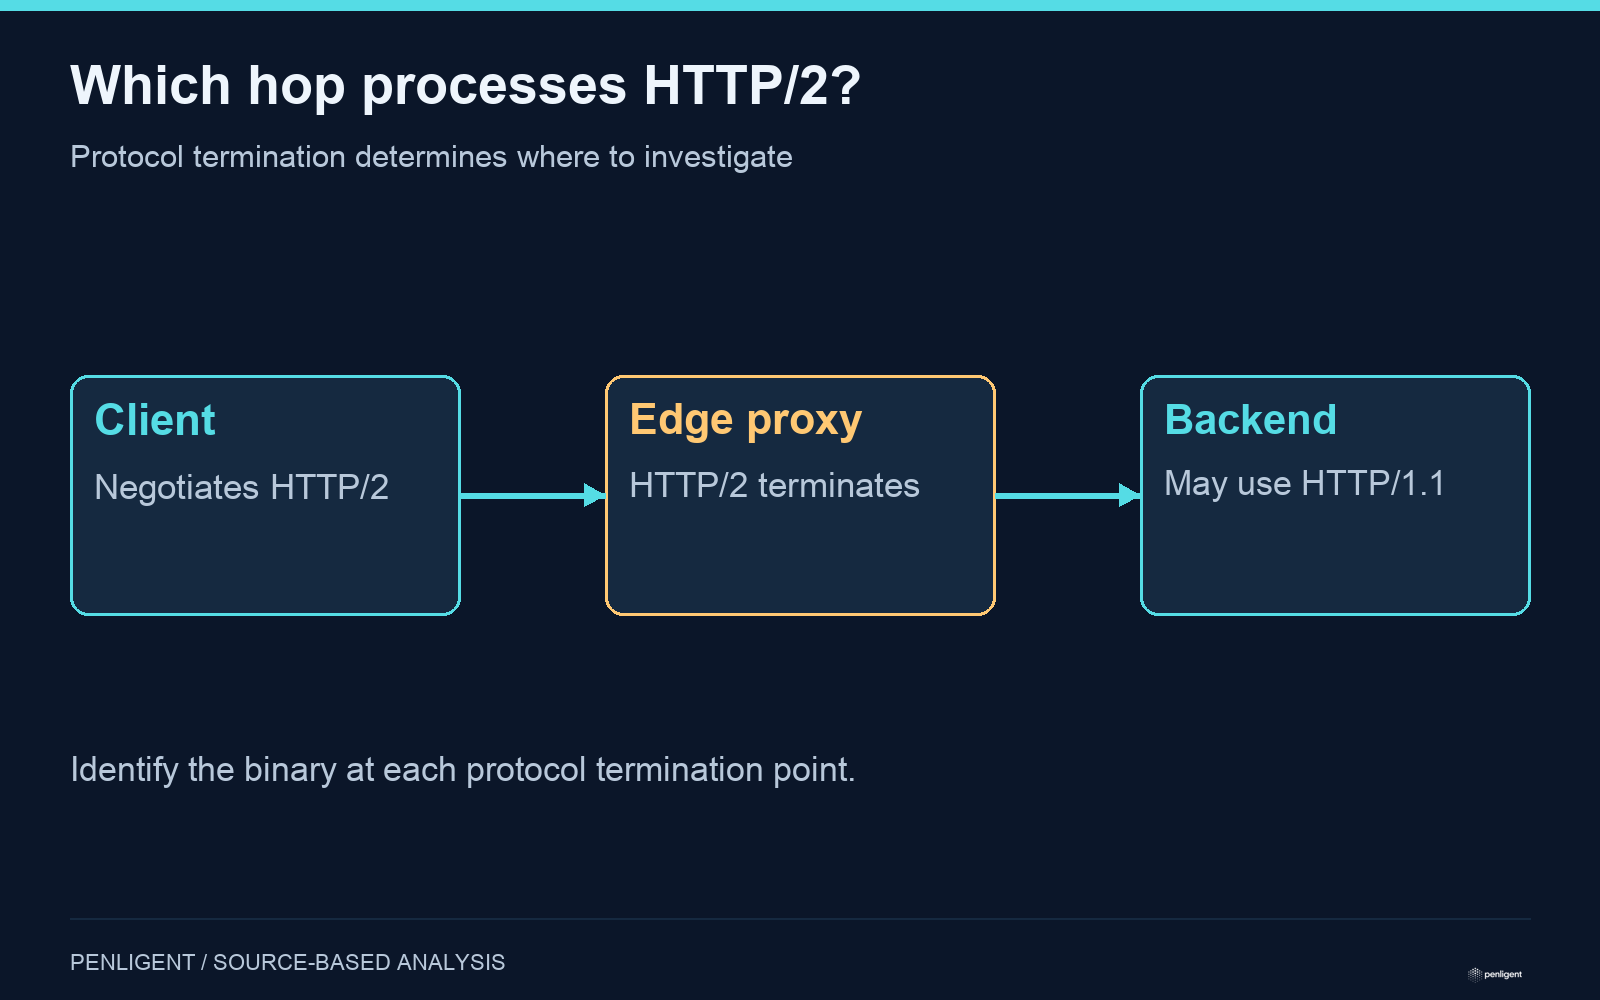
Find the process that terminates HTTP/2
A public hostname can pass through a CDN, load balancer, ingress layer and an application-side proxy. Identify which of those components actually negotiates and processes HTTP/2. A scanner that observes HTTP/2 at the edge has not identified the software behind every hop. Conversely, an HTTP/1.1 backend does not remove exposure from a vulnerable HTTP/2-facing proxy in front of it.
Record the listener, effective configuration, running NGINX binary, package origin and workload owner together. Include internal HTTP/2 listeners and embedded or containerized copies. The CVE is a data-plane issue; it does not require access to the NGINX management plane. Do not use a closed administration port as the principal exclusion criterion.
Match the fix to the software supplier
| Deployment source | Evidence checked November 19 | How to use it |
|---|---|---|
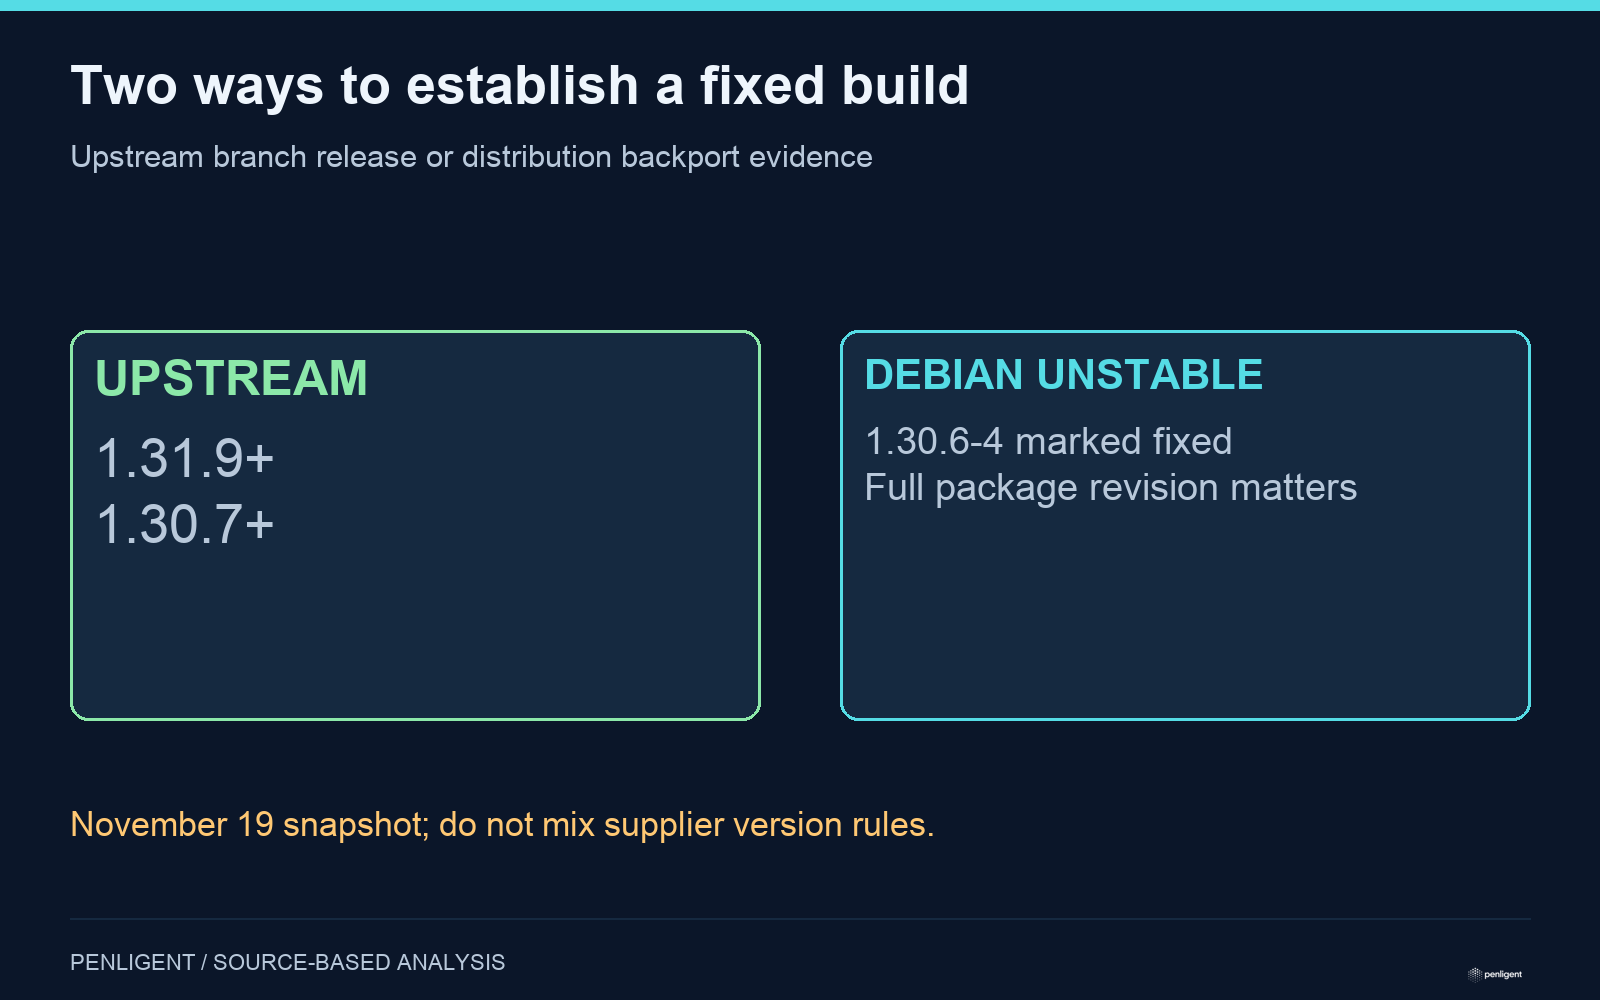
| NGINX Open Source | Official list: fixed in 1.31.9+ and 1.30.7+; vulnerable path listed from 1.9.5 | Use the supported branch and verify the deployed process contains the corrected build. |
| NGINX Plus | CVE lists affected ranges ending before 37.3.0.1 and 37.0.8.1 in the corresponding branches | Consult the F5 branch matrix; do not map an open-source number onto Plus. |
| Debian | Tracker marks unstable 1.30.6-4 fixed; listed bookworm and trixie security packages remain vulnerable at this check | A distribution backport can retain an older upstream base. Check the full Debian revision and release status. |
| Ubuntu | Tracker lists 16.04 through 26.10 vulnerable at this check and 14.04 not affected | Do not invent an Ubuntu fixed package from the upstream release. Recheck the tracker for the installed release. |
This is a time-bounded comparison, not a recommendation to move a stable Debian host to unstable or to replace a supported distribution package with an arbitrary binary. The Debian row shows why a numeric rule such as “everything below 1.30.7 is unpatched” is inadequate. Supplier status and the complete package revision are part of the evidence. Software outside evaluated support ranges needs a separate supplier decision.
Treat the November patch set as a configuration review
The same NGINX release set addresses other issues, including resolver use-after-free CVE-2026-123634 and HTTP/2 use-after-free CVE-2026-123633. They are distinct defects with distinct starting versions. Keep them in one patch plan when the same running binary is replaced, but do not infer that disabling HTTP/2 resolves resolver, stream, mail or other unrelated paths. The official security list supplies the applicability boundaries.
Keep four closure states visible
| State | Required record | What it does not prove |
|---|---|---|
| Exposure identified | HTTP/2 termination point, relevant binary and package source | That an observed crash was exploitation. |
| Containment applied | Approved protocol or network restriction and normal-service impact | That the vulnerable code was corrected. |
| Fixed deployment active | Supplier remediation, running process and rollout evidence | That every old worker or replica was replaced. |
| Historical review complete | Available worker crash, traffic and host evidence with retention limits | That missing telemetry proves no prior access. |
If HTTP/2 is temporarily disabled through supported configuration, verify every intended listener and the effect on clients. Treat this as a change requiring normal service validation, not as a universal fix for the entire patch set. Retain ASLR protections; their presence does not justify leaving memory corruption unpatched.
Verify normal traffic without sending an exploit
In an owned staging environment, confirm the intended HTTP/1.1 and HTTP/2 behavior after the update, including upstream routing and certificate handling. Record the package revision, image digest, active workers and request results. During production rollout, account for every replica and any old worker generation that remains in service. A successful package installation alone is insufficient.
For an authorized assessment using Sträflich, attach the listener map and supplier patch evidence to the scope. A generic product demonstration or a clean availability check does not establish that the exact vulnerable code path has been corrected.
The following Penligent 3.0 video is a general product workflow demonstration. It is not evidence of exploitation or proof that this vulnerability was remediated.
Methodology, November 19, 2026: AI-assisted drafting with agent verification against the linked primary records and source changes. The deployment decisions and proposed acceptance checks are analysis. No exploit was executed and no first-hand incident response is claimed.
 German
 English
 French
 Spanish
 Portuguese
 Japanese
 Korean
 Hindi
 Arabic
 Turkish
 Hebrew