
Penetration testing as a service should make validated security testing easier to repeat, govern and retest. It should not turn a vulnerability scanner into a pentest merely by adding a dashboard, an AI summary or a recurring schedule.
For a buyer, the central question is operational: can the service test the security properties that matter to the business, stay within an authorized scope, preserve reproducible evidence and help engineering confirm that a fix works? The answer depends on the delivery model, the people involved and the controls built around execution.
What PTaaS can mean
| Delivery model | Typical capability | Primary buying risk |
|---|---|---|
| Scanner subscription | Scheduled discovery of known vulnerabilities and common misconfigurations | Marketing language may imply manual reasoning that is not included |
| Automated pentest platform | Multi-step testing, tool orchestration and evidence capture | Autonomy may exceed the quality of scope controls and conclusions |
| Platform plus human validation | Automation with analyst review, triage and retesting | Human involvement may be limited to report editing rather than technical verification |
| Managed continuous testing service | Ongoing testing aligned to releases, assets and remediation workflows | Coverage can become opaque unless each testing cycle has explicit objectives |
Explore Penligent for authorized security testing
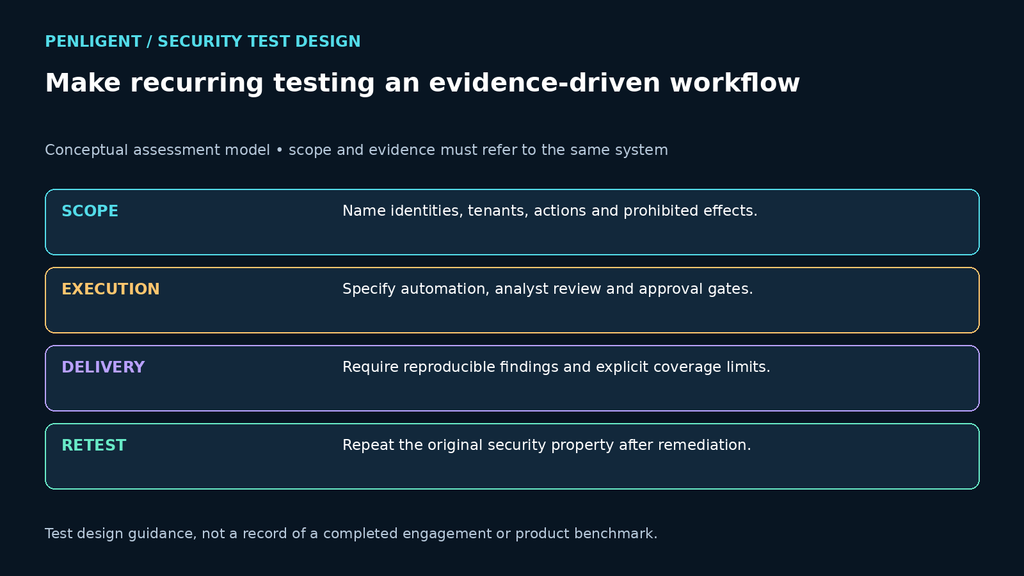
Ask the provider to name the operating model in the proposal. Terms such as continuous, autonomous and expert-validated are not acceptance criteria. They need to be translated into actions, approval gates, artifacts and response times.
Start with security properties, not URLs
A useful scope describes what must remain secure. A list of hosts is necessary, but it rarely captures the business risk of a SaaS or API. Add identities, roles, tenants, integrations, data classes and important state transitions.
| Scope element | Question the service must answer | Expected evidence |
|---|---|---|
| Tenant isolation | Can one tenant read or change another tenant’s objects? | Identity context, object ownership, request and response differences |
| Authentication lifecycle | Do enrollment, recovery, rotation and revocation behave consistently? | Token state, timestamps, account state and audit events |
| 권한 부여 | Are UI, API and background jobs enforcing the same policy? | Role matrix and server-side decision evidence |
| Business workflow | Can replay, race or sequence manipulation create an unauthorized outcome? | Preconditions, state transitions and final business impact |
| Cloud boundary | Can application access cross into management, metadata or adjacent accounts? | Resource identity, policy decision and provider-safe validation |
NIST SP 800-115 remains a useful foundation for planning tests, conducting them and analyzing findings. The OWASP 웹 보안 테스트 가이드 provides a broad testing framework, while the OWASP ASVS can help define application security requirements. A provider may use other methods, but it should be able to map its work to an explicit test plan.
Evidence is the real product
A dashboard count is not a security outcome. Require every accepted finding to identify the authorized target, identity, preconditions, violated security property, reproducible observation, impact, remediation direction and safe retest method.
- Reproducibility: an engineer can repeat the observation without guessing what the tester did.
- Attribution: the report distinguishes the vulnerable component or policy from downstream symptoms.
- State: the finding records the role, tenant, entitlement and workflow state required.
- 안전: evidence does not depend on destructive actions or unnecessary access to customer data.
- Retestability: the same invariant and evidence path can verify the correction.
During a trial, seed a small number of known defects in an isolated environment. Include a straightforward technical flaw, an authorization error, a stateful business-logic defect and a negative control. Measure validated findings, unsupported claims, engineer reproduction success and time to retest. Do not score a platform only by the number of alerts it emits.
Test the authorization and stop controls
Before enabling recurring execution, perform acceptance tests against the service itself:
- Reference an out-of-scope hostname and confirm that the request is blocked.
- Attempt an action above the approved risk level and confirm that approval is required.
- Stop a running engagement and verify that workers, queued jobs and callbacks terminate.
- Rotate a test credential and confirm the previous secret is invalidated and deleted.
- Export the audit trail needed to reconstruct who authorized and performed each action.
A provider’s claim that a human is in the loop is incomplete. The proposal should identify where human approval occurs, who can override it and what happens when the platform loses contact with its control plane.
Define the testing cadence
| 트리거 | Appropriate testing action | Not sufficient by itself |
|---|---|---|
| Major release | Target changed trust boundaries and regression-test critical workflows | Re-running the same generic scan profile |
| New integration | Test secrets, delegated authorization, callbacks and failure handling | Checking only the integration’s public endpoint |
| Critical vulnerability | Inventory exposure, validate prerequisites and confirm remediation | Matching a version string without active-runtime evidence |
| Periodic assurance | Rotate focus across identity, API, business logic, cloud and client surfaces | Reporting that no new CVEs were found |
| After remediation | Repeat the original security invariant and examine regression risk | Closing a ticket because a package was installed |
Data handling and deployment
PTaaS can process credentials, source code, HTTP bodies, customer-like records, logs and vulnerability evidence. Document where each data class is collected, processed, retained and deleted. A local worker does not prove that prompts, telemetry or findings remain local.
Ask which model providers and subprocessors receive data, whether customer content is used for training, how secrets are isolated, what regions are available, how browser sessions are separated and how incident notifications work. Contract language and product architecture should describe the same deployment tier.
Calculate total operating cost
Compare the cost of a validated and retested finding, not just the subscription. Include onboarding, staging preparation, model or compute usage, analyst review, false-positive rejection, evidence repair, ticket integration, retesting and internal coordination.
| Cost driver | Procurement question |
|---|---|
| Scope unit | Is price based on applications, hosts, endpoints, domains, testers, tests or usage? |
| Testing frequency | What triggers a new test, and are retests counted separately? |
| Human validation | Which tier includes technical review, and how much review is guaranteed? |
| Integrations | Are SSO, ticketing, CI/CD and API access included? |
| Overages | What happens when a run loops, scope expands or usage exceeds the plan? |
| Exit | Can findings, evidence and audit history be exported in usable formats? |
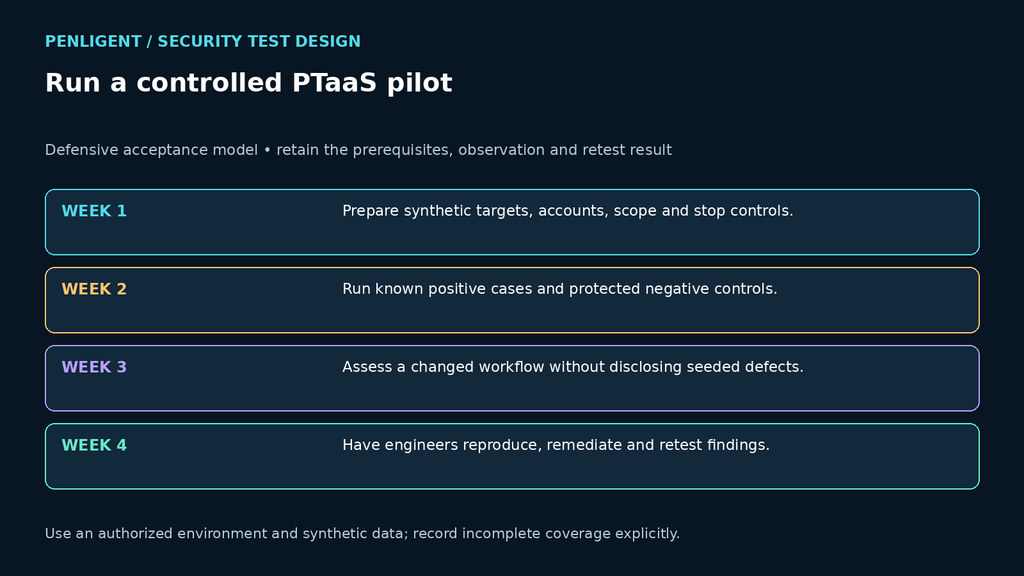
A 30-day PTaaS pilot
- Week 1: configure synthetic targets, identities, allowlists, approval gates and data-retention settings.
- Week 2: run known positive and negative cases, including one business-logic defect.
- Week 3: perform a blind assessment of a changed workflow and evaluate the evidence.
- Week 4: have engineers reproduce two findings, remediate them and request retests.
The purchase decision should be based on scope fidelity, validated finding quality, control behavior, developer acceptance, retest success and total cost. Penligent’s AI pentesting workflow can be assessed with the same pilot rather than receiving a vendor-specific exception.
Explore Penligent for authorized security testing
Make the purchase measurable
Buy PTaaS when it turns authorized testing into a repeatable engineering workflow with evidence and retesting. Do not buy it merely because it promises continuous scanning, autonomous execution or a larger finding count. The service is valuable when it reduces the time from a real security weakness to an accepted fix without weakening control over the test.
The following Penligent overview introduces a general authorized testing workflow. It does not demonstrate that every assessment capability discussed in this guide is included in a particular product plan.
 Korean
 English
 German
 French
 Spanish
 Portuguese
 Japanese
 Hindi
 Arabic
 Turkish
 Hebrew