Pages 03–06, 17
Overview, scope & methodology
Document purpose, system boundaries, test roles and exclusions, plus the scope and methodology appendix.
Free report sample
See how a web application and API penetration test report connects findings, evidence and remediation. A practical reference for security, engineering and review teams.
Sign in or create a free Penligent account, then select Download Sample Pentest Report in the homepage report section. The 19-page PDF is in English.
Actual pages from the sample PDF. Open an image to read it at a larger size.
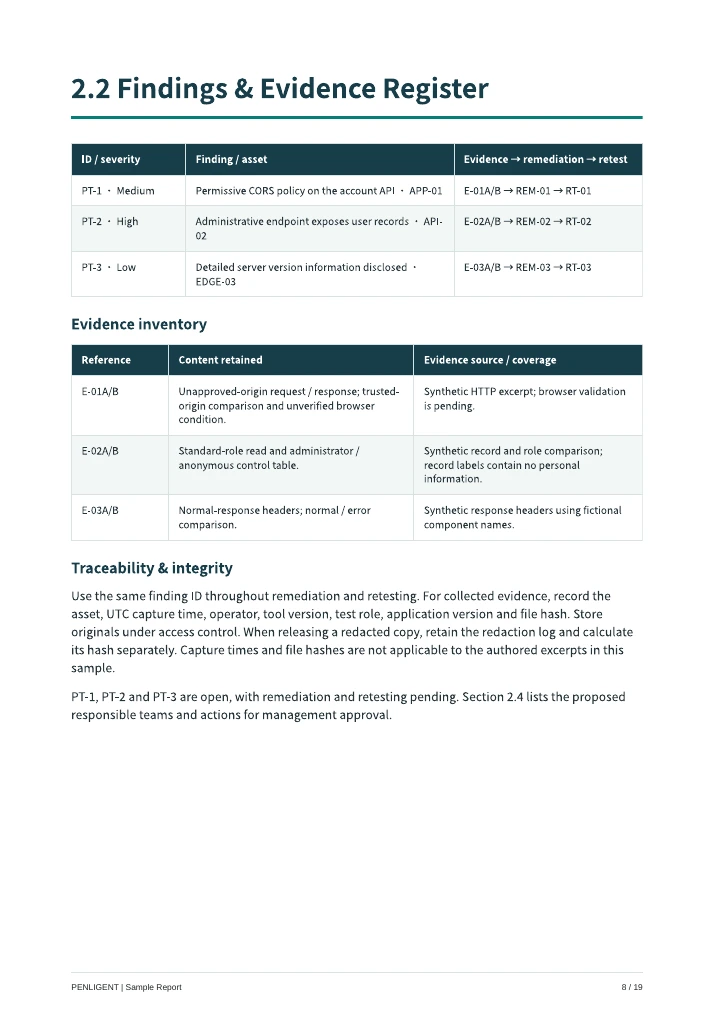
Document purpose, system boundaries, test roles and exclusions, plus the scope and methodology appendix.
Three fictional findings: permissive CORS, unauthorized access to administrative records, and version disclosure. Includes qualitative severity ratings and evidence references.
Suggested fixes, management response fields and retest criteria. These are scenario records; no live remediation or retesting was performed.
A vulnerability coverage appendix, glossary and references explain the scope and limits of the sample.
For technical review
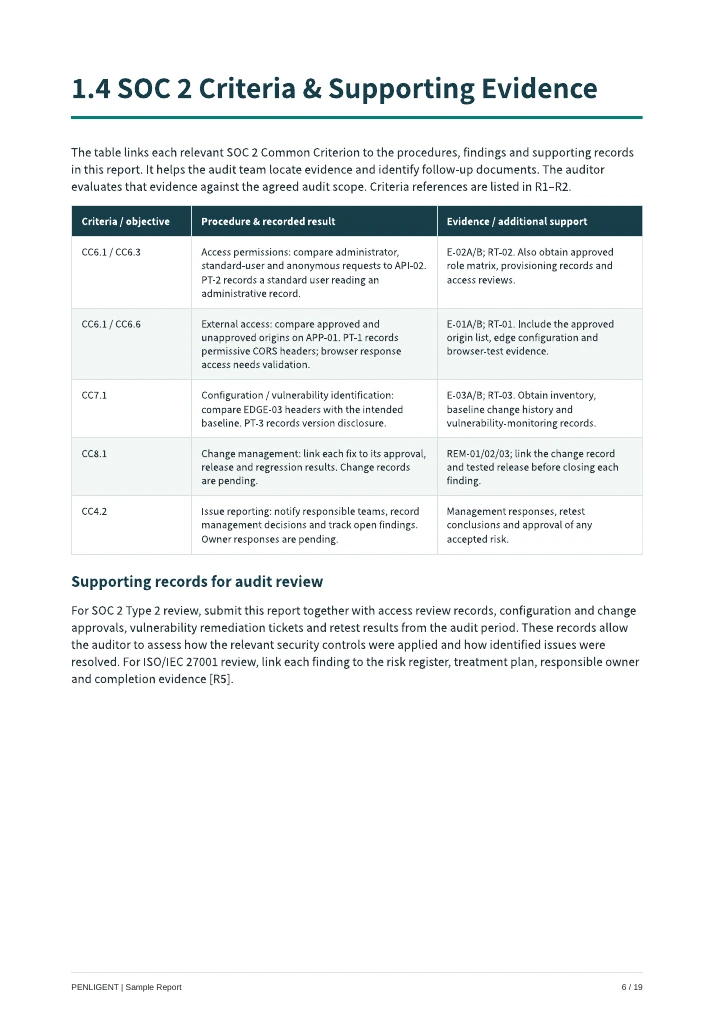
Page 6 maps selected SOC 2 Common Criteria to the sample’s procedures, findings and supporting records. It also identifies additional evidence an auditor would need to assess.
The report describes linking findings to a risk register, treatment plan, responsible owner and completion evidence. This is risk-treatment context, not a comprehensive ISO/IEC 27001 control mapping.
This is a penetration test report sample based on a fictional scenario. It is not a CPA-issued SOC 2 Type I/Type II report, an audit opinion or an ISO/IEC 27001 certificate. It does not establish compliance or guarantee acceptance by any auditor.
No. It is a penetration test report sample with selected SOC 2 references. It is not a SOC 2 Type I/Type II audit report or an auditor’s opinion.
No. The download is a finished PDF sample, not an editable Word or spreadsheet template. Use it to understand the structure of a report.
Sign in or create a free Penligent account, then select Download Sample Pentest Report in the homepage report section. The 19-page PDF is in English.
No. The 19-page English PDF uses a fictional application and synthetic evidence. It does not describe a live engagement, and no customer approval or independent assessor sign-off has been issued.
Explore the complete sample, from the executive summary to evidence and retest records.